
Resources
Blog
Resource Library
May 11, 2026
How to Meet Cyber Insurance Requirements
Learn what cyber insurance requirements insurers expect, how to close third-party risk gaps, and how continuous monitoring strengthens your coverage.
May 11, 2026
Supply Chain Security Needs Real-Time Visibility
Learn why supply chain security demands real-time visibility and explore 7 best practices to protect your organization from third-party cyber threats.
May 11, 2026
Building a Vendor Compliance Dashboard for Auditors
Build a compliance dashboard auditors actually trust. Learn how real-time vendor monitoring beats outdated quarterly assessments.
May 11, 2026
The Four Questionnaires Your TPRM Team Is Managing (And Struggling to Keep Up With)
The questionnaire is the workhorse of third-party risk management. But not all questionnaires are the same and treating them like they are is one of the reasons TPRM programs fall behind. Here’s a clear-eyed look at the four types your team is juggling. 1. Initial / Intake Questionnaires Also called: Inherent Risk Questionnaire (IRQ), Vendor
May 8, 2026
Passive DNS Explained: Vendor and Threat Infrastructure
Passive DNS Explained: Vendor and Threat Infrastructure
May 8, 2026
What Is Typosquatting? Attack Types and Prevention
Typosquatting is a domain attack using misspelled, look-alike URLs to trick users. Learn the types, real examples, and how to prevent it.
May 4, 2026
How to Run a Supply Chain Risk Assessment
Learn how to run a supply chain risk assessment, identify supplier vulnerabilities, and build a program that stays current between reviews.
May 4, 2026
Cybersecurity Questionnaire in the Age of AI
AI is reshaping the cybersecurity questionnaire. Learn how to combine faster assessments with continuous monitoring for real-time vendor visibility.
May 4, 2026
Cyber Risk Quantification Models
Learn how cyber risk quantification models help organizations express security risks in financial terms. Compare FAIR, NIST, and ISO frameworks.
May 4, 2026
Amanda Smith Earns Spot on the 2026 Women of the Channel List, Showcasing SecurityScorecard’s Channel Leadership
NEW YORK– May 4, 2026— SecurityScorecard, the global leader in threat-informed third-party risk management (TPRM), today announced that CRN®, a brand of The Channel Company, has recognized Amanda Smith, Director of Public Sector Channel at SecurityScorecard, on the prestigious Women of the Channel list for 2026. This annual CRN list celebrates women from vendors, distributors,
April 29, 2026
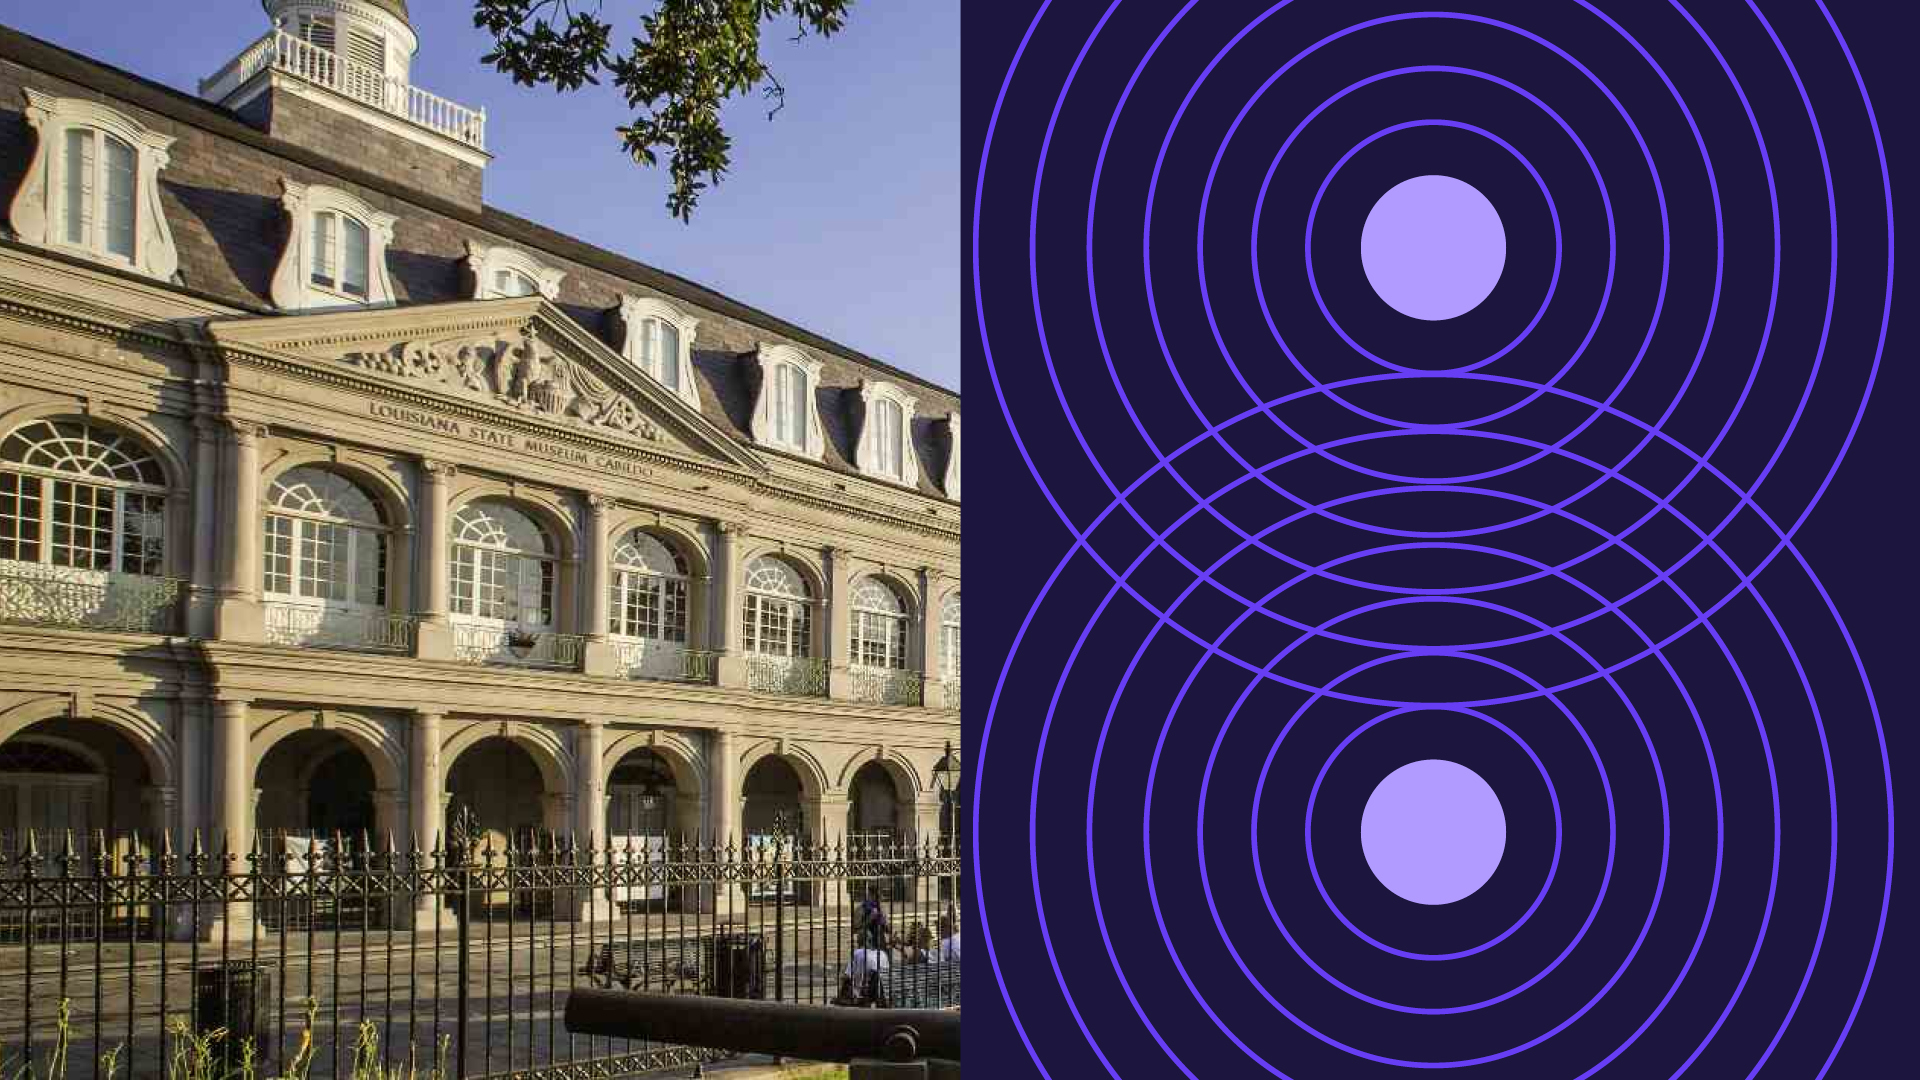
SecurityScorecard Partners with Louisiana Lieutenant Governor and Department of Culture, Recreation & Tourism to Strengthen Cyber Resilience Across Key State Agencies
SecurityScorecard deploys TITAN AI to safeguard Louisiana tourism, culture, libraries, and state assets against growing supply chain risk NEW YORK– April 30, 2026—SecurityScorecard, the global leader in threat-informed third-party risk management (TPRM), today announced a partnership with Louisiana Lieutenant Governor Billy Nungesser and the Department of Culture, Recreation & Tourism to help strengthen cyber protection
April 29, 2026
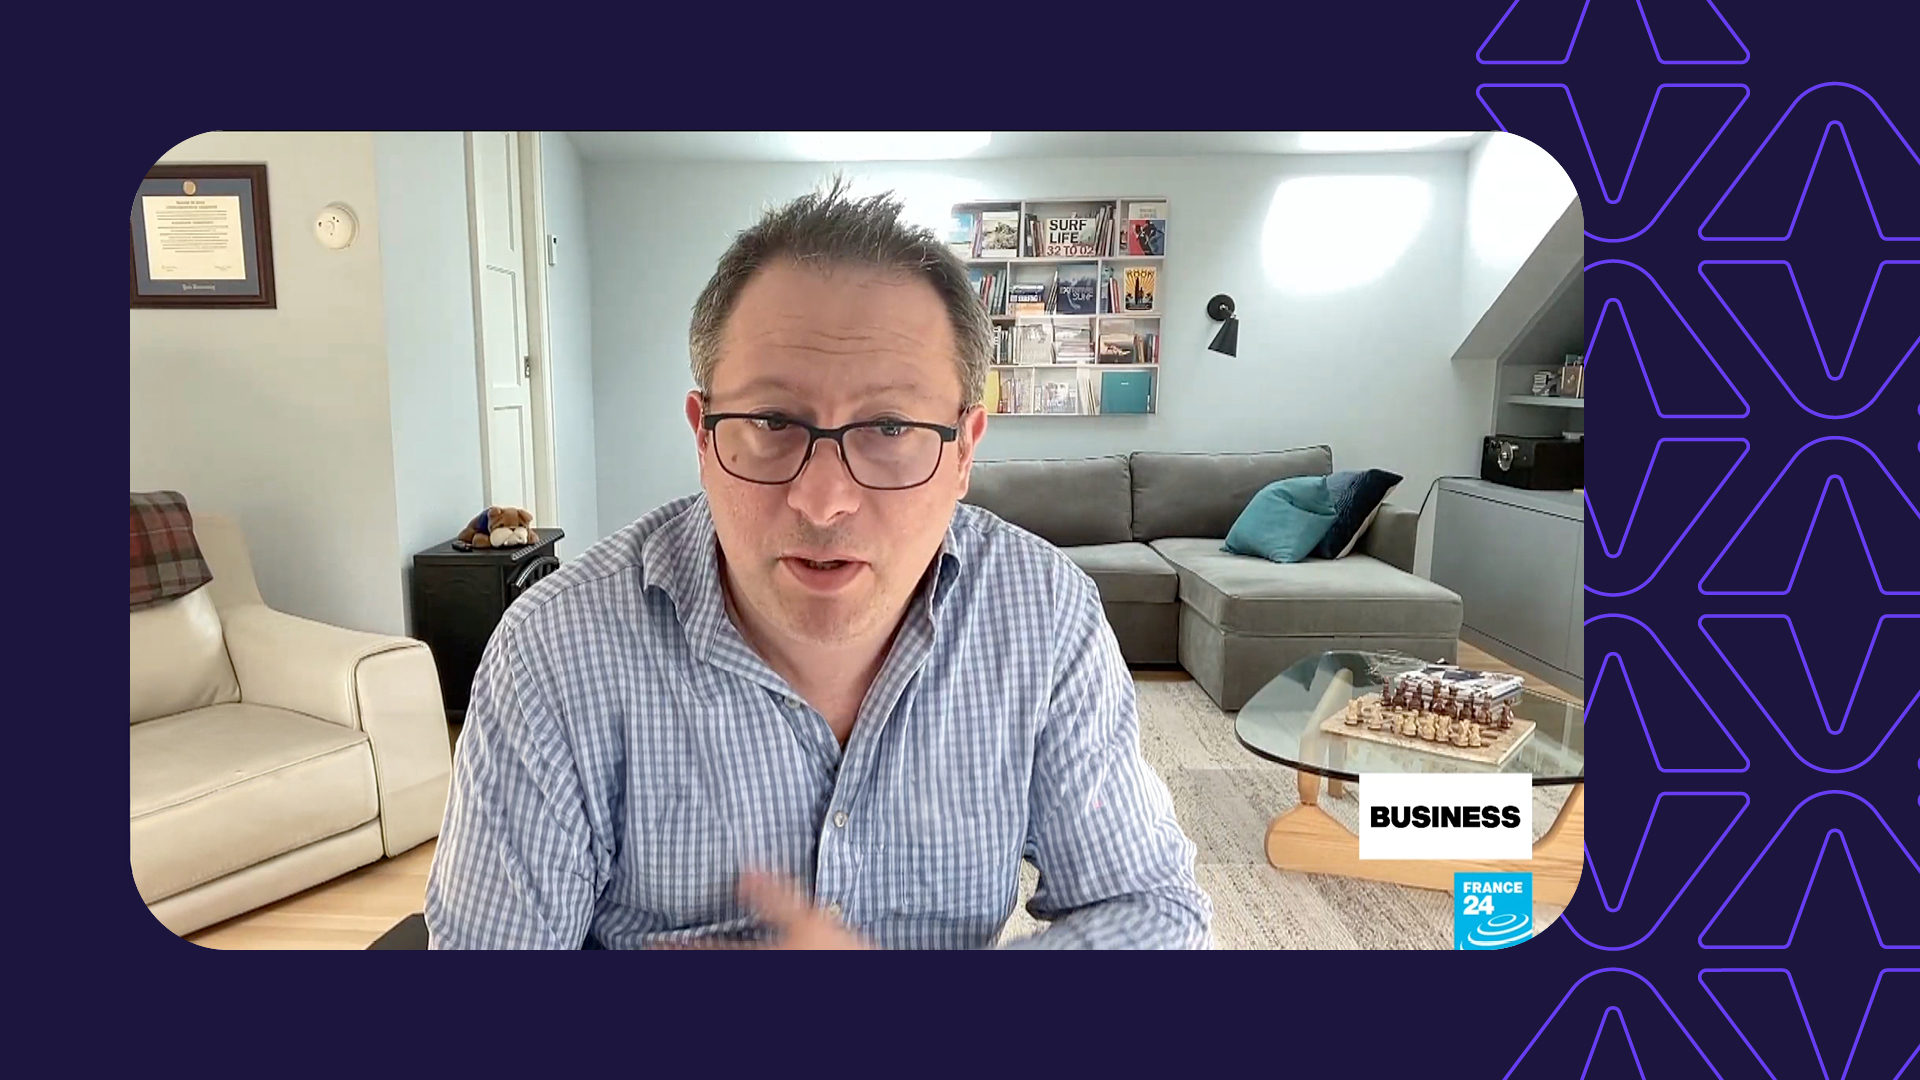
What Security Teams Need to Know Now About Anthropic’s Mythos
SecurityScorecard CEO and Co-Founder Dr. Aleksandr Yampolskiy joined Yuka Royer on France 24 to discuss Anthropic’s Mythos model, noting that AI has compressed the time to respond to cyber threats, accelerated exploitation timelines, and made automation and collaboration essential for defense. For defenders, the issue is not just more powerful AI. It is how that power
April 29, 2026
What Security Teams Need to Know Now About Anthropic’s Mythos and AI-Driven Cyber Risk
Mythos Doesn’t Change Cyber Risk. It Removes Your Time to React. Anthropic’s Mythos reinforces a reality security teams have recognized for years: cyber risk is accelerating, and the time to respond continues to shrink. The reported discovery of a 27-year-old OpenBSD vulnerability should prompt careful consideration. It does not demonstrate that AI can identify every
April 27, 2026
Vendor Tiering at Scale
Vendor tiering lets security teams categorize third-party risk by criticality. Learn how to build a tiering model that scales with your program.
April 27, 2026
Identify Shadow IT Risk with Automatic Detection
Learn how automatic detection uncovers shadow IT risk hiding in your organization. Gain real-time visibility into unauthorized tools before they become threats.
April 27, 2026
Why SMBs Need Continuous Vendor Risk Monitoring
Annual vendor audits leave SMBs vulnerable. Learn why continuous monitoring catches threats before they become breaches.
April 21, 2026
Rethinking the Questionnaire: Why Better Tech and More People Won’t Clear Your TPRM Backlog
Assessment backlogs are a common challenge for Third-Party Risk Management (TPRM) programs. Most organizations tackle the problem by increasing their capacity through hiring or improving efficiency with technology. While both are important elements of the solution, organizations also need to implement the right process for prioritizing the necessary business outcomes. This is especially true for
MAX
April 20, 2026
Attack Surface Visibility Finds Third-Party Risks First
Attack surface visibility reveals third-party risks before attackers exploit them. Learn how continuous monitoring protects your entire vendor ecosystem.
April 20, 2026
What Is Supply Chain Security?
Learn what supply chain security is, why it matters, and proven strategies to protect your organization from third-party breaches and vendor vulnerabilities.
April 13, 2026
What Is Network Security?
Learn what network security is, why it matters, and how to protect your organization from cyber threats with proven strategies and tools.
April 10, 2026
What Are Indicators of Compromise (IOCs)?
An indicator of compromise (IOC) is forensic evidence of a breach. Learn the types of IOCs, how they differ from IOAs, and how teams use them.