Resources
Blog
Resource Library
October 14, 2026
The Simple Test That Separates Real AI Transformation From AI Theater
SecurityScorecard CEO and Co-Founder Dr. Aleksandr Yampolskiy shares the before-and-after test that separates real AI transformation from AI theater.
October 14, 2026
How Security Ratings Turn Supply Chain Risk Into Resolved Risk
SecurityScorecard ratings help 3,000 organizations and over 70% of the Fortune 100 strengthen supply chains, backed by 95% attribution accuracy and data-driven insights.
October 14, 2026
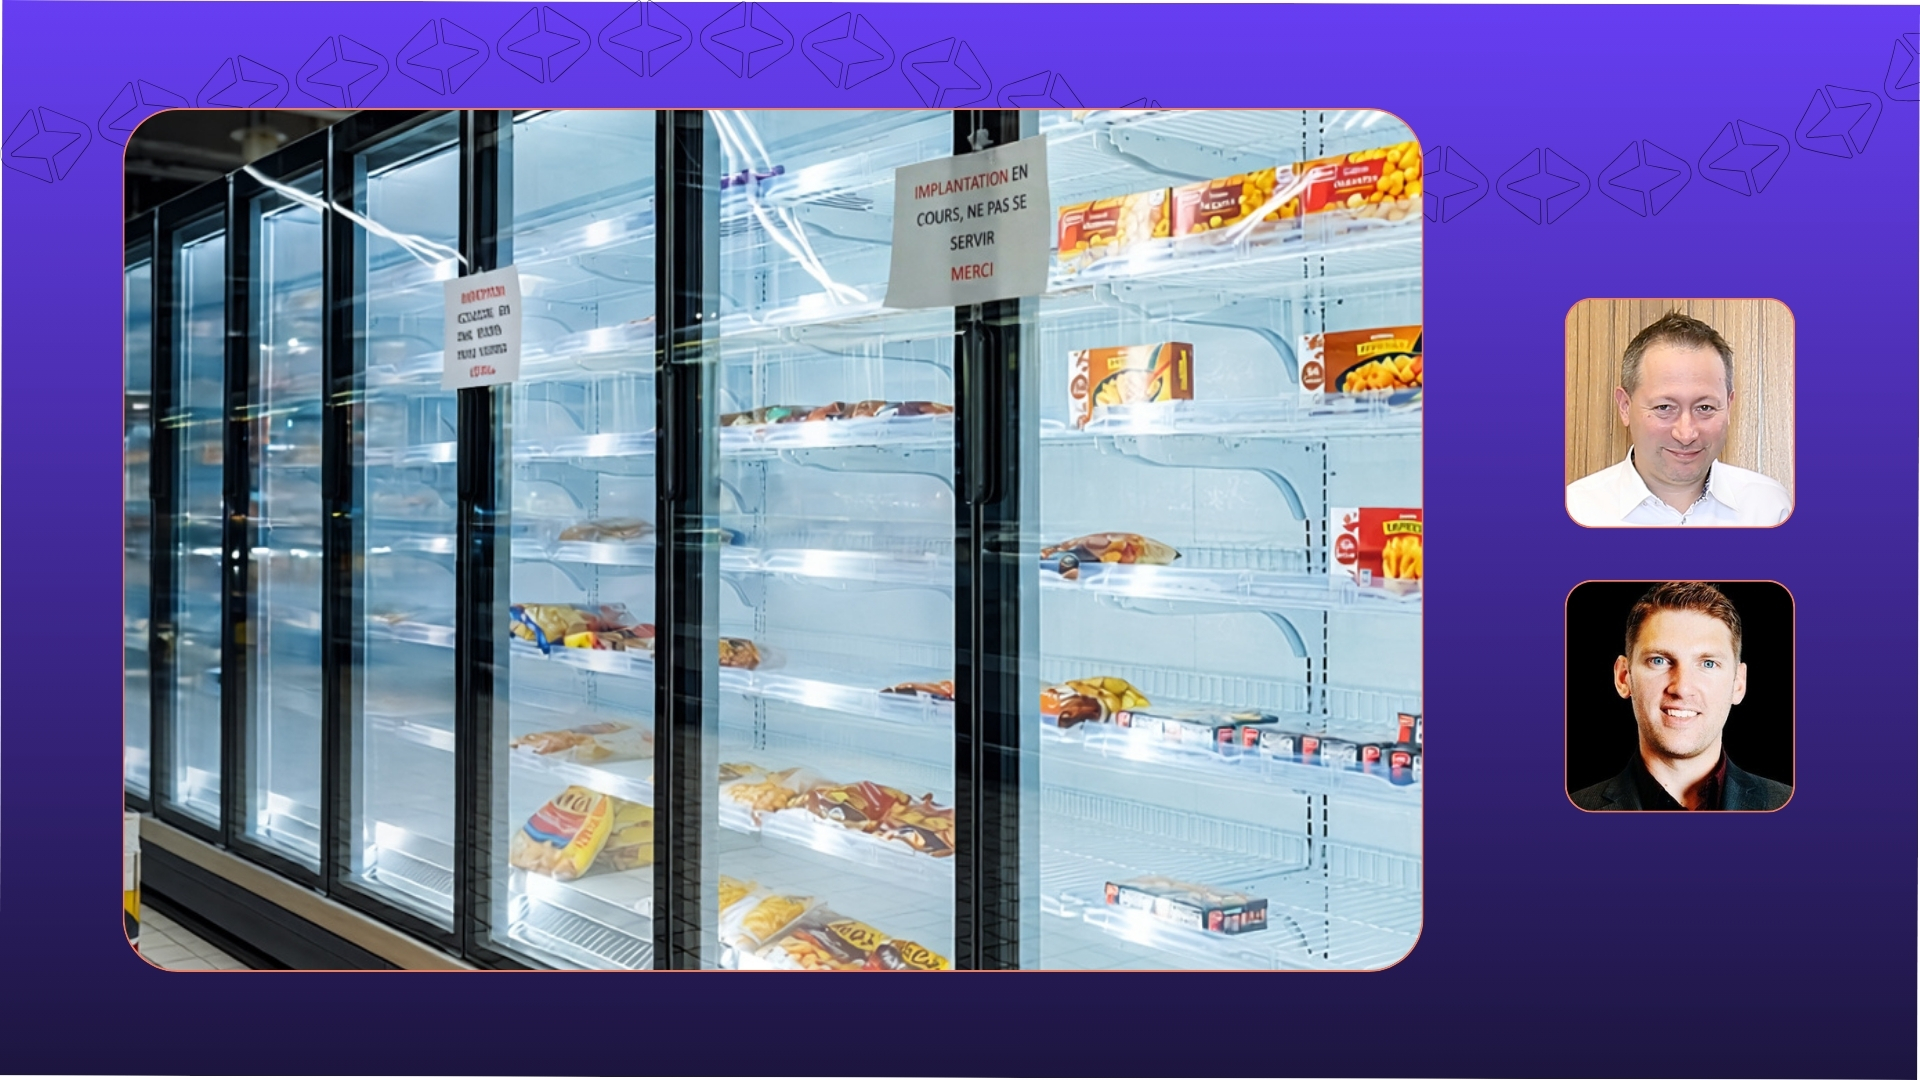
Hackers Turned Supermarket Refrigerators Into Heaters
The French attacks, the wider cold-chain footprint, and the path from internet intelligence to safe remediation.
October 13, 2026
CanOworms: How to Evict Hackers’ For-Rent Infrastructure
SecurityScorecard’s STRIKE Threat Intelligence Team uncovered CanOworms, a 633-server rental proxy network that lets attackers swap infrastructure in minutes rather than exposing their own infrastructure. Here is how the research team uncovered the network and the practical steps security teams can take to protect themselves.
STRIKE News
October 13, 2026
Scorecarder Spotlight: Amanda Smith
Amanda Smith, VP, Alliances & Channels, shares why she chose to work at SecurityScorecard, and how collaboration and innovation have helped shape her career.
Scorecarder Spotlight
October 12, 2026
Why Local Government Cybersecurity Is About to Change
Local government cybersecurity is shifting to the supply chain. See why state and local agencies need continuous vendor oversight, and what to do now.
October 12, 2026
Cybersecurity ROI in the Language Your CFO Speaks
Cybersecurity ROI, translated for finance. See what a 176% ROI, $3.9M NPV, and sub-six-month payback mean in Forrester’s study of SecurityScorecard.
October 7, 2026
Financial Services Is Banking on Third-Party Risk It Can’t See
The most interconnected financial institutions face the highest third-party breach risk. New research reveals why outsourcing-dependent supply chains create vulnerability.
October 6, 2026
Airlines Are Flying Blind on Third-Party Cyber Risk
Annual vendor questionnaires can’t stop aviation’s cyber threats. Discover how continuous monitoring protects flight operations and supply chain security.
October 5, 2026
How Regulators Use Suptech for Continuous Cyber Oversight
Suptech is changing how regulators oversee cyber risk. See how supervisory authorities in New York and Hong Kong moved to continuous monitoring.
October 5, 2026
6 Ransomware Myths Debunked: How to Prepare Your Security Team
Ransomware doesn’t spare small businesses, hospitals, or paying victims. SecurityScorecard debunks six myths with real incident data.
October 2, 2026
TITAN AI Now Runs Third-Party Risk Management End to End
Learn how TITAN AI now runs third-party risk management end to end, replacing disconnected tools with one connected workflow built on continuous intelligence and AI agents.
September 30, 2026
Data Centers Are the Backbone of AI. Their Cybersecurity Can’t Be an Afterthought.
Data center cybersecurity is a supply chain problem. Learn why continuous third-party risk monitoring matters more than ever in the AI era.
September 30, 2026
The Vanishing Window: Why We Built SecurityScorecard for What Comes Next
A response to IDC’s 2026 Spotlight on the shift from periodic to continuous, threat-informed third-party risk management.
September 28, 2026
Vendor Risk Remediation Starts with Vendors Who Respond
Vendor risk remediation stalls when vendors ignore you. See how three of our customers turned silent suppliers into active partners.
September 28, 2026
The Real Staffing Math Behind Your TPRM Team
One FTE, 600 vendors, three hours each per year. See the real staffing math behind your TPRM team and how lean teams cover every vendor.
September 25, 2026
How the EU AI Act Changes Vendor Risk Management
The European Union’s Artificial Intelligence Act has moved from preparation to enforcement. On August 2, 2026, the European Commission and national authorities gained enforcement powers under the AI Act. Transparency requirements also became applicable for certain artificial intelligence (AI) systems. For security leaders, the implications extend beyond the AI models their organizations build. AI increasingly
Third-Party Risk Management
Threat-Informed TPRM
September 15, 2026
AI Security Cannot Depend on Everyone Slowing Down
Frontier labs are calling for the industry to slow down. Our adversaries didn’t get the memo. The world’s first benchmark for AI in third-party risk management shows what we should be building instead: measurement, not just restraint.
September 4, 2026
How to Present Cyber Risk to the Board: A CISO’s Reporting Framework
CISOs now face direct board accountability for vendor risk. Here’s a practical framework for turning security data into a board-ready risk narrative — with a template to get started.
September 1, 2026
5 Reasons Your TPRM Program Needs Continuous Monitoring
Annual vendor reviews miss what changes in between. Five reasons continuous monitoring belongs in your TPRM program, plus how to run it at scale.
August 31, 2026
How to Validate Security Questionnaire Answers
Security questionnaire validation turns vendor answers into verified evidence. A step-by-step workflow for checking claims against independent data.