Resources
Blog
Resource Library
October 27, 2026
TeamPCP’s Arrests Did Not End the Threat: What STRIKE Found in the Worm and the Alliance Behind It
Two TeamPCP suspects face criminal charges, but risks to your software supply chain may remain.
STRIKE Alert
STRIKE News
October 27, 2026
PHP2Shell お客様向けアドバイザリ:CVE-2026-109618およびCVE-2026-109619 対応ガイド
SecurityScorecardのPHP2Shellアドバイザリは、CVE-2026-109618とCVE-2026-109619を対象としています。SecurityScorecardは、影響を受けた自社のPHPサイトを修正版のリリース当日にパッチ適用し、悪用の形跡は確認されませんでした。PHP2Shell脆弱性がお客様にどう影響するか、どう対応すべきかをご確認ください。
October 27, 2026
ランタイムにパッチを適用した上でフットプリントを検証する
PHP2Shellとは、CVE-2026-109618とCVE-2026-109619のことです。どちらもCVSS v4.0で9.2(Critical)と評価されています。PHPセキュリティチームによると、どちらも認証なしのリモートコード実行につながり得ます。WordPressのプラグインやアプリケーションフレームワークを更新しても、PHPランタイムの更新の代わりにはなりません。
October 27, 2026
共有依存関係がPHPの脆弱性を公共サービスのリスクに変える
PHPの重大な脆弱性2件を狙った攻撃の初期報告があり、組織や公共サービスが危険にさらされています。ミッションへの影響度と共有依存関係で優先順位を付ける方法を解説します。
October 22, 2026
PHP2Shell Customer Advisory: CVE-2026-109618 and CVE-2026-109619 Remediation Guide
SecurityScorecard’s PHP2Shell advisory covers CVE-2026-109618 and CVE-2026-109619: SecurityScorecard patched its affected PHP site on release day and found no exploitation. See how the PHP2Shell vulnerability affects you and how to respond.
STRIKE Alert
STRIKE News
October 21, 2026
Shared Dependencies Turn PHP Flaws Into a Public Service Risk
Early reported attacks on two critical PHP flaws put organizations and public services at risk. Learn how to prioritize by mission impact and shared dependencies.
STRIKE Alert
STRIKE News
October 21, 2026
Patch the runtime. Then verify the footprint.
PHP2Shell refers to CVE-2026-109618 and CVE-2026-109619, each rated 9.2 Critical under CVSS v4.0. The PHP security team says both can lead to unauthenticated remote code execution. Updating a WordPress plugin or application framework does not replace updating the PHP runtime.
STRIKE Alert
STRIKE News
October 20, 2026
フランスの約700店舗に影響、冷凍・冷蔵設備へのサイバー攻撃から学ぶ企業の5つの対策
フランスの約700店舗に影響した冷凍・冷蔵設備へのサイバー攻撃。世界で1万件超の管理画面が公開状態にあることが判明。企業が今すぐ取り組むべき5つの対策を解説します。
October 14, 2026
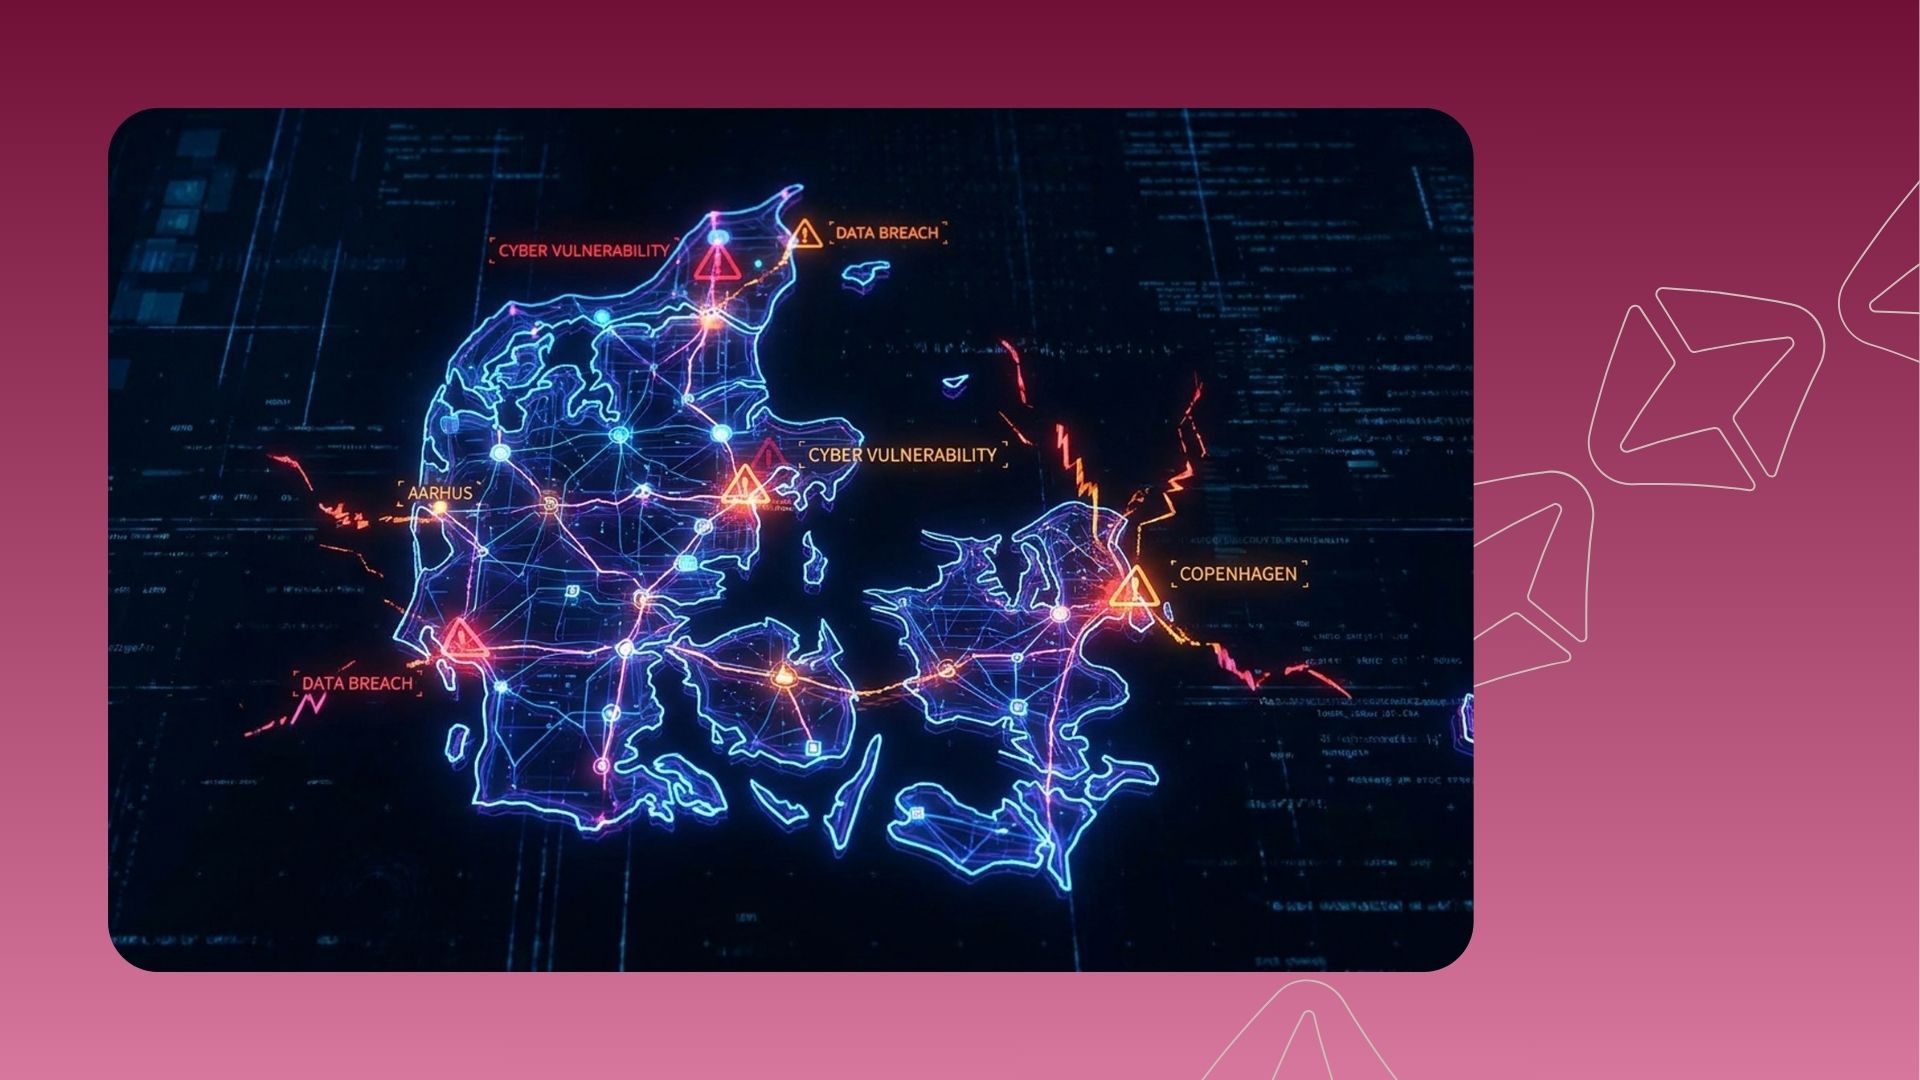
One Vendor, Millions Exposed: Lessons from Denmark’s CPR Breach
The Denmark Central Population Register (CPR) breach exposed 8.8 million records through approved vendor access. See how continuous third-party risk monitoring and risk tiering reduce third-party exposure.
October 14, 2026
The Simple Test That Separates Real AI Transformation From AI Theater
SecurityScorecard CEO and Co-Founder Dr. Aleksandr Yampolskiy shares the before-and-after test that separates real AI transformation from AI theater.
October 14, 2026
How Security Ratings Turn Supply Chain Risk Into Resolved Risk
SecurityScorecard ratings help 3,000 organizations and over 70% of the Fortune 100 strengthen supply chains, backed by 95% attribution accuracy and data-driven insights.
October 14, 2026
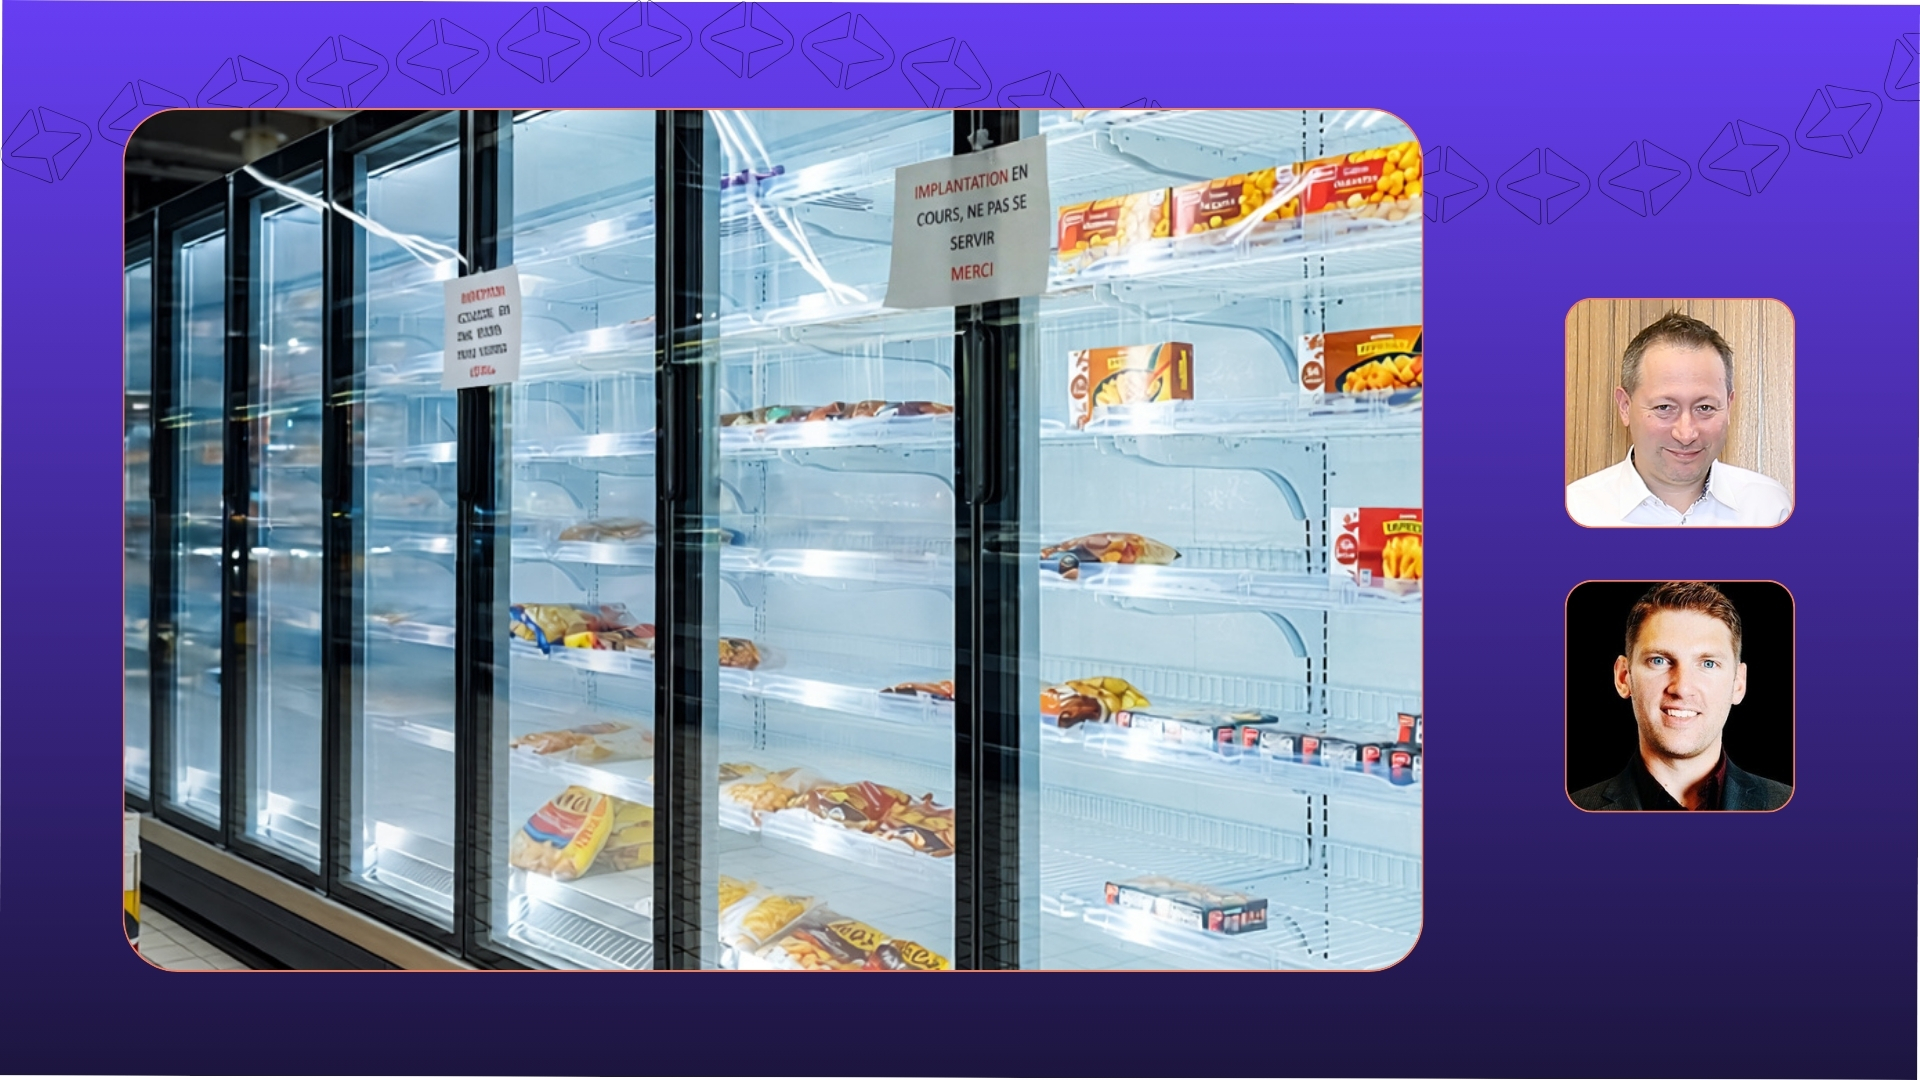
Hackers Turned Supermarket Refrigerators Into Heaters
The French attacks, the wider cold-chain footprint, and the path from internet intelligence to safe remediation.
October 13, 2026
CanOworms: How to Evict Hackers’ For-Rent Infrastructure
SecurityScorecard’s STRIKE Threat Intelligence Team uncovered CanOworms, a 633-server rental proxy network that lets attackers swap infrastructure in minutes rather than exposing their own infrastructure. Here is how the research team uncovered the network and the practical steps security teams can take to protect themselves.
STRIKE News
October 13, 2026
Scorecarder Spotlight: Amanda Smith
Amanda Smith, VP, Alliances & Channels, shares why she chose to work at SecurityScorecard, and how collaboration and innovation have helped shape her career.
Scorecarder Spotlight
October 7, 2026
Financial Services Is Banking on Third-Party Risk It Can’t See
The most interconnected financial institutions face the highest third-party breach risk. New research reveals why outsourcing-dependent supply chains create vulnerability.
October 6, 2026
Airlines Are Flying Blind on Third-Party Cyber Risk
Annual vendor questionnaires can’t stop aviation’s cyber threats. Discover how continuous monitoring protects flight operations and supply chain security.
October 5, 2026
6 Ransomware Myths Debunked: How to Prepare Your Security Team
Ransomware doesn’t spare small businesses, hospitals, or paying victims. SecurityScorecard debunks six myths with real incident data.
October 2, 2026
TITAN AI Now Runs Third-Party Risk Management End to End
Learn how TITAN AI now runs third-party risk management end to end, replacing disconnected tools with one connected workflow built on continuous intelligence and AI agents.
September 30, 2026
Data Centers Are the Backbone of AI. Their Cybersecurity Can’t Be an Afterthought.
Data center cybersecurity is a supply chain problem. Learn why continuous third-party risk monitoring matters more than ever in the AI era.
September 30, 2026
The Vanishing Window: Why We Built SecurityScorecard for What Comes Next
A response to IDC’s 2026 Spotlight on the shift from periodic to continuous, threat-informed third-party risk management.
September 25, 2026
How the EU AI Act Changes Vendor Risk Management
The European Union’s Artificial Intelligence Act has moved from preparation to enforcement. On August 2, 2026, the European Commission and national authorities gained enforcement powers under the AI Act. Transparency requirements also became applicable for certain artificial intelligence (AI) systems. For security leaders, the implications extend beyond the AI models their organizations build. AI increasingly
Third-Party Risk Management
Threat-Informed TPRM