
Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library
Video
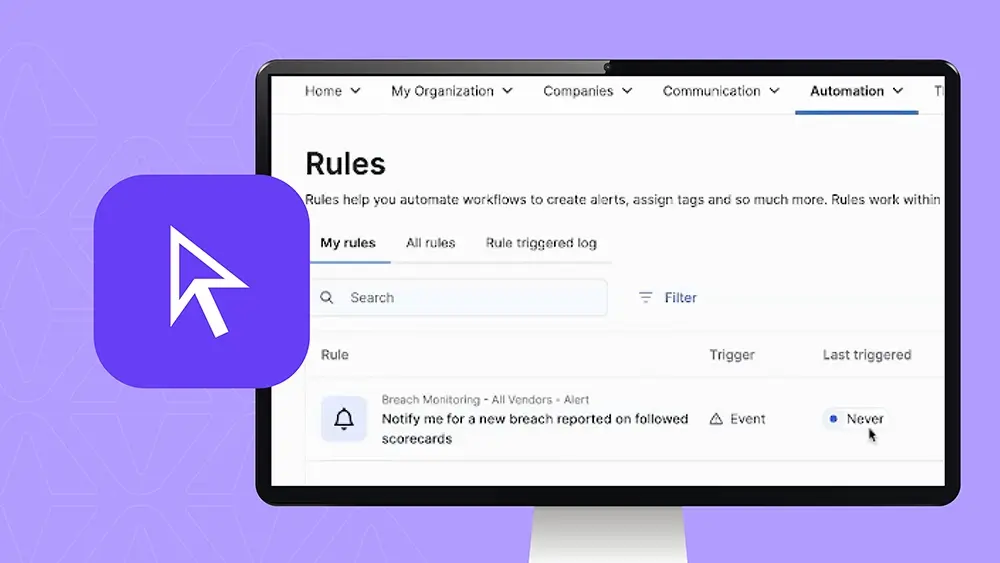
TITAN Watch – Rule Builder Agent
Learn how SecurityScorecard’s Rule Builder agent automates vendor risk alerting, from breach monitoring to score threshold triggers. This step-by-step walkthrough shows how to set up a fully configured alert in minutes, without manual rule-building or risk of duplication.
Demo Tuesdays
Blog
What Are DORA Compliance Requirements
Learn what DORA compliance requirements mean for financial entities, from ICT risk management and incident reporting to third-party oversight.
Blog
Scorecarder Spotlight: Emmy Chau
Our “Scorecarder Learning & Development Spotlight” series showcases our talented, driven employees, the incredible work they do, and their quest to continue their development as lifelong learners. Name: Emmy Chau Role: Senior Manager, FP&A “One of the things I appreciate most about SecurityScorecard is the opportunity to keep learning. Whether it’s partnering with teams across
Scorecarder Spotlight
Research
Catch Me If You Can: Inside the Anonymization-for-Hire Network
In this briefing, Wade Lance VP, Product Marketing & Sales Enablement walks through STRIKE’s newest report Catch Me If You Can.
Wade takes viewers inside the full commercial stack behind CanOworms — tenants, relay fleet, resellers, and landlord ASNs — and explains why treating a threat-feed-flagged C2 as a single actor’s infrastructure can lead defenders to the wrong conclusion entirely.
This isn’t a read-through of the report. It’s Wade’s field-tested take on what the findings mean for how security teams should actually hunt this kind of infrastructure.
Download the briefing now.
STRIKE Alert
STRIKE News
STRIKE Team
Blog
What Is Internet-Wide Scanning, and How Attackers Use It
Internet-wide scanning lets attackers find exposed hosts fast. See how it works and how to spot your exposure before they do.
Blog
How SOC Automation Improves Threat Response
SOC automation helps security teams respond faster, cut false positives, and scale operations. Learn the top use cases, benefits, and challenges.
Blog
Inside CanOworms: The 633-Server Proxy Network Hiding Criminal and State-Linked Activity
SecurityScorecard’s STRIKE team uncovered a 633-server anonymization network used by commodity malware operators and suspected state-linked actors, revealing how attackers rent shared infrastructure to evade traditional defenses.
STRIKE Alert
STRIKE News
STRIKE Team
Research
Catch Me If You Can: New Research Reveals CanOworms, a Proxy Network for Hire
Blocklists, geolocation, and ASN reputation all share one assumption: that an IP tells you who’s behind it. CanOworms is built to break that assumption. STRIKE identified 633 confirmed member servers operating as a shared Squid/SOCKS/OpenVPN/IPsec relay fleet — not a command-and-control panel, but the disposable front in front of one. Dozens of tenants, from Remcos and Quasar operators to suspected APT41 and APT43/APT37 infrastructure, have used these same relays. The operator is unattributed by design. Many tenants, one set of relays.
What you’ll learn:
How the mesh was found. A shared self-signed TLS certificate (O=kickass), corroborated by JARM and JA4X fingerprints, exposed 633 confirmed nodes out of 748 candidate IPs across a dozen dense /24 blocks, six-plus hosting providers, and more than a dozen countries.
How it’s run. Five Czech Republic control-plane hosts manage the fleet in a centralized “star” topology, with one node alone touching roughly 256 others and a fleet-wide ~35-second heartbeat back to a single collector — a pressure point defenders can watch.
Who’s renting it, and who isn’t. A reseller called “PrivacyFirst” (MAXKO d.o.o., AS214366) surfaces in the paper trail, but only a fraction of its address space actually carries the mesh certificate — a case study in why reseller identity isn’t operator identity isn’t tenant identity.
Where the attack traffic lands. Suspected credential-spray traffic exits the fleet toward MikroTik routers, TR-069 CPE, and Hikvision cameras — concentrated in South Africa, India, the U.S., Brazil, and Bangladesh. Commodity-crime geography, not espionage-target geography.
Why IP-based defense fails here, and what to fingerprint instead. The report lays out why durable detection means tracking how the infrastructure was built (certificate thumbprints, JARM, JA4X, service-stack signature) rather than chasing IPs that get burned and replaced faster than blocklists can keep up.
Full IOCs and MITRE ATT&CK mapping. Appendix A publishes the complete fingerprint set — ready to drop into detection tooling — mapped to ATT&CK Resource Development and C2 techniques (T1583.003, T1090.002, T1571).
Download “Catch Me If You Can” for the complete CanOworms research, including the fingerprint methodology, control-plane analysis, and the full IOC appendix.
Blog
How to Make the Most of Your SecurityScorecard Free Trial
Most free trial users only check their score once. Here’s how to use every feature available — from self-monitoring and vendor checks to ASI searches — to get real value from day one.
Video
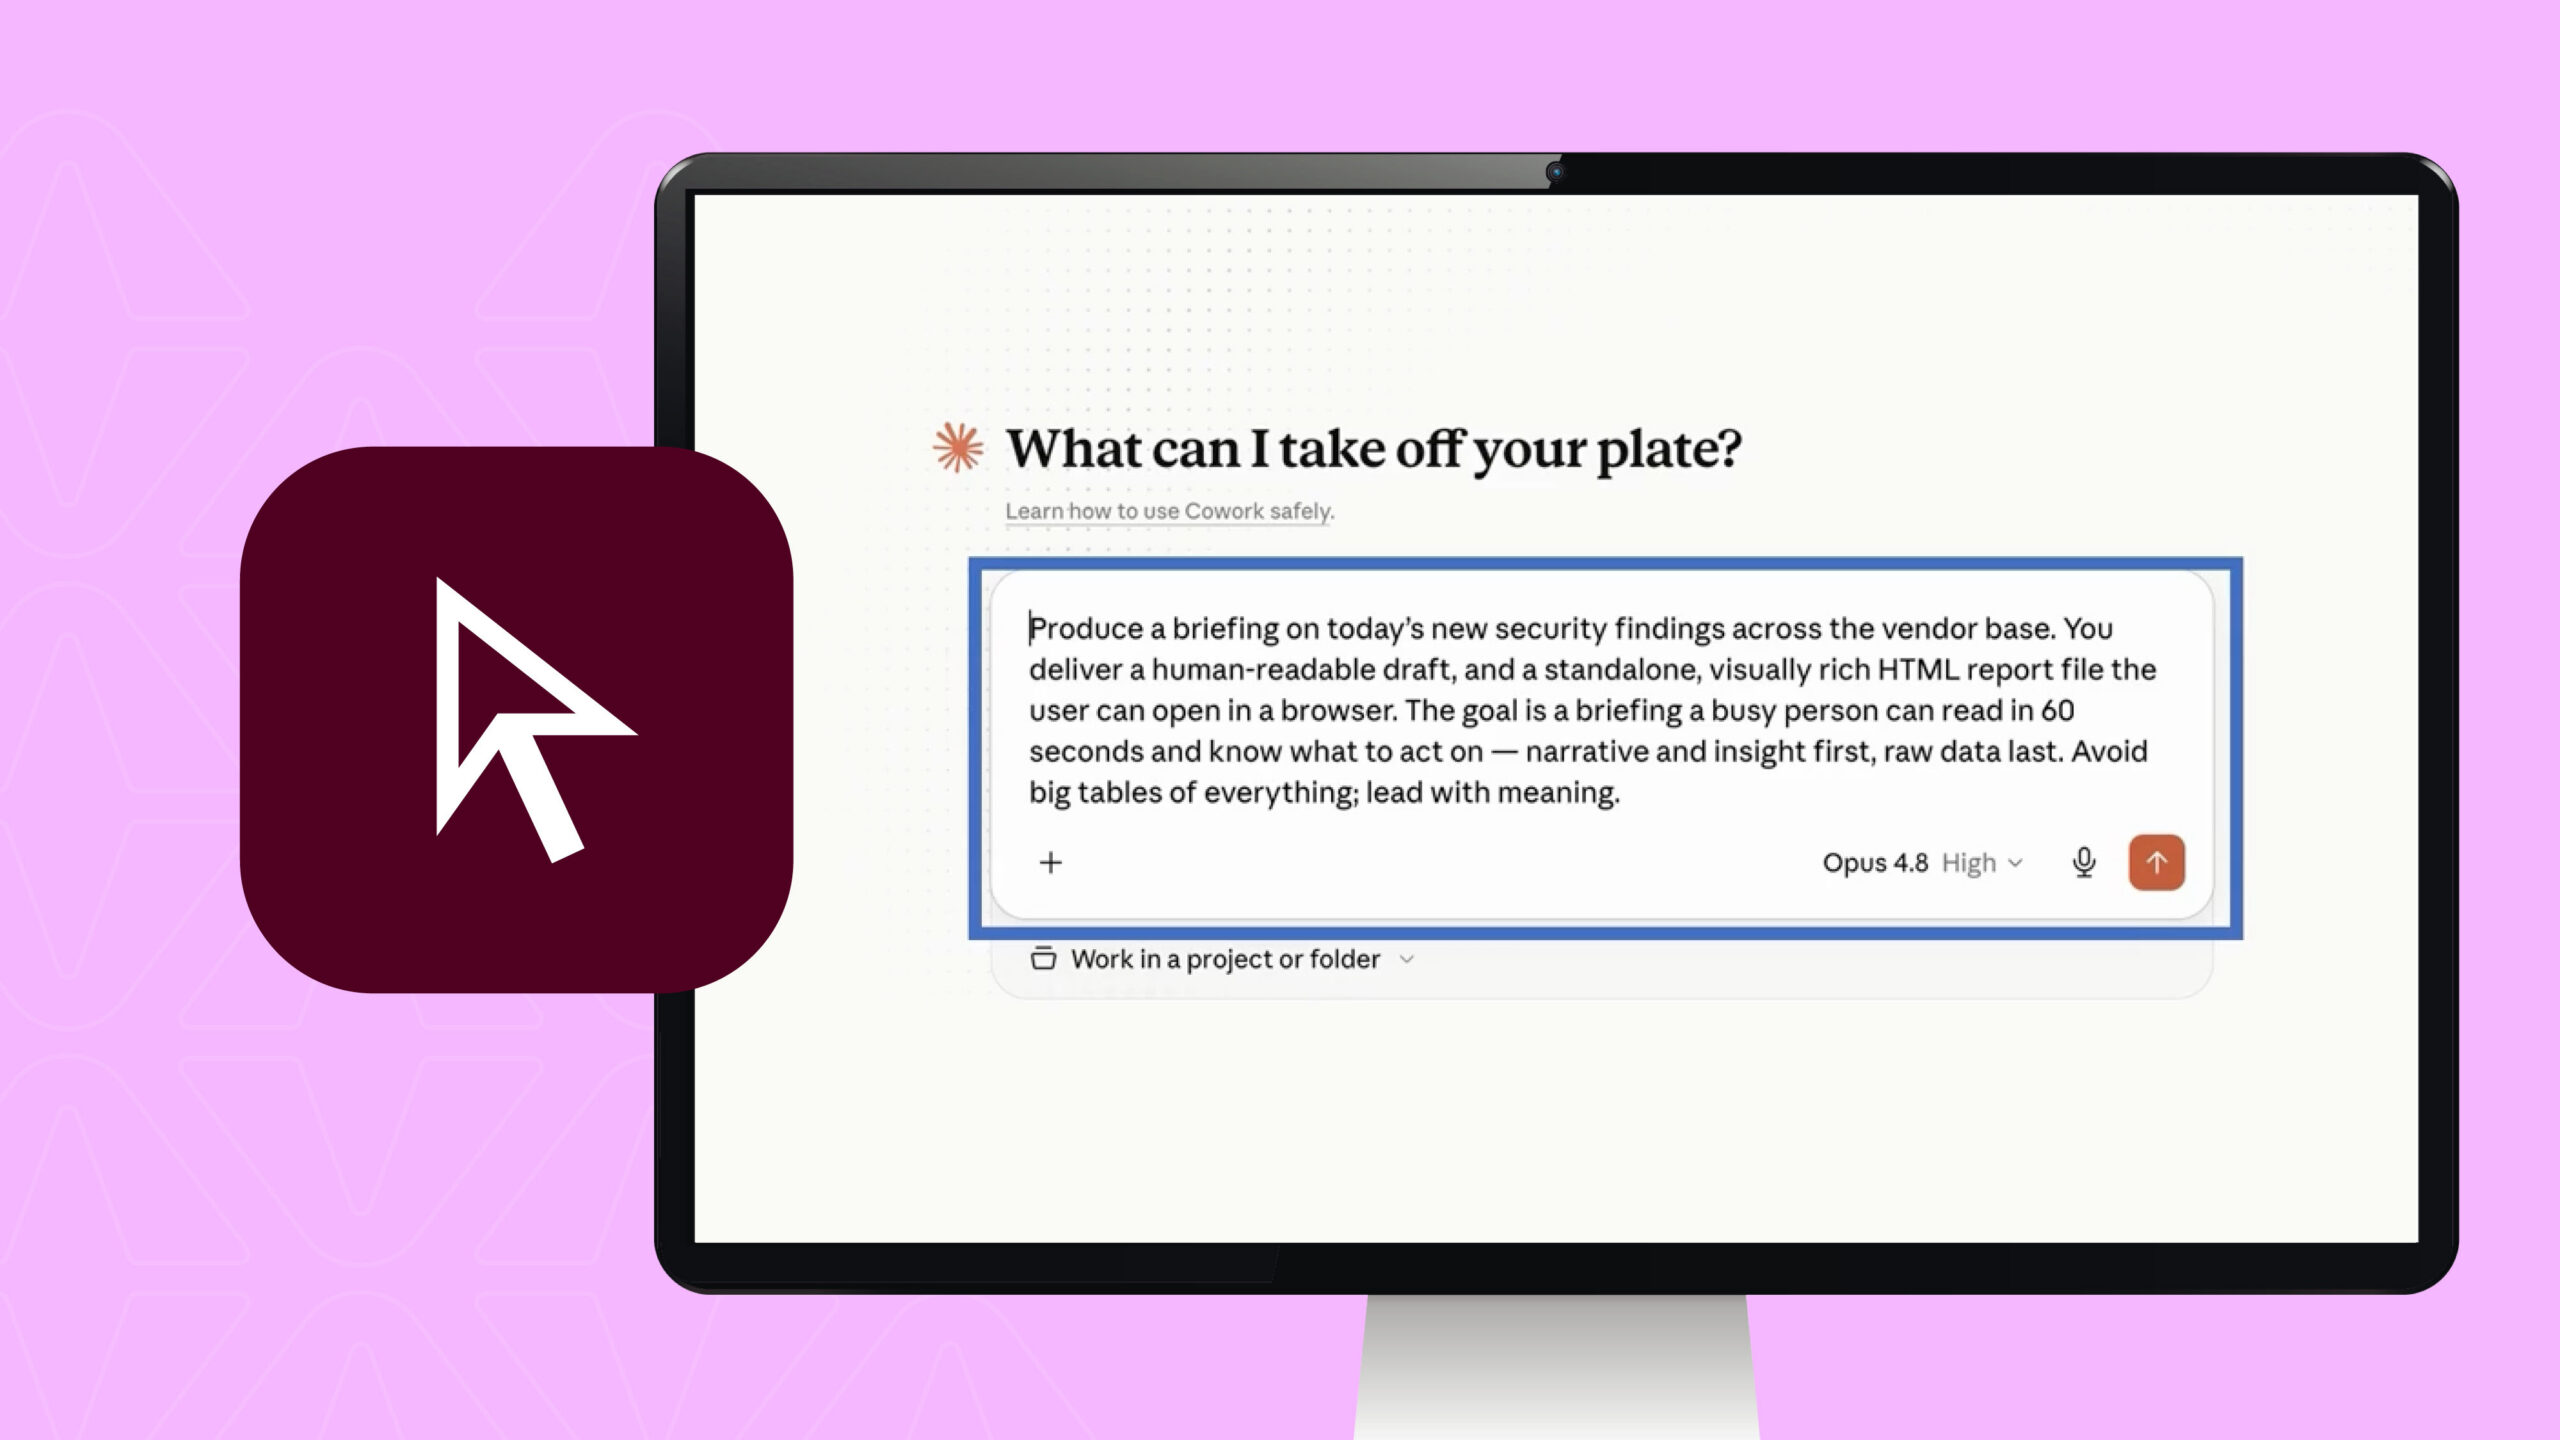
Use the TITAN AI MCP connector in Claude
Our customers can now build powerful TPRM workflows directly in Claude using SecurityScorecard data and the Titan AI MCP connector. An MCP connector for SSC has been one of our most requested asks and it’s a huge milestone for the platform.
Demo Tuesdays
Blog
How to Manage AI Vendor Risk
Manage AI vendor risk with a framework for vetting AI capabilities, auditing data flows, and bringing AI tools into continuous monitoring.
Blog
Domestic Sourcing Alone Won’t Secure America’s Defense Supply Chains
This month, the Administration signed an executive order that will force primes and subcontractors in the Defense Industrial Base to answer a question they have spent years avoiding: where does this actually come from? That’s the right question. It’s just not the whole question.
Video
MAX: Behind the scenes – How Max Delivers Accountability
See how requests, updates, and escalations flow through a managed task backlog, where TITAN AI agents analyze data and propose actions for human review to ensure total accountability.
Demo Tuesdays
Video
MAX: How MAX detects and responds to zero-days
See how MAX monitors vendor ecosystems for emerging threats and zero-day vulnerabilities, identifying exposed vendors and driving remediation to closure within tight SLAs.
Demo Tuesdays
Video
MAX: What a Mature TPRM Program Looks Like
See how MAX streamlines vendor assessments, cuts cycle times, and achieves a 70% engagement rate through managed vendor outreach—empowering our customers to focus on decision-making instead of chasing follow-ups.
Demo Tuesdays
Blog
How to Identify a Critical Vendor
Identifying a critical vendor is a CISO’s discipline. Learn how to build a defensible list, run a bankruptcy stress test, and monitor continuously.
Video
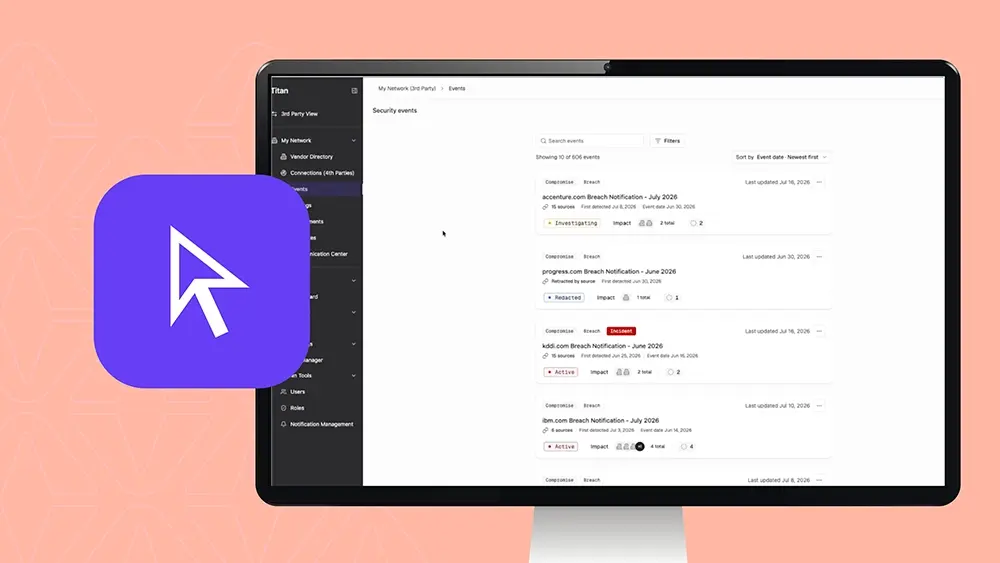
TITAN SECURE: Identifying a Cybersecurity Event
In this installment of SecurityScorecard’s Demo Tuesday series, see how TITAN Secure’s built-in investigation workspaces, response tracking, and clear vendor-impact tables help teams move from reactive noise sifting to proactive, evidence-backed decision-making.
Demo Tuesdays
Blog
How to Secure Your SaaS Supply Chain
Most SaaS supply chain attacks start at a forgotten vendor. Learn how to map, monitor, and secure every third-party app touching your data.
Webinars
Preparing for the Post-Mythos Era: When AI Finds Vulnerabilities Faster Than Humans
Learn more in this resource.
Mythos
Supply Chain Cyber Risk
Case Studies
CEDIA
Cómo CEDIA transformó la ciberresiliencia del ecosistema académico ecuatoriano con SecurityScorecard
Case Studies
MRS Brazil
Depoimento da MRS sobre como a SecurityScorecard trouxe visibilidade independente à postura de segurança externa da empresa, elevando o score a 100% e tornando a gestão de risco cibernético um indicador estratégico acompanhado por executivos e áreas técnicas.