
Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library
Webinars
Beyond the Backlog: Why Tech and Talent Aren’t Fixing Your TPRM Questionnaires
Learn more in this resource.
Blog
What Secure by Design Means for Vendor Vetting
Secure by design means building security in from the start. Learn what it means for vendor vetting and how to assess whether your vendors actually follow it.
Video
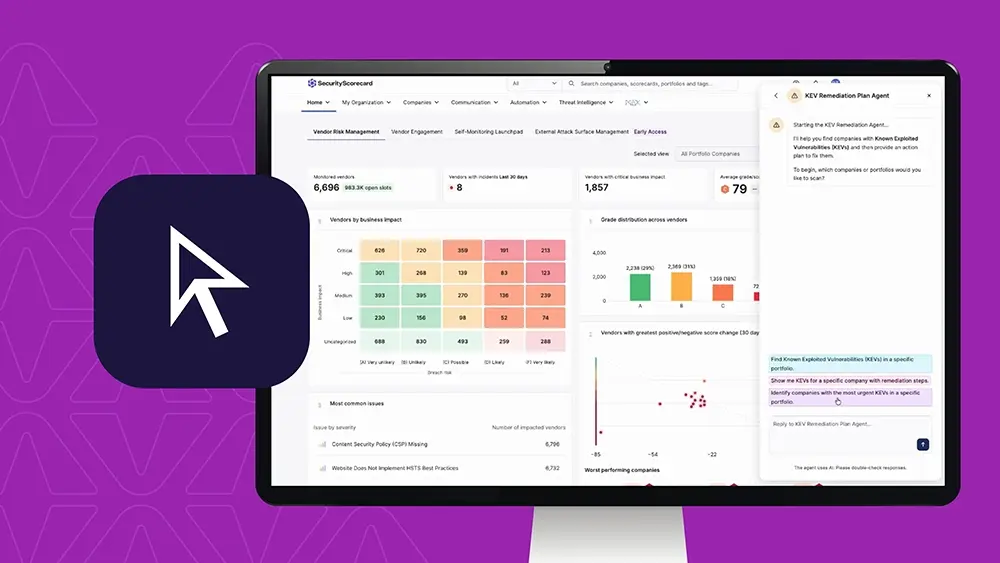
Mythos and CVE/KEV Management
Check out this quick demo video to see how our new AI agents — like the KEV Remediation Plan Agent — help teams identify exposed vendors, prioritize the vulnerabilities that matter most, and generate remediation guidance in minutes.
Demo Tuesdays
Blog
Vendor Offboarding: The Step TPRM Teams Forget
Vendor offboarding is the stage most teams skip. See why lingering vendor access turns into breach risk, and how to close the gap.
Blog
Living Off the Land Attacks Explained
Living off the land attacks use legitimate system tools to evade detection. Learn how LOTL techniques work, who uses them, and how to reduce your exposure.
Blog
How Ransomware as a Service Has Changed
Ransomware-as-a-service has transformed who can launch a ransomware attack and how. Learn how the RaaS model works and how to defend your supply chain.
Blog
How Cloud Misconfiguration Exposes Vendor Networks
Cloud misconfiguration is one of the most common causes of data breaches. Learn how vendor cloud misconfigurations create risk and how to reduce your exposure.
Blog
What Agentic AI Security Risks Mean for CISOs
Agentic AI introduces security risks traditional controls weren’t built for. Learn what CISOs need to know about securing autonomous AI systems and supply chains.
Blog
How Deepfake Phishing Powers Business Email Compromise
Deepfake phishing uses AI-generated voice and video to impersonate trusted contacts. Learn how these attacks work and how to defend your organization.
Blog
Software Bill of Materials and Supply Chain Risk
A software bill of materials documents every component in your software supply chain. Learn what SBOMs are, why they matter, and how to build a program that holds up.
White Papers
TPRM: De la gestion statique au pilotage en temps réel
Moderniser la gestion des risques tiers grâce à l’IA et à la Threat Intelligence
Pendant des décennies, la gestion des risques tiers (TPRM) s’est résumée à un exercice statique, réalisé à un instant précis, par fichiers et questionnaires interminables. Mais aujourd’hui, cette approche constitue un risque opérationnel majeur. À mesure que se multiplient les dépendances, une seule vulnérabilité enfouie dans une bibliothèque logicielle peut déclencher une panne mondiale en quelques secondes.
Alors que 90 % des responsables cyber se disent convaincus de leur résilience, à peine 22 % des programmes TPRM internes évaluent plus de la moitié de leur écosystème de fournisseurs. Pour combler cet écart, les organisations doivent abandonner la conformité réactive au profit d’une intelligence continue, où les données en temps réel et l’analyse prédictive remplacent l’audit annuel obsolète.
Téléchargez ce guide pour découvrir:
Les trois piliers du TPRM moderne : intégrer la télémétrie en temps réel, les signaux issus des adversaires et une orchestration pilotée par l’IA pour dépasser la conformité purement statique.
Réduire drastiquement les délais d’intégration : réduire le temps d’intégration d’un nouveau fournisseur de 42 jours à seulement 42 heures, grâce à l’automatisation et le pré-remplissage intelligent, pilotés par l’IA.
La Threat Intelligence comme multiplicateur de force : Associer une vision externe (Outside-In) à une vision interne pour identifier en temps réel les expositions zero-day et les risques de concentration.
Le virage agentique : évoluer vers des agents IA capables de surveiller les risques de manière autonome et de déclencher des demandes de remédiation sans intervention humaine.
Blog
Building Trust In Data: How We Added Data Quality Checks To Our Scoring Data Pipeline
Data quality is foundational to customer confidence. At SecurityScorecard, our Scoring platform processes data for thousands of companies daily. That scale requires more than strong engineering discipline. It requires clear validation patterns, consistent checks, and observable results across every critical stage of the pipeline. This post shares how our data engineering team uses Great Expectations,
Report
SecurityScorecard’s New Driftnet Engine Reveals America’s Small-Town Surveillance Blind Spot
SecurityScorecard researchers used Driftnet’s internet-scale discovery capabilities to analyze the network footprint of a small U.S. municipal utility provider that also operates as the town’s internet service provider (ISP). The investigation identified widespread exposure across internet-facing systems, including vulnerable surveillance equipment, exposed Industrial Control Systems (ICS), weak encryption configurations, and End-of-Life (EoL) Windows devices.
The utility provider operates its own Autonomous System (AS), meaning internet connectivity and critical infrastructure services exist within the same broader operational environment. This convergence creates a concentrated point of failure where disruption to one service can affect others across the community.
Over a six-month period, Driftnet identified 1,498 services across 692 IP addresses. Of those, 446 IPs (64%) exhibited at least one technical issue that increased exposure risk. SecurityScorecard’s Driftnet engine identifies 150% more internet-facing services than previous scanning methodologies, uncovering exposures traditional approaches miss. Findings included:
30 instances of Dahua and Hikvision surveillance equipment inside the entire footprint of the utilities AS. Banned internet protocol (IP) cameras could enable Man-in-the-Middle (MitM) attacks, Distributed Denial of Service (DDoS) attacks, malware-based campaigns, and more.
Exposed ICS, SCADA, and OT-related services directly reachable from the internet. At least three /24 clusters hosting ICS or IOT services and consumer devices on the same broadcast domain.
Weak or misconfigured encryption across 382 IP addresses, in addition to cleartext FTP and HTTP and unrecognized Certificate Authorities.
EoL Windows hosts reachable via Server Message Block (SMB) and NetBIOS. A relic from the past, rarely ever makes an appearance outside of OT environments.
25 Known Exploited Vulnerabilities (KEVs) identified across internet-facing services.
Convergence of a utility and ISP creates a single point of failure. Power delivery and internet reside on the same AS. Incidents on one impacts the other.
The research also identified multiple network segments where consumer-grade devices, surveillance systems, and ICS-related technologies operated within the same local network environment. This lack of segmentation increases the likelihood that compromise of a lower-security system could enable lateral movement toward operational infrastructure.
To understand the full scope of the findings, download the full report today to see how Driftnet delivers the visibility organizations need to move from reactive security to continuous, threat-informed defense.
STRIKE Alert
STRIKE News
STRIKE Team
Press
SecurityScorecard Acquires Driftnet to Power Real-Time, Threat-Informed Third-Party Risk Management
NEW YORK– May 14, 2026 – SecurityScorecard, the global leader in threat-informed third-party risk management (TPRM), today announced it has completed the acquisition of Driftnet, a pioneer in global internet scanning and next-generation threat intelligence. This acquisition will bring Driftnet’s high-fidelity internet discovery engine into SecurityScorecard’s TITAN AI platform, giving TPRM, Security Operations, and threat
Blog
Why Password Spraying Attacks Target Your Vendors
Password spraying attacks use one password across many accounts to avoid lockouts. Learn how attackers target your vendors and how to stop them.
Blog
How to Meet Cyber Insurance Requirements
Learn what cyber insurance requirements insurers expect, how to close third-party risk gaps, and how continuous monitoring strengthens your coverage.
Blog
Supply Chain Security Needs Real-Time Visibility
Learn why supply chain security demands real-time visibility and explore 7 best practices to protect your organization from third-party cyber threats.
Blog
Building a Vendor Compliance Dashboard for Auditors
Build a compliance dashboard auditors actually trust. Learn how real-time vendor monitoring beats outdated quarterly assessments.
Ebook
A Roadmap to Modern TPRM
Understanding the 4 Stages, the Gaps, and TPRM Priorities for Various Stakeholders Traditional Third-Party Risk Management (TPRM) programs, relying on static data and annual assessments, are failing to secure supply chains, exposing organizations to the 35%+ of breaches originating from third parties. This eBook provides a roadmap to understanding the disconnect between modern threats and
Blog
The Four Questionnaires Your TPRM Team Is Managing (And Struggling to Keep Up With)
The questionnaire is the workhorse of third-party risk management. But not all questionnaires are the same and treating them like they are is one of the reasons TPRM programs fall behind. Here’s a clear-eyed look at the four types your team is juggling. 1. Initial / Intake Questionnaires Also called: Inherent Risk Questionnaire (IRQ), Vendor
Blog
Passive DNS Explained: Vendor and Threat Infrastructure
Passive DNS Explained: Vendor and Threat Infrastructure