Threat-Informed TPRM
Proactively Manage and Reduce Vendor Cyber Risk
Transform how your team identifies, prioritizes, and acts on real-world cyber threats across your entire vendor ecosystem with a unified, continuous workflow.
The CVE Fire Drill
A headline drops. An analyst runs a manual search, then blasts attestation requests to hundreds of vendors and tracks every response by hand. This CVE Fire Drill is the default mode for most Third-Party Risk Management (TPRM) programs. TITAN Secure closes the gap: you define the standard, and it tells you who falls short first.
Expect More From Your TPRM

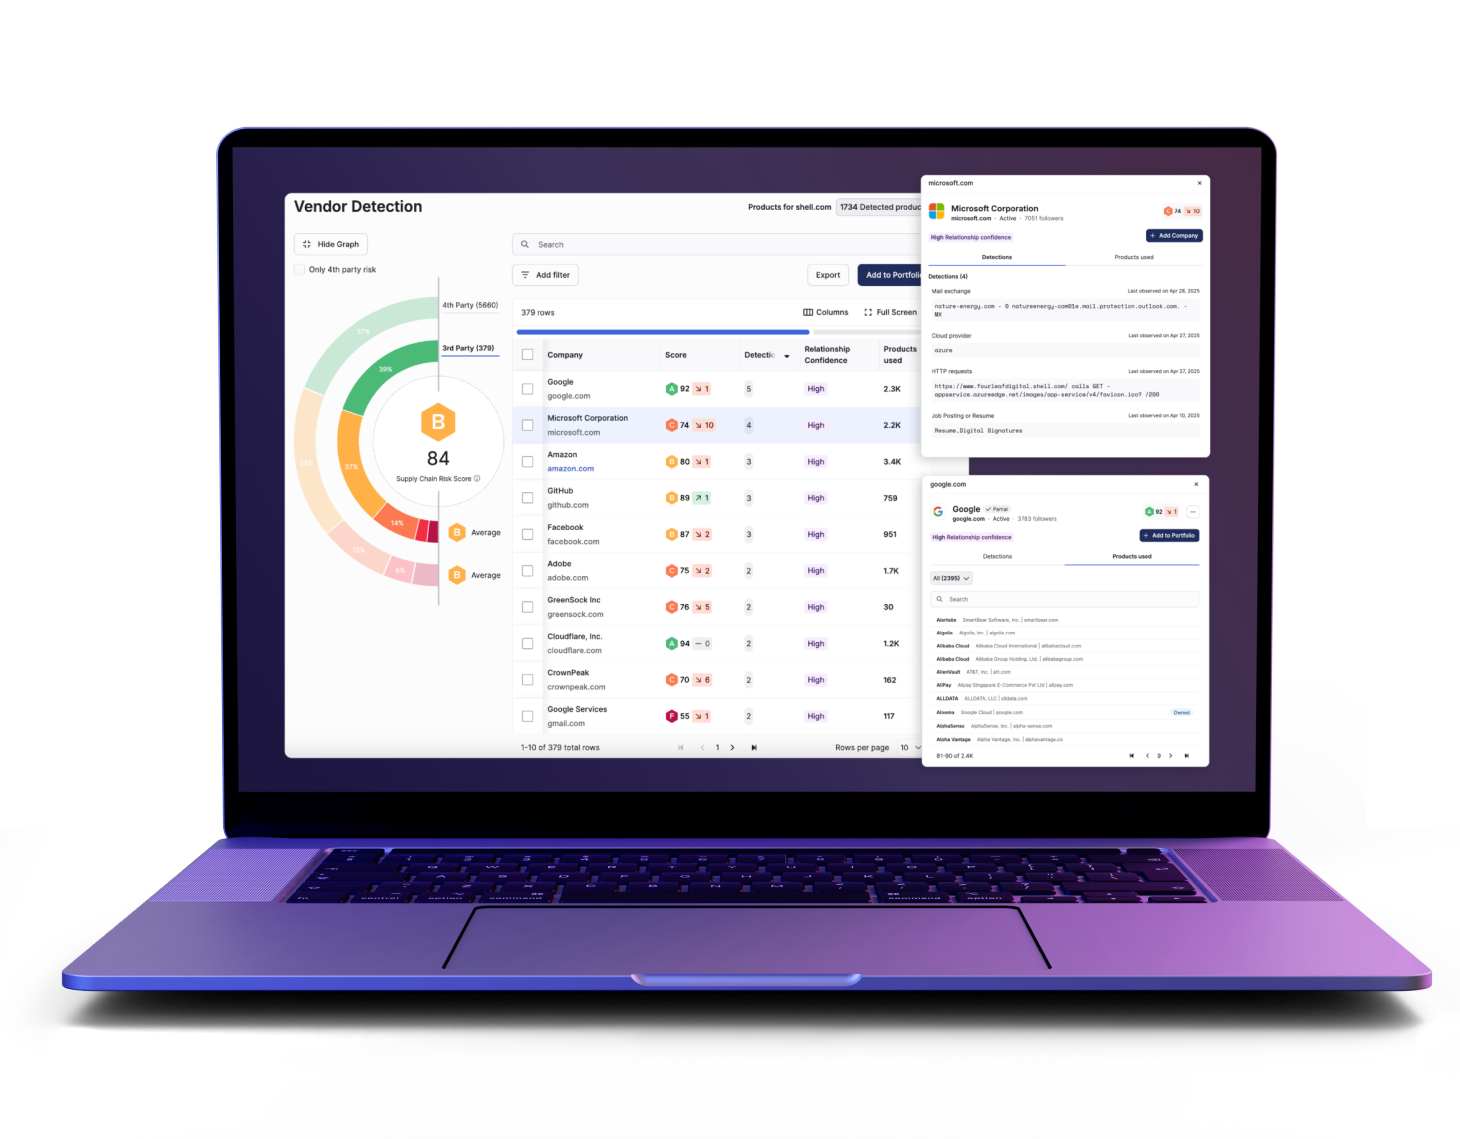
Identify compromises and vulnerabilities across your ecosystem using automatic vendor discovery and confidence scores.

Leverage our STRIKE team expertise to surface the findings adversaries are actually using today

Respond with confidence and Instantly understand your “blast radius” during an incident and use guided workflows to document response efforts for regulatory compliance.
Gain Unified Visibility and Real-Time Risk Reduction
Real-Time Vendor Risk Intelligence
Fourth-Party Concentration Risk
Focus on what matters
Full auditability and traceability
Coordinated Response
Remediation That Runs Itself
Empower Your Team to Lead with Timely and Accurate Data

Move from manual, reactive tracking to a proactive stance that reduces vendor friction and delivers clear, defensible risk reduction.

Discover – Third Party Vendor Ecosystem
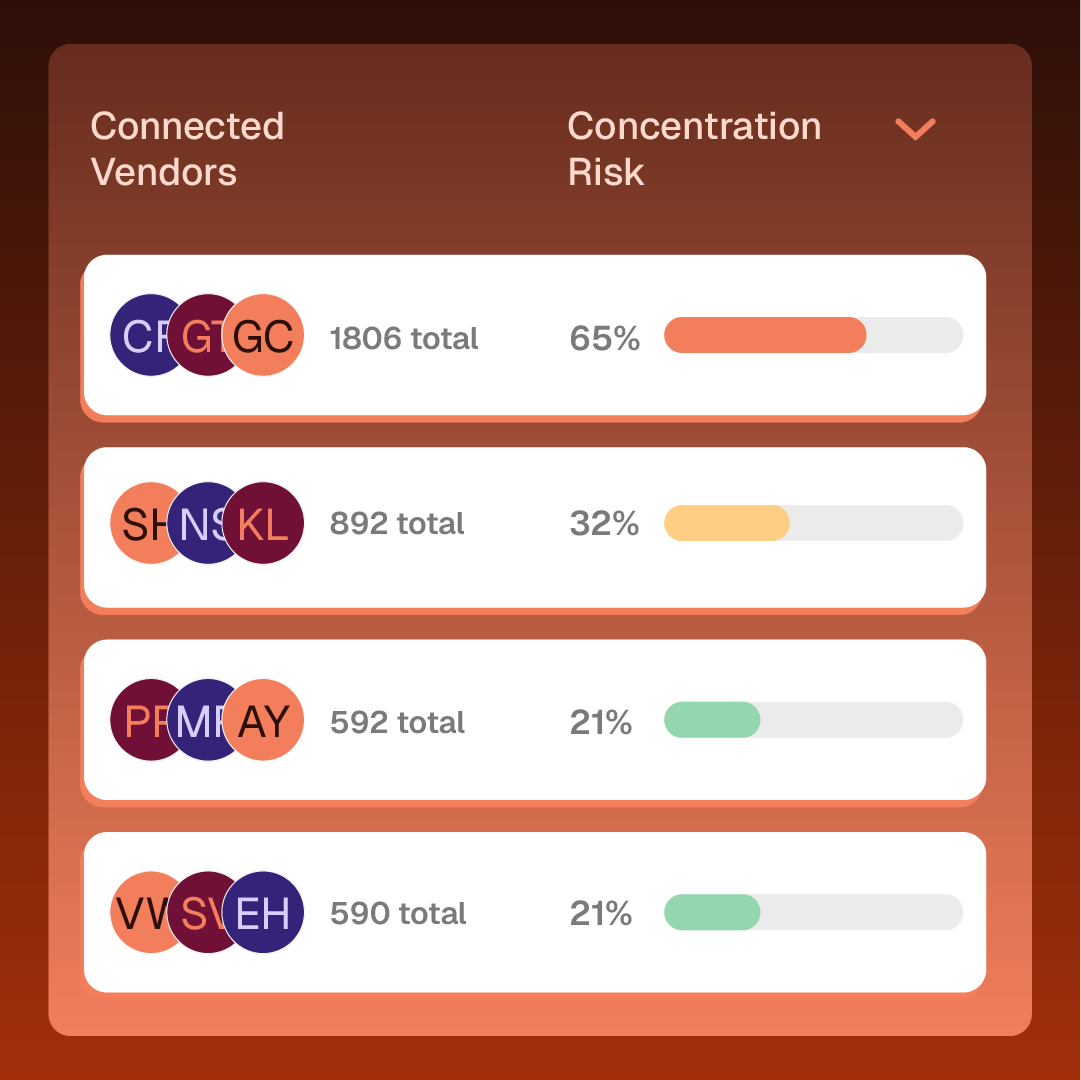
Automatically detect unknown vendors and map your extended attack surface, including 4th-party concentration risks.

Prioritize – Threat-informed Third Party Risk Management
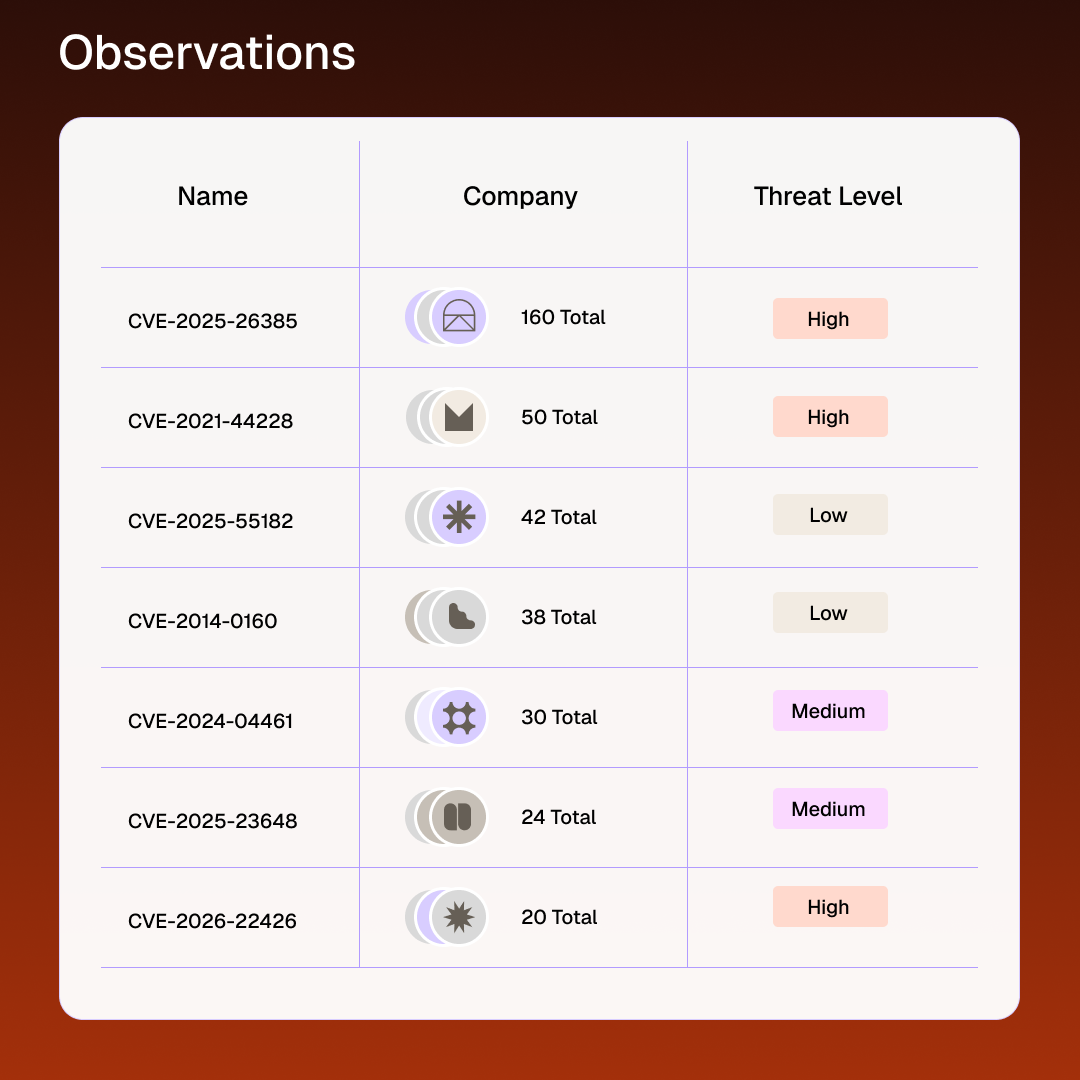
Apply policy-driven filters to security signals to isolate high-criticality issues, such as vulnerabilities on vendors with PII access.

Engage – Collaborate with Third Parties
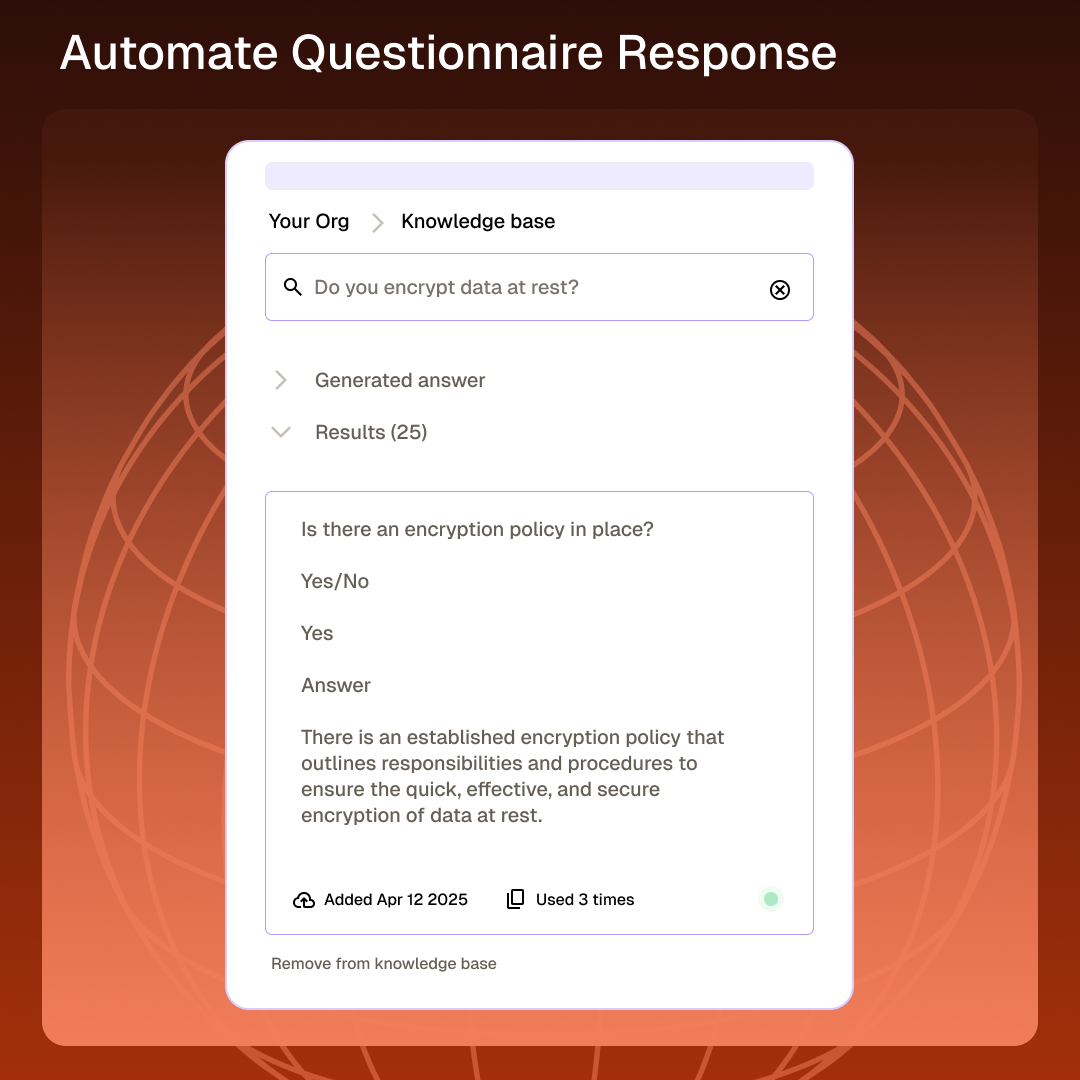
Eliminate email friction by using pre-managed contact lists and the Exchange Hub to request remediation or documentation directly in-platform.

Resolve – Track Vendor Remediation
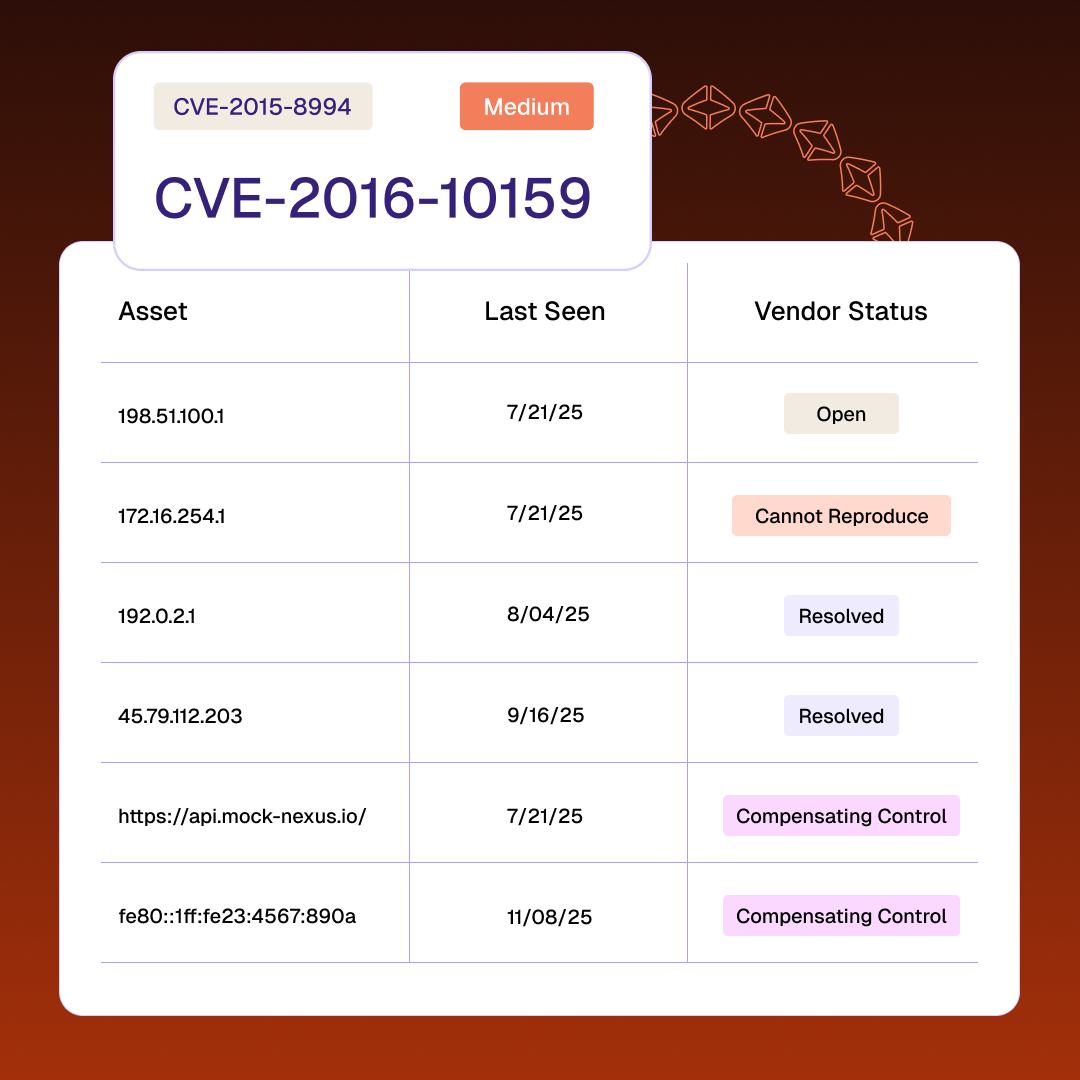
Map live threat intelligence to your ecosystem to generate executive insights and track vendor remediation through to completion.
Respond – One real-time events feed
The moment a breach or alleged breach touches your ecosystem, see it mapped to the specific vendors involved, then send a templated response request to every impacted vendor at once and watch replies update automatically.
Related resources
Frequently Asked Questions (FAQs)
Everything you need to know about starting your journey with TITAN Secure.
Find more answers in our help centerWhat is Threat-Informed TPRM?
Threat-Informed TPRM is a risk management approach that uses real-time intelligence and adversary tactics to prioritize assessments based on actual threats rather than generic compliance checkboxes.
We already get a lot of alerts. Won’t this just add more noise?
The default view isn’t every critical finding, it’s every critical finding adversaries are actually using right now, filtered by threat-informed presets built by our STRIKE team. You decide what breaks through, not the volume of what’s out there.
Can I communicate with vendors directly in the platform?
Yes, the Exchange Hub allows for “many-to-many” engagement and automated outreach to all impacted vendors regarding an incident.
How does this help with board reporting?
Dynamic reporting and AI-driven summaries translate technical findings into defensible, business-oriented insights for leadership and board meetings.