
Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library
Case Studies
CEDIA
Cómo CEDIA transformó la ciberresiliencia del ecosistema académico ecuatoriano con SecurityScorecard
Case Studies
MRS Brazil
Depoimento da MRS sobre como a SecurityScorecard trouxe visibilidade independente à postura de segurança externa da empresa, elevando o score a 100% e tornando a gestão de risco cibernético um indicador estratégico acompanhado por executivos e áreas técnicas.
Video
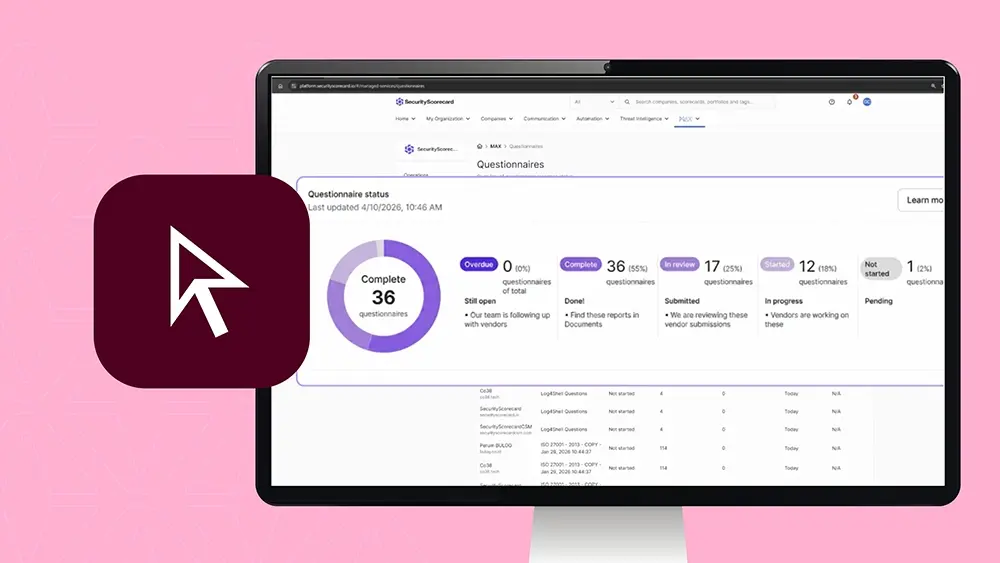
MAX Managed Questionnaires
In this installment of SecurityScorecard’s Demo Tuesday series, see MAX Managed Questionnaires in action and what your security program looks like when your team is free to focus on risk strategy instead of assessment admin.
Demo Tuesdays
Blog
What Is Cybersecurity M&A and Why It Matters
Cybersecurity M&A turns every deal into a cyber risk question. See what cybersecurity M&A is, why it matters, and the role of cyber due diligence.
Blog
LapDogs Is Back: Inside UAT-7810’s Expanding ORB Network and Its New Servers
Executive Summary: The latest Cisco Talos research shows these operators did not abandon the LapDogs ORB network after exposure. Instead, they appear to be continuing development through new tooling designed to manage, expand, and sustain compromised routers and other internet-facing devices. Cisco Talos published new research this week on UAT-7810, the threat actor behind LapDogs,
STRIKE Alert
STRIKE News
STRIKE Team
White Papers
Meeting BNM RMiT 2025: A Guide to Third-Party & Supply Chain Cyber Risk Requirements
On 28 November 2025, Bank Negara Malaysia issued one of the most significant overhauls to Malaysian financial sector cybersecurity regulation in recent years. The revised Risk Management in Technology (RMiT) policy expands who’s in scope, mandates continuous monitoring of third-party vendors, introduces SBOM requirements, and enforces stricter SLAs for incident disclosure and remediation. This white paper breaks down what changed, what it means for your third-party risk program, and how to operationalise and evidence the new obligations at scale.
28 Nov 2025 — the date RMiT was revised and reissued by BNM
New entities in scope — including certain non-bank merchant acquirers and intermediary remittance institutions
Continuous monitoring now mandatory — periodic, questionnaire-based assessment is explicitly no longer sufficient
12M+ entities rated across SecurityScorecard’s global intelligence network
RMiT 2025 isn’t a checkbox exercise. It’s a shift in how cyber risk is governed.
Video
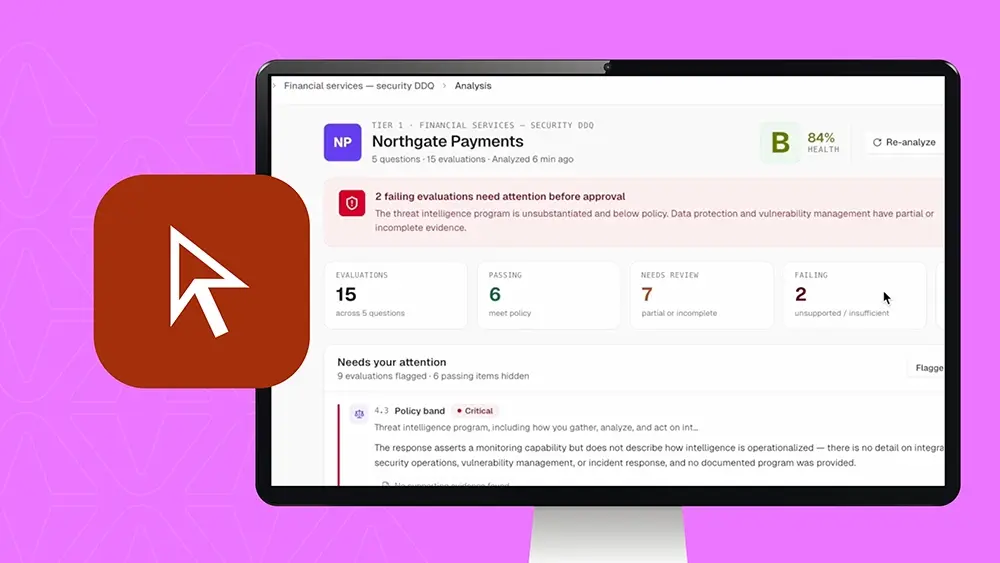
TITAN ASSESS: Send questionnaires
In Episode 5 of SecurityScorecard’s Demo Tuesday series, see how TITAN Assess streamlines the entire questionnaire outreach process — so your team spends less time on admin and more time acting on what vendors actually tell you.
Demo Tuesdays
Video
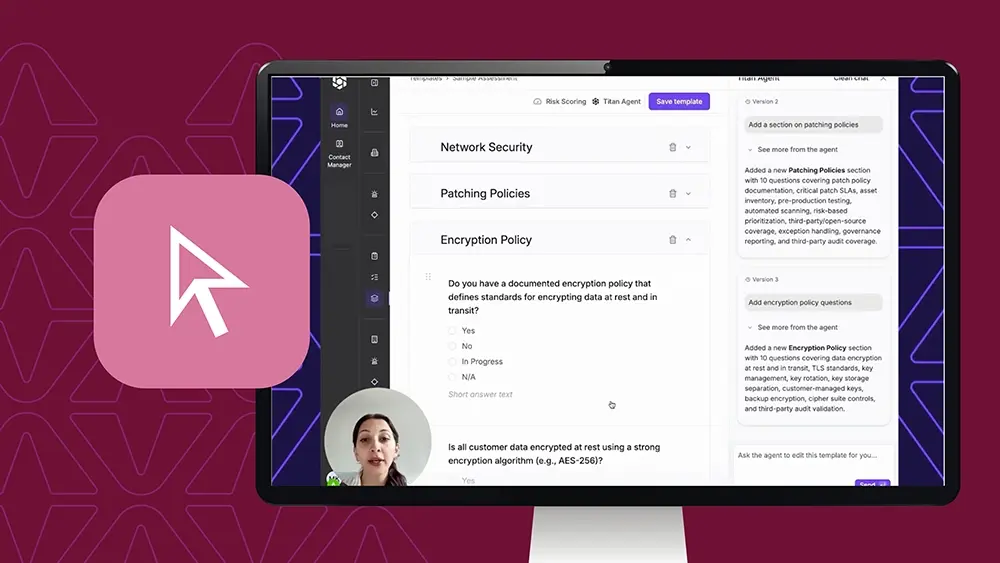
TITAN ASSESS: Building an Assessment Template with Titan Agent
In this installment of SecurityScorecard’s TITAN demo series, see how TITAN Agent uses AI to build customized, comprehensive assessment templates — so your team gets to evaluation faster and with more consistency across every vendor engagement.
Demo Tuesdays

Video
TITAN ASSESS: AI Pre-fill from Vendor Policies
In this installment of SecurityScorecard’s TITAN demo series, see AI pre-fill from vendor policies in action and find out how much faster your team moves through assessments when the manual work disappears.
Demo Tuesdays
Blog
What Is the Third-Party Risk Management Maturity Model
The third-party risk management maturity model turns vague TPRM goals into measurable stages. See the levels and how to move yours forward.

Video
TITAN WATCH: Introduction
In Episode 4 of SecurityScorecard’s Demo Tuesday series, get an introduction to TITAN Watch — and see how security teams are moving from stale, periodic reviews to continuous, always-on intelligence across their entire vendor ecosystem.
Demo Tuesdays
La résilience cyber en 2026: Pourquoi les chaînes d’approvisionnement sont en première ligne
Le rapport Global Cybersecurity Outlook 2026 du Forum économique mondial lance un avertissement clair aux dirigeants des secteurs public et privé: le risque cyber dépasse désormais les frontières du pare-feu. Le secteur public est particulièrement exposé à cette réalité. Les missions gouvernementales dépendent d’un réseau de fournisseurs, de prestataires de services managés, de plateformes cloud
Blog
How to Secure Your CI/CD Pipeline
Your CI/CD pipeline can ship a breach as fast as a feature. Learn the CI/CD pipeline security threats, controls, and practices that close the gap.
Ebook
The Questionnaire Trap
Your TPRM program was designed to reduce risk – but bloated questionnaires, annual audit cycles, and vendor fatigue may be doing the opposite. This eBook draws on candid insights from experienced risk management practitioners to help you escape the questionnaire trap and build a smarter, more effective vendor assessment program.
Learn how to shift from a checkbox-compliance mindset to an evidence-driven approach that actually reduces third-party risk. We’ll guide you through:
Understanding why more questions don’t equal more security – and the data that proves it.
Diagnosing the three failure modes that make most questionnaires ineffective.
Adopting a documentation-first model that cuts assessment time without sacrificing rigor.
Moving from calendar-driven audits to trigger-based TPRM that responds to real risk events.
Leveraging AI as a force multiplier – while keeping human judgment where it belongs.

Video
AI Agents – KEV Remediation
In Episode 3 of SecurityScorecard’s Demo Tuesday series, see how TITAN AI Agents automate KEV remediation workflows — so your team spends less time triaging and more time closing exposures.
Demo Tuesdays
Blog
How Open Source Risk Threatens Your Vendors
Open source risk follows every vendor into your supply chain. See where it hides, how attackers exploit it, and what continuous monitoring solves.
Blog
How State-Sponsored Cyber Attacks Use Third Parties
State-sponsored cyber attacks increasingly target vendors to reach high-value organizations. Learn how nation-state actors exploit third parties and how to defend.

Video
TITAN AI Demo Series: Unlocking the Driftnet API for Deeper Third-Party Visibility
In the latest installment of our Demo Tuesday series, learn how the Driftnet API gives TPRM, SOC, and threat hunting teams real-time visibility into third-party exposures before attackers exploit them.
Demo Tuesdays
Blog
Identity-Based Attacks and Third-Party Risk
Identity attacks now account for 59% of breaches, and vendors are the fastest-growing entry point. Learn how to protect your supply chain.
Blog
The World Cup Has 48 Teams. Adversaries Are Playing Too.
During the 2020 Tokyo Olympics, held in 2021 after a pandemic-forced delay, NTT Corporation recorded approximately 450 million cyberattack attempts targeting Olympic systems. The 2022 FIFA World Cup in Qatar drew similar attention from state-aligned threat actors and opportunistic criminals. The 2026 tournament, spanning three nations, 16 cities, and several million projected visitors, will be
Blog
Compliance vs Security: What Passing an Audit Misses
Compliance vs security explained. A passed audit proves controls existed on one day, not that you are secure. Close the gap.