Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library
メディア掲載
第三回 ランサムウェア攻撃に備えよ、企業が築くべきサイバーレジリエンスの新基準:ランサムウェア対策は予測の時代へ―AIとデータ活用が防御を変える
Learn more in this resource.
Japanese
メディア掲載
第2回:なぜ攻撃対象に?エージェンティックAIで広がる攻撃対象領域
Learn more in this resource.
Japanese
寄稿記事
「そこが動かなくなると会社全体が止まる」 意外と見えない自社の急所をあぶり出すサイバー対策5つのポイント
Learn more in this resource.
Japanese
メディア掲載
リスクが見えても人手が足りない米国、リスクが見えてすらいない日本 サプライチェーン防衛の現実
Learn more in this resource.
Japanese
メディア掲載
第1回:エージェンティックAIとは?権限を持つAIがもたらすリスクの拡大
Learn more in this resource.
Japanese
メディア掲載
第二回 ランサムウェア攻撃に備えよ、企業が築くべきサイバーレジリエンスの新基準:サプライチェーン攻撃はなぜ防げない?企業が取るべき「レジリエンス戦略」
Learn more in this resource.
Japanese
メディア掲載
SecurityScorecard「TITAN AI」発表 サードパーティリスク管理をAI駆動に
Learn more in this resource.
Japanese
寄稿記事
「もらい事故でした、申し訳ありません」では済まない、”他社”で発生したサイバー攻撃による被害の厳しい現実
Learn more in this resource.
Japanese
メディア掲載
「第一回:ランサムウェア攻撃に備えよ、企業が築くべき“サイバー レジリエンス”の新基準」 初動・復旧・信頼回復の全体設計 – “防げない”前提で備えよ
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(3)「侵害は社外で始まる」 クラウドや取引先に“潜伏する”脅威と、求められるセキュリティ再設計
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(2)ネットワーク境界防御では防げない、大損害をもたらす「外部侵入口」への対処法
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(1)ランサムウェアやDDoSで連鎖被害も? 再々委託先までのリスク管理が不可欠になった訳
Learn more in this resource.
Japanese
Blog
AI Security Cannot Depend on Everyone Slowing Down
Frontier labs are calling for the industry to slow down. Our adversaries didn’t get the memo. The world’s first benchmark for AI in third-party risk management shows what we should be building instead: measurement, not just restraint.

Press
SecurityScorecard website wins Best Technology Website of 2026 from WEBAWARD
SecurityScorecard builds a bespoke, bold, accessible cybersecurity brand experience.
Press
SecurityScorecard Names Sarah Walker President as Company Expands Its Mission for the AI Era
SecurityScorecard Names Sarah Walker President as Company Expands Its Mission for the AI Era
Ebook
The Perfect Scorecard
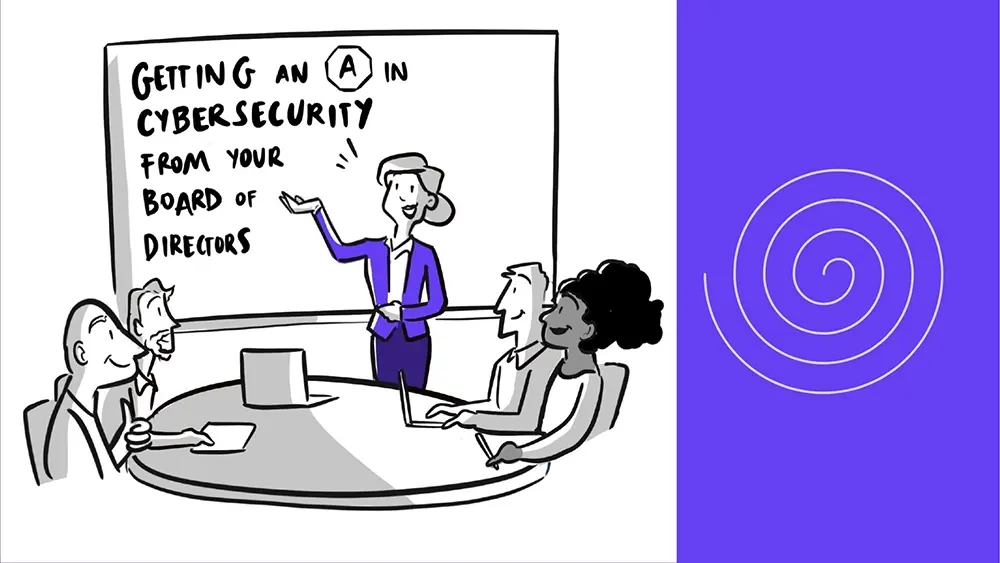
Getting an “A” in Cybersecurity From Your Board of Directors
There’s a growing communications gap between corporate boards and CISOs — and it’s putting companies at risk. This book brings together over a dozen top CISOs, CEOs, board members, and advisors to close the gap, chapter by chapter.
A Carnegie Mellon University survey found that 77% of U.S. board members rarely or never received senior leadership reports on digital privacy or security risk. Cyber risk has since become a top-tier business risk — yet most boards and CISOs still speak different languages. As the book puts it: CISOs are from Mars, and board members are from Venus.
What’s inside
How to tell if you have the right cybersecurity leader and how to test your CISO
A practical playbook for board-CISO communication, built for the boardroom, not the SOC
How to talk about ransomware, cyber insurance, and “wartime” security operations in terms the board understands
A Digital Trust Framework for managing cybersecurity as a business risk, not just an IT problem
Why trust, not just technology, is the foundation of a CISO’s success with the board
Who it’s for
CISOs and security leaders preparing for board conversations, board members and executives responsible for cyber risk oversight, and risk, compliance, and governance teams navigating the CISO-board relationship.
You’ll walk away with insights on how security executives can best communicate to the board, and what board members need to know to assess their security executives.
Video
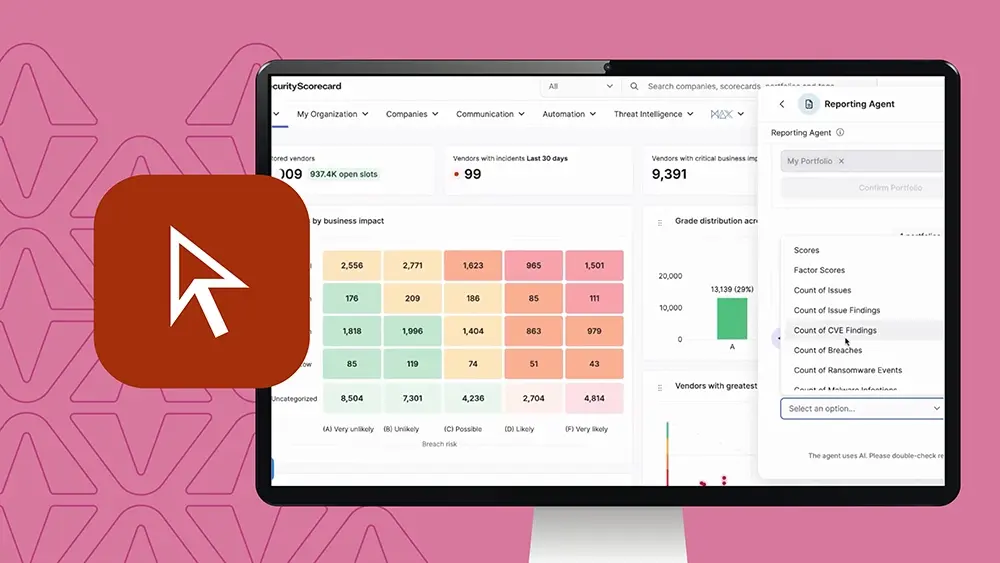
TITAN Watch – Reporting (Reporting Agent)
See how TITAN AI’s Reporting Agent turns risk data into charts and reports in minutes, without manual exports or chart-building.
Demo Tuesdays
Blog
How to Present Cyber Risk to the Board: A CISO’s Reporting Framework
CISOs now face direct board accountability for vendor risk. Here’s a practical framework for turning security data into a board-ready risk narrative — with a template to get started.
Video
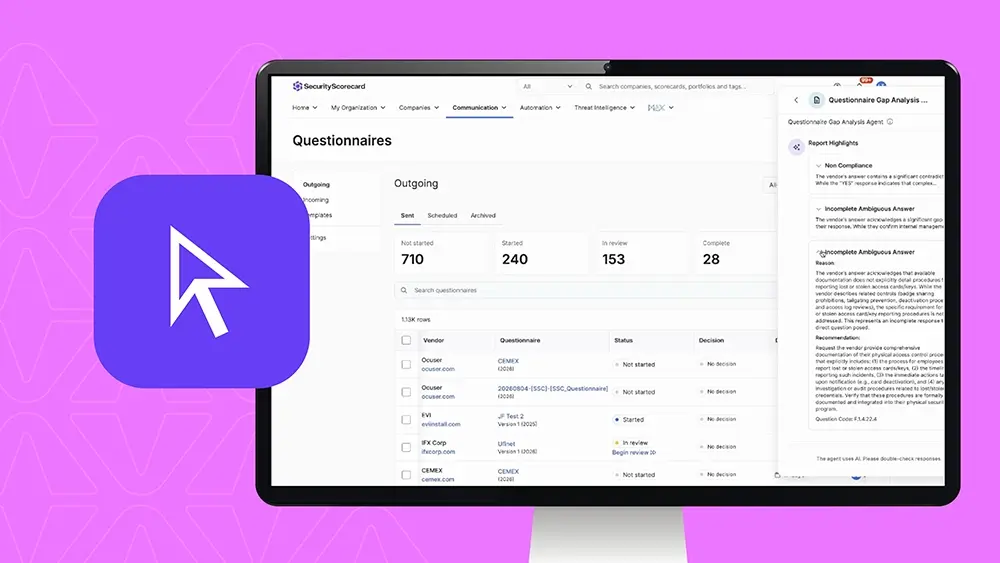
TITAN Watch – Questionnaire Gap Analysis Agent
See how TITAN AI’s Questionnaire Gap Analysis Agent flags compliance gaps between vendor questionnaire responses and real security data.
Demo Tuesdays
Video
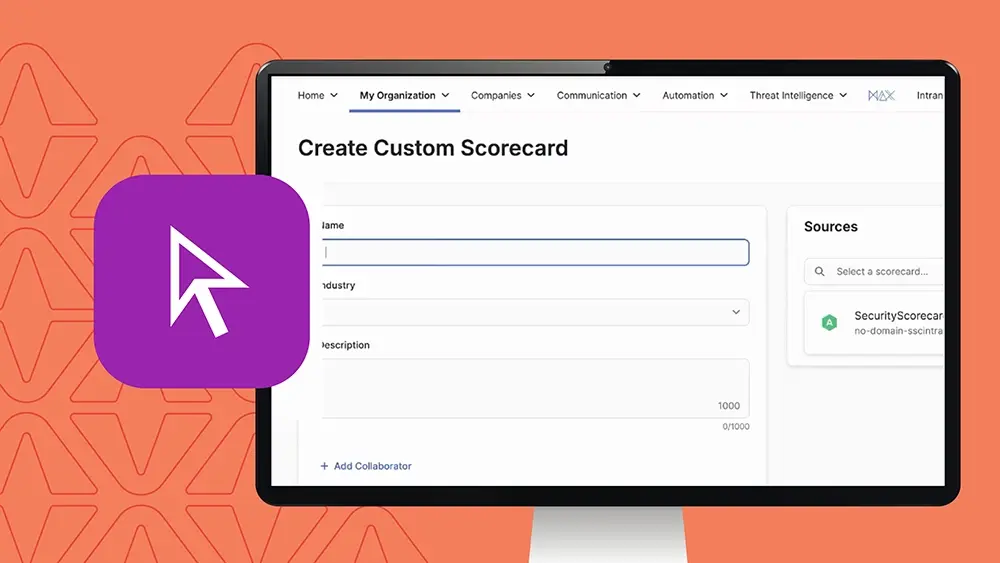
TITAN Watch – Custom Scorecards
Learn how to build custom scorecards in SecurityScorecard to segment domains, IPs, and geolocations and monitor the risk that matters most to you.
Demo Tuesdays
Blog
AI Agents in TPRM: What They Actually Do (and What They Don’t)
AI agents in TPRM do more than summarize findings. See what agentic AI actually automates in a third-party risk program — and how to tell real from hype.