Resources
Blog
Resource Library
April 27, 2026
Why SMBs Need Continuous Vendor Risk Monitoring
Annual vendor audits leave SMBs vulnerable. Learn why continuous monitoring catches threats before they become breaches.
April 21, 2026
Rethinking the Questionnaire: Why Better Tech and More People Won’t Clear Your TPRM Backlog
Assessment backlogs are a common challenge for Third-Party Risk Management (TPRM) programs. Most organizations tackle the problem by increasing their capacity through hiring or improving efficiency with technology. While both are important elements of the solution, organizations also need to implement the right process for prioritizing the necessary business outcomes. This is especially true for
MAX
April 20, 2026
Attack Surface Visibility Finds Third-Party Risks First
Attack surface visibility reveals third-party risks before attackers exploit them. Learn how continuous monitoring protects your entire vendor ecosystem.
April 20, 2026
What Is Supply Chain Security?
Learn what supply chain security is, why it matters, and proven strategies to protect your organization from third-party breaches and vendor vulnerabilities.
April 13, 2026
What Is Network Security?
Learn what network security is, why it matters, and how to protect your organization from cyber threats with proven strategies and tools.
April 10, 2026
What Are Indicators of Compromise (IOCs)?
An indicator of compromise (IOC) is forensic evidence of a breach. Learn the types of IOCs, how they differ from IOAs, and how teams use them.
April 9, 2026
Introducing SecurityScorecard AI Agents
Transform your vendor risk management with new SecurityScorecard AI Agents. Learn how to automate security questionnaire management, gain real-time threat insights, and accelerate remediation to stay ahead of emerging cyber threats.
April 6, 2026
What Is a DNS Sinkhole?
Learn what a DNS sinkhole is, how it blocks malicious traffic, and why security teams use sinkholing to neutralize botnets and protect their networks.
April 1, 2026
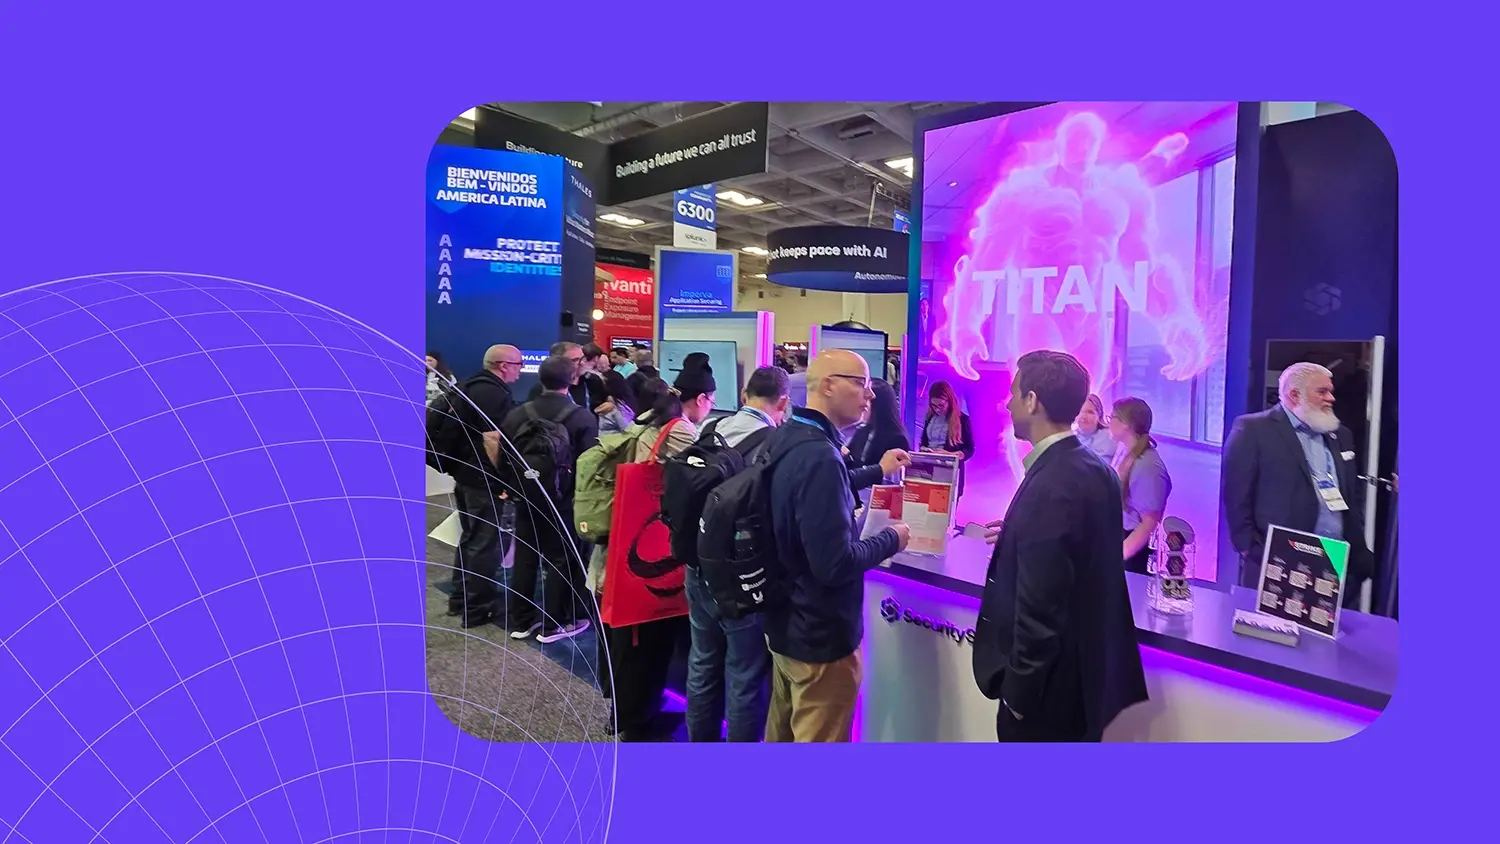
RSAC 2026 Recap: What Did RSAC 2026 Reveal About the Future of TPRM? SecurityScorecard’s TITAN AI Sets the Pace
CEO and Co-Founder Dr. Aleksandr Yampolskiy, CISO Steve Cobb, and SecurityScorecard leaders joined chief information security officers (CISOs), partners, and industry experts at RSAC 2026 to discuss how AI, threat intelligence, and continuous monitoring are reshaping third-party risk management (TPRM). RSAC 2026 reinforced a growing gap between how organizations manage third-party risk and how that
March 31, 2026
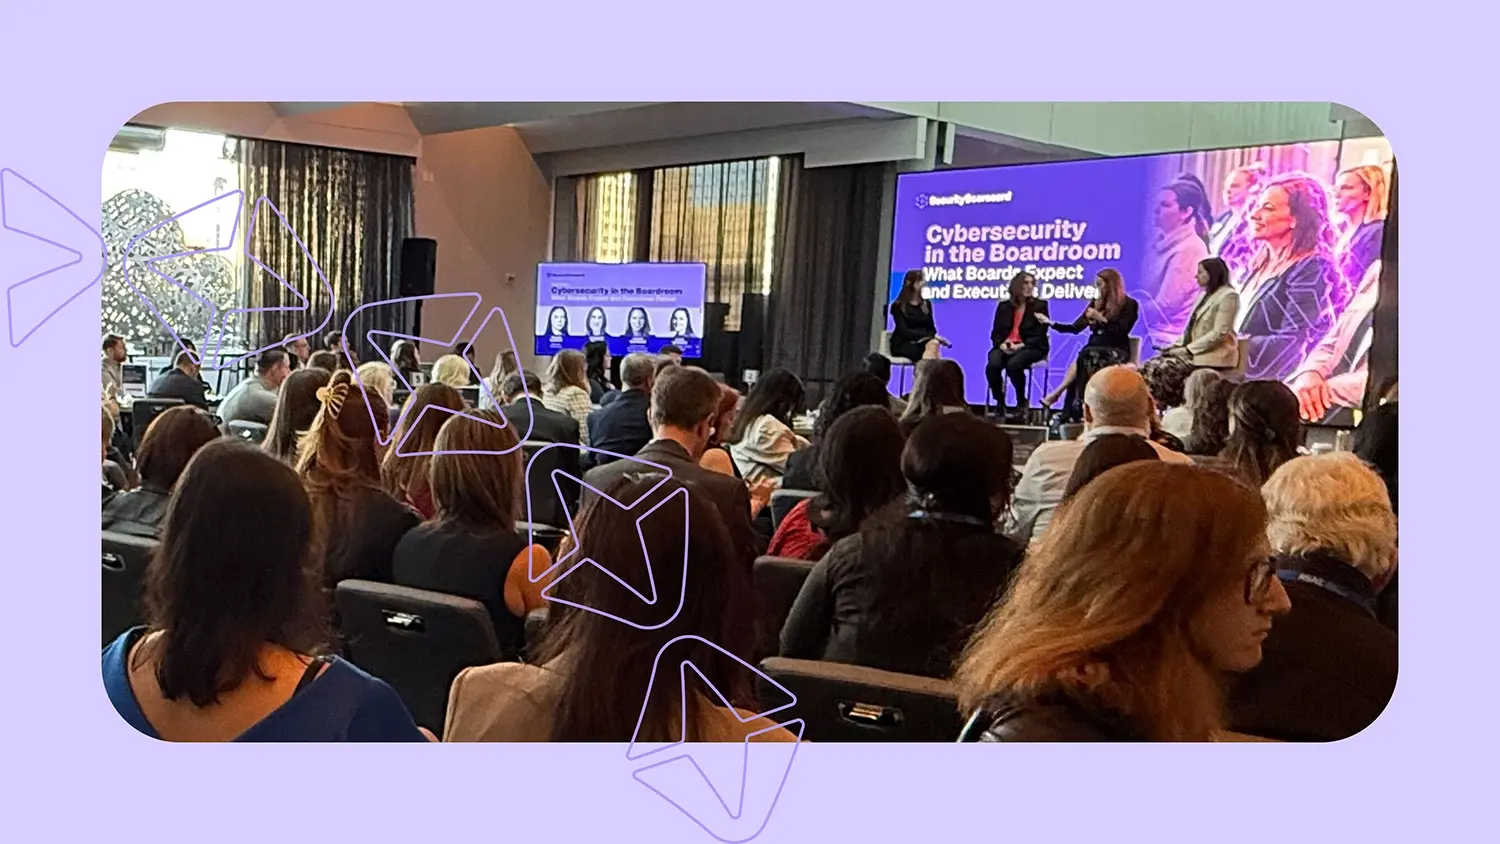
AI Is Reshaping Cyber Risk in 2026: Why Boards Must Take Ownership Now
Cybersecurity leaders must accept a hard truth: AI has already broken the traditional model of defense in 2026. Attackers now operate faster, at lower cost, and at greater scale than most organizations can handle. The only viable response is to rethink security as a continuous, business-driven risk function. This shift defined a recent panel at
March 31, 2026
Iran Conflict and the Expanding Cyber Front: What Government Leaders Need to Know
When conflict escalates in the Middle East, the battlefield is never limited to geography. It extends into energy grids, government networks, transportation systems, and financial infrastructure. The current war involving Iran is no exception. While missiles and airstrikes dominate headlines, the parallel cyber dimension may prove equally consequential, particularly for regional governments, critical infrastructure operators,
March 31, 2026
SecurityScorecard Appoints Dean Sysman to Board of Directors
SecurityScorecard today announced that Dean Sysman, Co-Founder and Executive Chairman of Axonius, has joined its Board of Directors as an independent director. Dean is one of the most respected builders in cybersecurity today. Sysman co-founded Axonius and scaled it into a leader in cyber asset management. The platform helps organizations maintain accurate asset inventories, reduce
March 30, 2026
What Is a Honeypot in Cybersecurity?
Learn what a honeypot is in cybersecurity, how it works to detect threats, and why security teams use honeypots to gather attacker intelligence.
March 27, 2026
What Is the CAIQ Questionnaire? A Clear Guide
The CAIQ questionnaire documents a cloud provider’s security controls. Learn how it works and how to finish it without the grind.
March 26, 2026
RSAC 2026 Talk: Transforming Third-Party Risk Management From Compliance Checkboxes to Security Resilience
The traditional approach to managing supply chain risk is broken. For years, organizations have relied on annual questionnaires and static attestations to “check the box” for compliance. However, as SecurityScorecard CISO Steve Cobb highlighted in his RSAC 2026 talk, “The Outside-In Advantage: Modernizing TPRM with AI and Threat Intelligence,” 90% of security practitioners lack confidence
March 24, 2026
SecurityScorecard and Dataminr Partner to Deliver Preemptive Cyber Defense for the Enterprise
Combining third party risk and external attack surface management with client-tailored threat intelligence to help organizations stop threats before they strike.
March 23, 2026
Supply Chains Are the New Front Line for Cyber Resilience
Supply chains are the top cyber resilience challenge in 2026. See how continuous monitoring and threat-informed vendor risk management protect your operations.
March 20, 2026
How to Reduce Security Questionnaire Fatigue
Answering the same security questionnaires is wearing your team out. Reduce security questionnaire fatigue with these fixes.
March 16, 2026
What Is Application Security and Best Practices for it?
Learn what application security is and why your vendors’ AppSec gaps become your risk. Learn how continuous monitoring protects your supply chain.
March 9, 2026
What Is a Supply Chain Attack?
Learn how a supply chain attack works, why it’s so dangerous, and what security measures can help protect your organization from hidden threats.
Supply Chain Cyber Risk
Threat-Informed TPRM
February 25, 2026
What the Mississippi Ransomware Attack Means for Healthcare and How to Protect Critical Infrastructure
A ransomware attack shut down clinics across Mississippi. Learn how healthcare and critical infrastructure can prevent supply chain-driven cyber disruptions.