Video

Titan AI: The AI Operating System for End-to-End Third Party Risk Management

Titan AI: The AI Operating System for End-to-End Third Party Risk Management
Third Party Risk Management Is at an Inflection Point

Third party risk management is at an inflection point, and traditional programs aren’t keeping up. Your company trusts hundreds of vendors. Each of them trusts hundreds more. Nearly half of all breaches now come through a third party and most TPRM programs still run on a ratings tool, a questionnaire tool, and a spreadsheet stitched together by hand. Visibility alone isn’t enough to reduce risk and static annual questionnaires may miss something that happens the next day. The seams are where risk slips through. Legacy TPRM and GRC tools were built for a slower threat landscape. Today, AI powered attackers move at machine speed and exploits land in hours, not months. Meanwhile, every CISO wants three numbers every day. How much risk did we actually reduce today? What efficiencies did we create? And how much time did we save? Risk doesn’t stand still, and neither do we. Introducing Titan AI, the first and only AI operating system for end to end third party risk management. Threat informed, grounded in what’s happening now, not a historical estimate. Continuous twenty four seven with no blind spots between annual snapshots. Predictive surfacing risk while there’s still time to act. And AI driven, taking manual work off your team’s plate. Titan watch, assess, and secure now run as one connected workflow. Here’s what that looks like for one vendor. Meet Northbridge payroll, your payroll provider. Critical tier. Tuesday 09:04AM. A new critical finding appears on one of their internet facing servers. Titan Watch flags it the moment it’s detected. No waiting for next year’s review. Then Titan goes one layer deeper. Northbridge runs its file transfers through RelayFTP. A fourth party that isn’t in your inventory, isn’t in your contracts, and has never been assessed. Until now, nobody knew it was there. Because Northbridge is critical, the workflow fires on its own. Titan assess sends the right questionnaire for that tier, prefilled from the vendor’s own policies, so they answer fewer questions. When the answers come back, the review agent checks everyone against Northbridge’s SOC two report and your policies. 19 controls pass. One doesn’t. They say they patch critical vulnerabilities in fourteen days. Their audit report says 30. That’s the only thing a human needs to look at. Assessment review goes from six or seven hours to minutes. Thursday, a zero day in RelayFTP’s software is exploited in the wild. Normally, this is the fire drill. Manual searches, mass emails, a spreadsheet of who replied. Titan Secure is already on it. The event lands in your security events feed and Titan maps the blast radius. Northbridge and 41 other vendors that depend on the same software. Threat informed presets cut thousands of findings down to the handful tied to this active campaign. Then the response agent sends one remediation request to every impacted vendor at once, tracks every reply in the exchange hub, and follows up with anyone who goes quiet. When Northbridge patches, Titan rescans. The vulnerability is gone, so the finding closes. Verified by an independent rescan, not the vendor’s word for it. Friday morning, your CISO asks the question every board asks. Are we exposed? The reporting agent already has the answer. How urgent it was, how fast the response moved, and how responsive your vendors were. Export it straight into the board deck. One finding, one fourth party nobody knew about, one questionnaire nobody had to chase, one breach contained across every affected vendor before Friday. See every vendor, understand actual risk, prioritize what matters, remediate it automatically, prove it to the board. This is Titan end to end. Welcome to Titan AI.
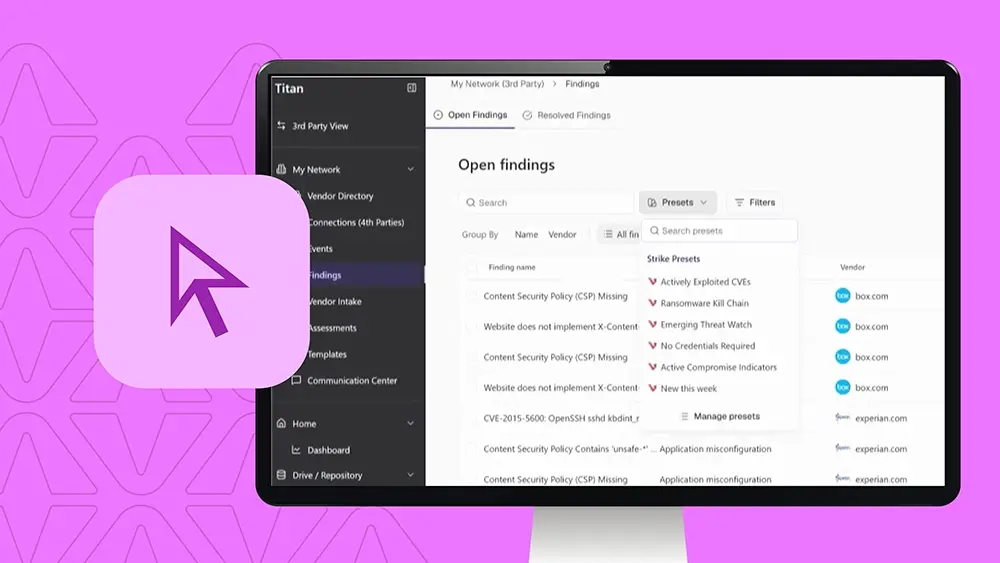
Traditional programs aren’t keeping up. Your company trusts hundreds of vendors. Each of them trusts hundreds more.

Nearly half of all breaches now come through a third party, and most TPRM programs still run on a ratings tool, a questionnaire tool, and a spreadsheet stitched together by hand. Visibility alone isn’t enough to reduce risk, and static annual questionnaires may miss something that happens the next day. The seams are where risk slips through.

Legacy TPRM and GRC tools were built for a slower threat landscape. Today, AI-powered attackers move at machine speed, and exploits land in hours, not months.

Meanwhile, every CISO wants three numbers every day:

  • How much risk did we actually reduce today?
  • What efficiencies did we create?
  • How much time did we save?

Introducing Titan AI

Risk doesn’t stand still, and neither do we.

Titan AI is the first and only AI operating system for end-to-end third party risk management.

  • Threat informed: Grounded in what’s happening now, not a historical estimate.
  • Continuous: 24/7, with no blind spots between annual snapshots.
  • Predictive: Surfaces risk while there’s still time to act.
  • AI driven: Takes manual work off your team’s plate.

Titan Watch, Titan Assess, and Titan Secure now run as one connected workflow. Here’s what that looks like for one vendor.

Tuesday, 9:04 AM: Titan Watch Detects a Critical Finding

Meet Northbridge Payroll, your payroll provider. Critical tier. A new critical finding appears on one of their internet-facing servers.

Titan Watch flags it the moment it’s detected. No waiting for next year’s review.

Then Titan goes one layer deeper. Northbridge runs its file transfers through RelayFTP, a fourth party that isn’t in your inventory, isn’t in your contracts, and has never been assessed. Until now, nobody knew it was there.

Titan Assess Automates the Review

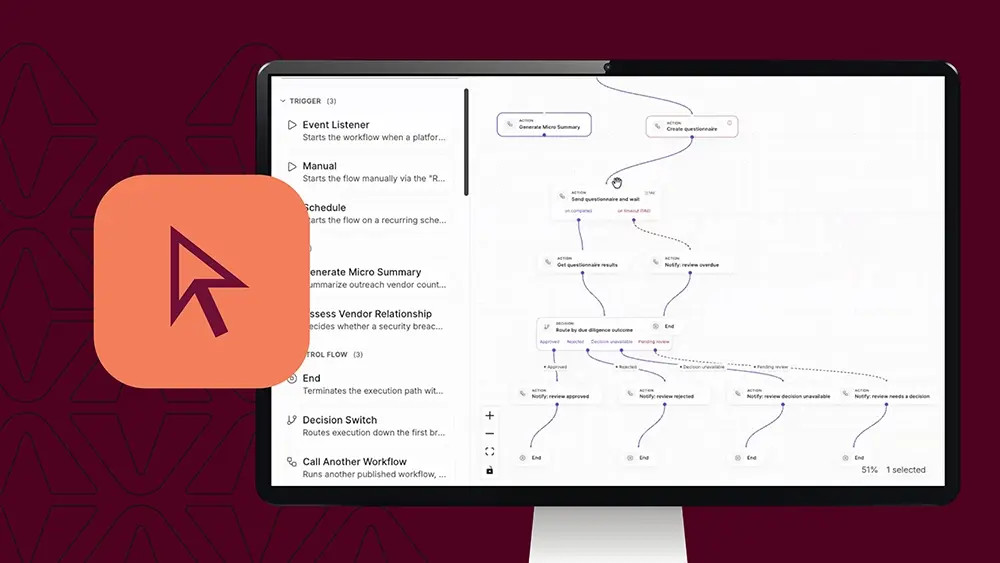
Because Northbridge is critical, the workflow fires on its own.

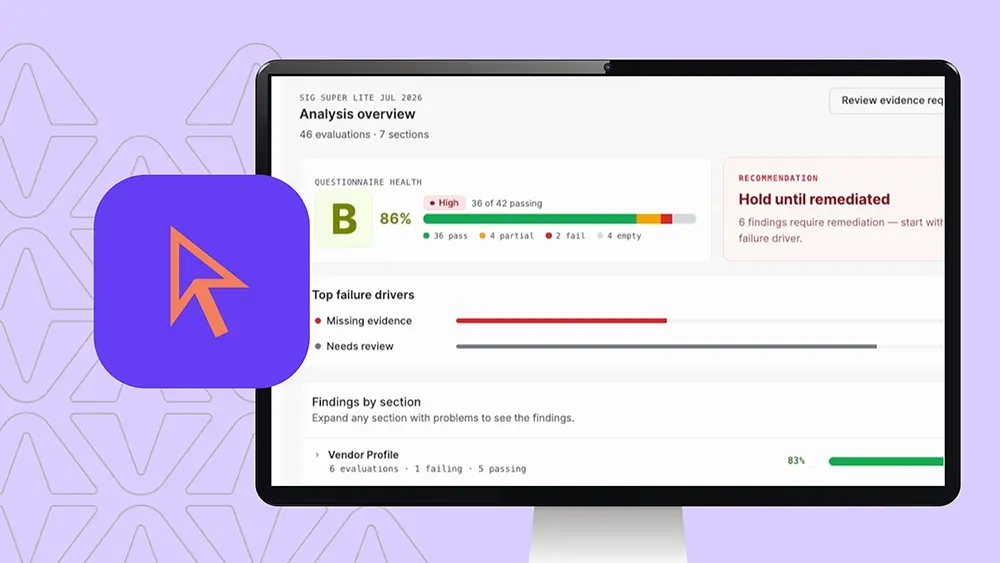
Titan Assess sends the right questionnaire for that tier, prefilled from the vendor’s own policies, so they answer fewer questions. When the answers come back, the review agent checks everything against Northbridge’s SOC 2 report and your policies. 19 controls pass. One doesn’t.

Northbridge says it patches critical vulnerabilities in 14 days. Its audit report says 30. That’s the only thing a human needs to look at.

Assessment review goes from six or seven hours to minutes.

Thursday: Titan Secure Responds to a Zero-Day

A zero-day in RelayFTP’s software is exploited in the wild. Normally, this is the fire drill: manual searches, mass emails, a spreadsheet of who replied. Titan Secure is already on it.

  • Blast radius mapped: The event lands in your security events feed, and Titan identifies Northbridge and 41 other vendors that depend on the same software.
  • Threat-informed presets: Thousands of findings are cut down to the handful tied to this active campaign.
  • Automated response: The response agent sends one remediation request to every impacted vendor at once, tracks every reply in the exchange hub, and follows up with anyone who goes quiet.

When Northbridge patches, Titan rescans. The vulnerability is gone, so the finding closes. Verified by an independent rescan, not the vendor’s word for it.

Friday Morning: Proving It to the Board

Your CISO asks the question every board asks: Are we exposed?

The reporting agent already has the answer: how urgent it was, how fast the response moved, and how responsive your vendors were. Export it straight into the board deck.

Titan End to End

  • One finding.
  • One fourth party nobody knew about.
  • One questionnaire nobody had to chase.
  • One breach contained across every affected vendor before Friday.

See every vendor, understand actual risk, prioritize what matters, remediate it automatically, and prove it to the board. This is Titan end to end.

Welcome to Titan AI.