Two flaws in PHP itself
In the first flaw, an out-of-memory interruption can leave partially initialized request data that PHP later uses during cleanup. In the second, request-owned state can persist after its memory is freed, then be accessed by a later request handled by the same worker. The PHP advisories describe confirmed remote code execution against Apache mod_php; they also document a validated PHP-FPM session lifecycle path for the second flaw. Applicability varies by SAPI, configuration, and request path. Read the upstream advisory.
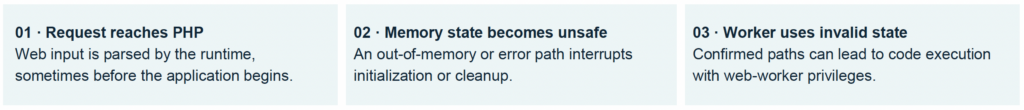
Conceptual diagram based on the 109618 and 109619 PHP project advisories; it is not an exploit sequence.
2.71M IPs advertised a PHP build below the upstream fix
In the same 30-day window, Driftnet identified 2,705,148 distinct IPs with an upstream-vulnerable PHP version string on at least one observed service. Within that cohort, 2,022,485 advertised an upstream unsupported branch. A separate exact-build query found 3,674 distinct IPs advertising one of the four fixed upstream releases.

The version test uses PHP’s fixed thresholds: 8.2.35, 8.3.36, 8.4.27 and 8.5.12; older released branches have no upstream update. It gives responders a version-based priority cohort. Validate the running package or provider advisory to establish patch state, including vendor backports.
Source: Driftnet version-status query receipt and PHP’s fixed-release advisory. These are independent distinct-IP cohorts, not parts of a pie: one IP can host multiple PHP services or show both a below-fix and fixed build during the window.
A 7.67M-IP PHP footprint
The exact Driftnet product-tag:php search identifies 7,669,724 distinct IPs seen in a 30-day window. An independent PHP CPE query returns 7,664,924 distinct IPs. Generic PHP CPEs and Apache/PHP Server banners add useful entry points for runtime and deployment review.
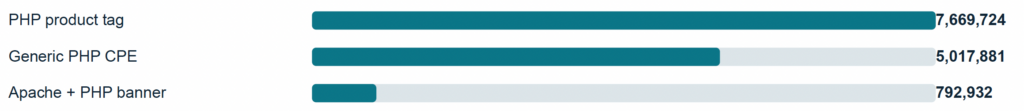
Source: authenticated Driftnet 30-day query receipt. Each query deduplicates IPs within the fixed window; query populations can overlap.
From this global starting point, analysts can pivot to version, deployment, network and verified ownership context to direct remediation.
Multiple signals, millions of leads
Driftnet found 2,818,686 distinct IPs with PHP in an HTTP header, 1,539,338 with a PHPSESSID header marker, and 851,447 with PHP in the Server banner during the same 30-day window. These detection channels help analysts corroborate the technology and pivot to a specific service.
Corroborating PHP signals
Distinct IPs per signal query · fixed 30-day window
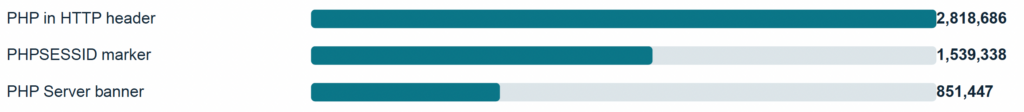
Source: Driftnet distinct-IP query receipt. A service may contribute to several signal cohorts.
The long tail is visible by branch
The largest individual branch cohort is PHP 7.4 on 551,860 distinct IPs. PHP 8.3 and 8.2 each exceed a quarter-million IPs, while older PHP 5.x and 7.x branches remain prominent. This branch-level view lets teams sort runtime investigations against the PHP project’s fixed-release matrix.
PHP branch footprint
Distinct IPs in each PHP CPE branch query · fixed 30-day window
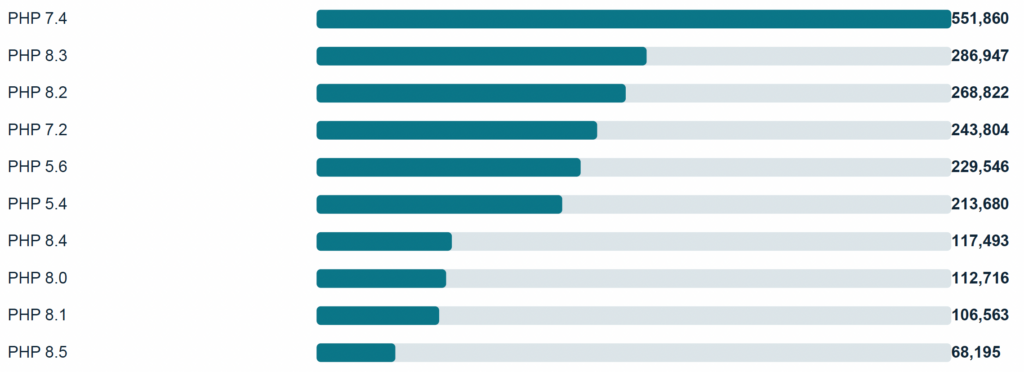
Source: Driftnet branch query receipt. Each branch is independently deduplicated; an IP hosting multiple PHP services can appear in more than one row.
Apache/PHP stands out in the banner data
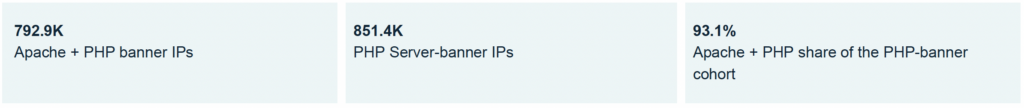
792,932 distinct IPs displayed both Apache and PHP in a Server banner during the 30-day window. That is 93.1% of the
851,447 IPs with PHP in a Server banner. It creates a focused cohort for SAPI and application-path validation.
Deployment signal
Distinct IPs per Server-banner query · fixed 30-day window

Source: Driftnet 30-day distinct-IP query receipt. Banner evidence guides targeted deployment validation.
Where PHP-tagged IPs concentrate
Driftnet’s 30-day product-tag:php query returned 7,669,724 globally distinct IPs. Country-specific unique-IP queries place the largest cohorts in the United States (1.69M), France (1.20M) and Germany (828.6K). The same search can pivot into routing networks for provider-level follow-up.
PHP-tagged unique IPs by country
Distinct IPs per country query · 21 September–21 October 2026
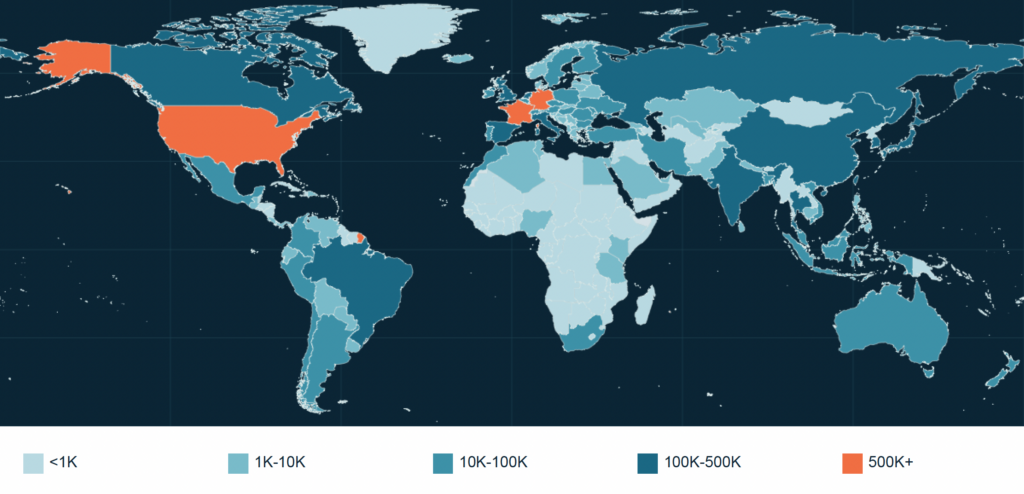
Each country color represents distinct IPs in that country’s 30-day query. Country cohorts are independently deduplicated and may overlap across the window. Sources: Driftnet country cardinalities, Natural Earth geometry, and the map receipt.
Largest country cohorts
Distinct PHP-tagged IPs per country
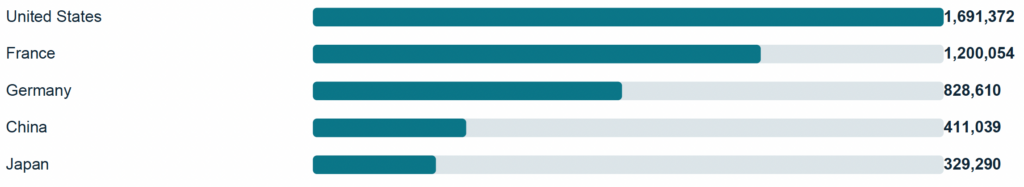
Source: 30-day country IP cardinalities.
Selected routing networks
Distinct PHP-tagged IPs per ASN query
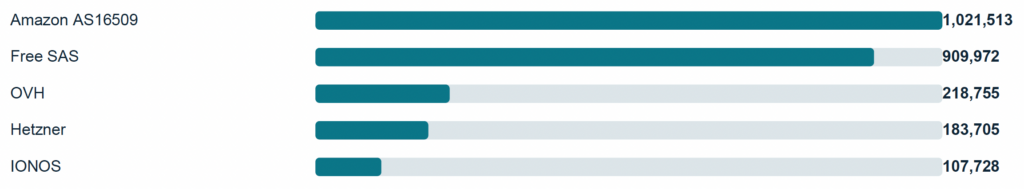
Source: 30-day ASN IP cardinalities. ASNs identify routing networks.
From global signal to actionable portfolios
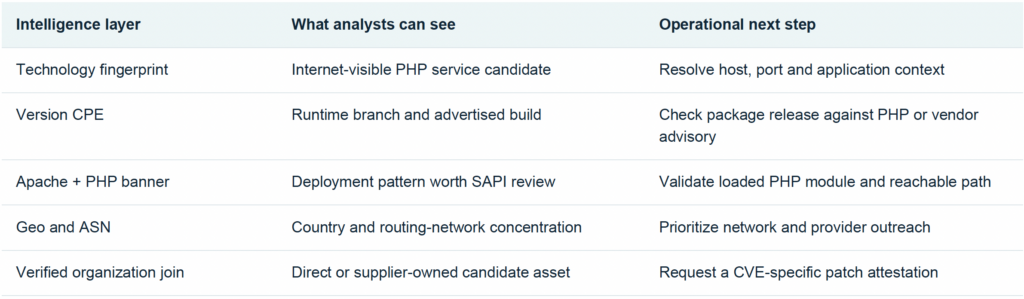
Internet intelligence becomes more useful with each connected layer. Component, version, deployment and network context together help teams build a precise queue for package verification and vendor outreach.
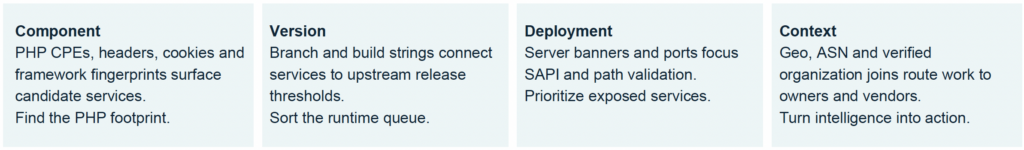
At portfolio scale, preserve each observed host, IP, port, fingerprint, scan time and attribution link. Group the resulting services by direct vendor and validated fourth-party relationship. The result is a service-specific patch request and a reviewable trail from global signal to remediation evidence.
The fix is available now
The PHP project released patched builds for all four maintained branches. Operators should use the fixed build for their branch or a distribution or LTS vendor package explicitly documented to include these CVE fixes. PHP 8.1 and older receive no upstream project updates, but some vendors have issued backports for older package lines.
Upstream fixed releases
Both CVEs are addressed by each release listed below.
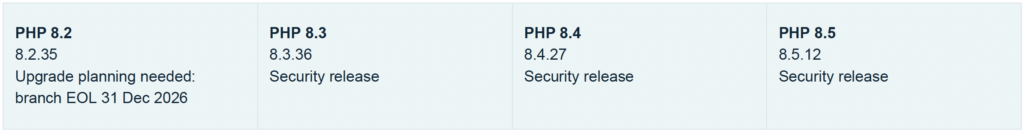
Source: PHP security advisory and release notices. Ubuntu also lists fixed distribution packages, including backports.
Fixed-build fingerprints in the 30-day window
Distinct IPs in each exact upstream CPE query
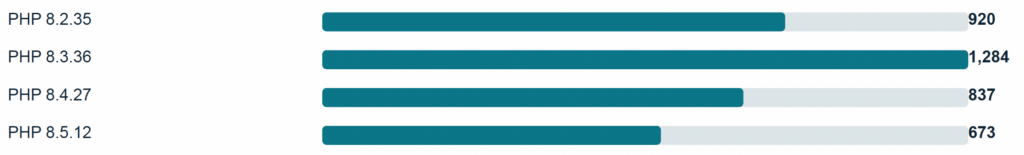
Source: Driftnet exact-build IP cardinalities. Package and provider attestations establish patch state, including vendor backports.
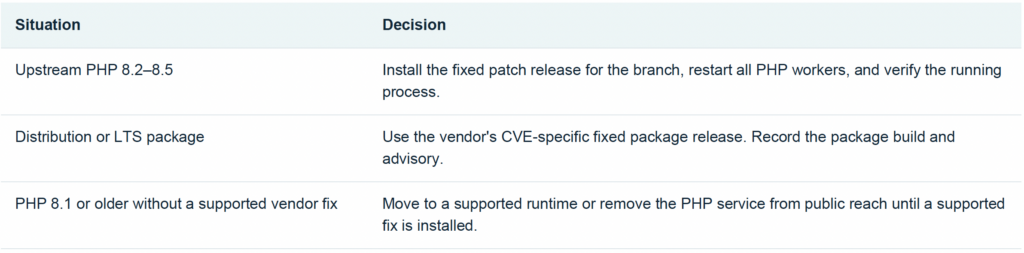
Reference records: CVEDetails 109618 · CVEDetails 109619. Patch versions follow the PHP project release advisory.
Attempted attacks are already being observed
Cloudflare reported attack traffic targeting customers on 21 October and said payloads were changing as attackers tried to bypass protections. That activity raises the urgency of patching and focused log review. The PHP project has confirmed exploitability for specific paths; teams can use runtime and deployment intelligence to prioritize their response.
“Which of our web-facing services actually run an unpatched PHP package?” is the question to answer today.
Prioritize directly reachable Apache mod_php deployments, exposed upload paths, unsupported PHP lines, and high-value applications. Include managed hosting, appliances, containers, and third-party services in the inventory. If a provider operates the runtime, request a CVE-specific patch attestation rather than relying on the application’s version.
Remediate, restart, and confirm
- Inventory every PHP runtime. Search web hosts, images, managed platforms, and embedded products. Collect the SAPI, actual package build, provider, internet reachability, and owner. Use package inventory to establish the active runtime build.
- Install the fixed PHP or vendor package. Target 8.2.35, 8.3.36, 8.4.27, or 8.5.12 upstream. If using a distribution backport, retain the vendor advisory and complete fixed package release as evidence. Plan a supported upgrade for older branches.
- Restart and verify the running service. Restart Apache or every PHP-FPM pool and recycle containers. Verify the active worker’s runtime/package state after restart; a successful package install alone does not refresh long-lived workers.
- Reduce exposure while patching. If a fix cannot be applied immediately, restrict public access or take the PHP service offline. Keep WAF protections in blocking mode where available. The PHP project advises administratively setting session.upload_progress.enabled=0, and for the OOM path memory_limit=-1 with conservative request limits and cgroup containment. These are temporary risk reductions, not a complete fix; test their operational impact and restart workers.
- Hunt and attest. Review web and PHP logs for abnormal multipart requests, repeated fatal errors or memory failures, and PHP worker processes launching shells or download tools. Investigate WAF events and unexpected child processes. Re-scan after remediation, validate origin access controls, and close each asset only with package or provider evidence.
Interim configuration specifics, including where settings must take effect and why RLIMIT_AS/RLIMIT_DATA are unsuitable, come from the PHP advisory. Cloudflare’s WAF research documents observed attempts and reiterates that patching remains necessary.
How to read this brief
All Driftnet charts report distinct IP cardinality for a fixed 30-day window: 21 September 2026, 21:10 UTC to 21 October 2026, 21:10 UTC. The headline uses the exact product-tag:php search linked above. CPE, banner and header charts use their stated independent filters. Country and ASN rows each deduplicate IPs within their own query; rows can overlap across the window and are not summed into the global headline. Patch state is confirmed with package or provider evidence.
How we classified returned versions
The version-status chart groups observed PHP CPEs on released 3.x, 4.x, 5.x, 7.x and 8.0–8.5 branches. Versions below 8.2.35, 8.3.36, 8.4.27 or 8.5.12, plus older branches without an upstream update, enter the below-fix cohort. Exact matches to those four fixed builds enter the fixed cohort. Each cohort is a separate 30-day distinct-IP query; the same IP can appear in both after an upgrade or when it hosts more than one PHP service. A vendor backport can also protect a package that retains an older upstream version number.
- Driftnet 30-day unique-IP query receipt
- Version-status query receipt
- Country heatmap data and geometry receipt
Explore the exact PHP search: https://driftnet.io/search/summary?e=product-tag%3Aphp