Almost no organization operates alone anymore. You work with clients, vendors, suppliers, specialists, and dozens of other partners, all of them third parties with access to sensitive data or a hand in a critical business process. That access is what turns third-party risk management into a board-level concern rather than a procurement checkbox.
Our Global Third-Party Breach Report found that 35.5% of all breaches involved a third party, and that 41.4% of ransomware incidents traced back to a third-party nexus. A data breach at one supplier can move through an entire supply chain before anyone inside your organization sees a single alert.
Security teams have traditionally tried to understand ongoing third-party risks through annual security assessments. That approach has three structural problems, and none of them get better as your vendor count grows.
Why Annual Assessments Leave Gaps
Point-in-time review made sense when vendor portfolios were small, and infrastructure changed slowly. Neither of those conditions holds today.
- Assessments consume weeks. Some questionnaires run to thousands of questions, and many organizations work with hundreds or thousands of third parties. Building, sending, chasing, and reviewing them eats analyst capacity that could go toward remediation, and more tooling alone will not clear that backlog.
- Risk is a snapshot. A vendor’s cyber risk profile can shift in days. Between assessments, a major security incident or a change in security posture can happen with no visibility on your side.
- Answers are only as good as the person writing them. Nothing in a questionnaire guarantees the responses are accurate, honest, or complete.
Does that make risk assessment obsolete? Hardly. Assessments remain the inside-out view of vendor cybersecurity risk, and they are the right tool for baselining maturity, understanding program design, and finding gaps in execution at your most critical third parties. What they cannot do is tell you what changed last Tuesday.
What Is Continuous Monitoring in Vendor Risk Management
Continuous monitoring is the practice of tracking a third party’s externally observable security posture in near real time across the life of the relationship, rather than sampling it once a year. You identify the risks your organization needs to watch, then track them constantly instead of on a calendar.
Continuous monitoring works as the eyes and ears of a mature TPRM program. It supplements assessments with ongoing indicators, surfacing vulnerabilities and posture changes as they happen and sometimes before the vendor notices them internally. The risk categories most worth watching include data security operations, the data security environment, network security, and fourth parties sitting behind your direct suppliers.
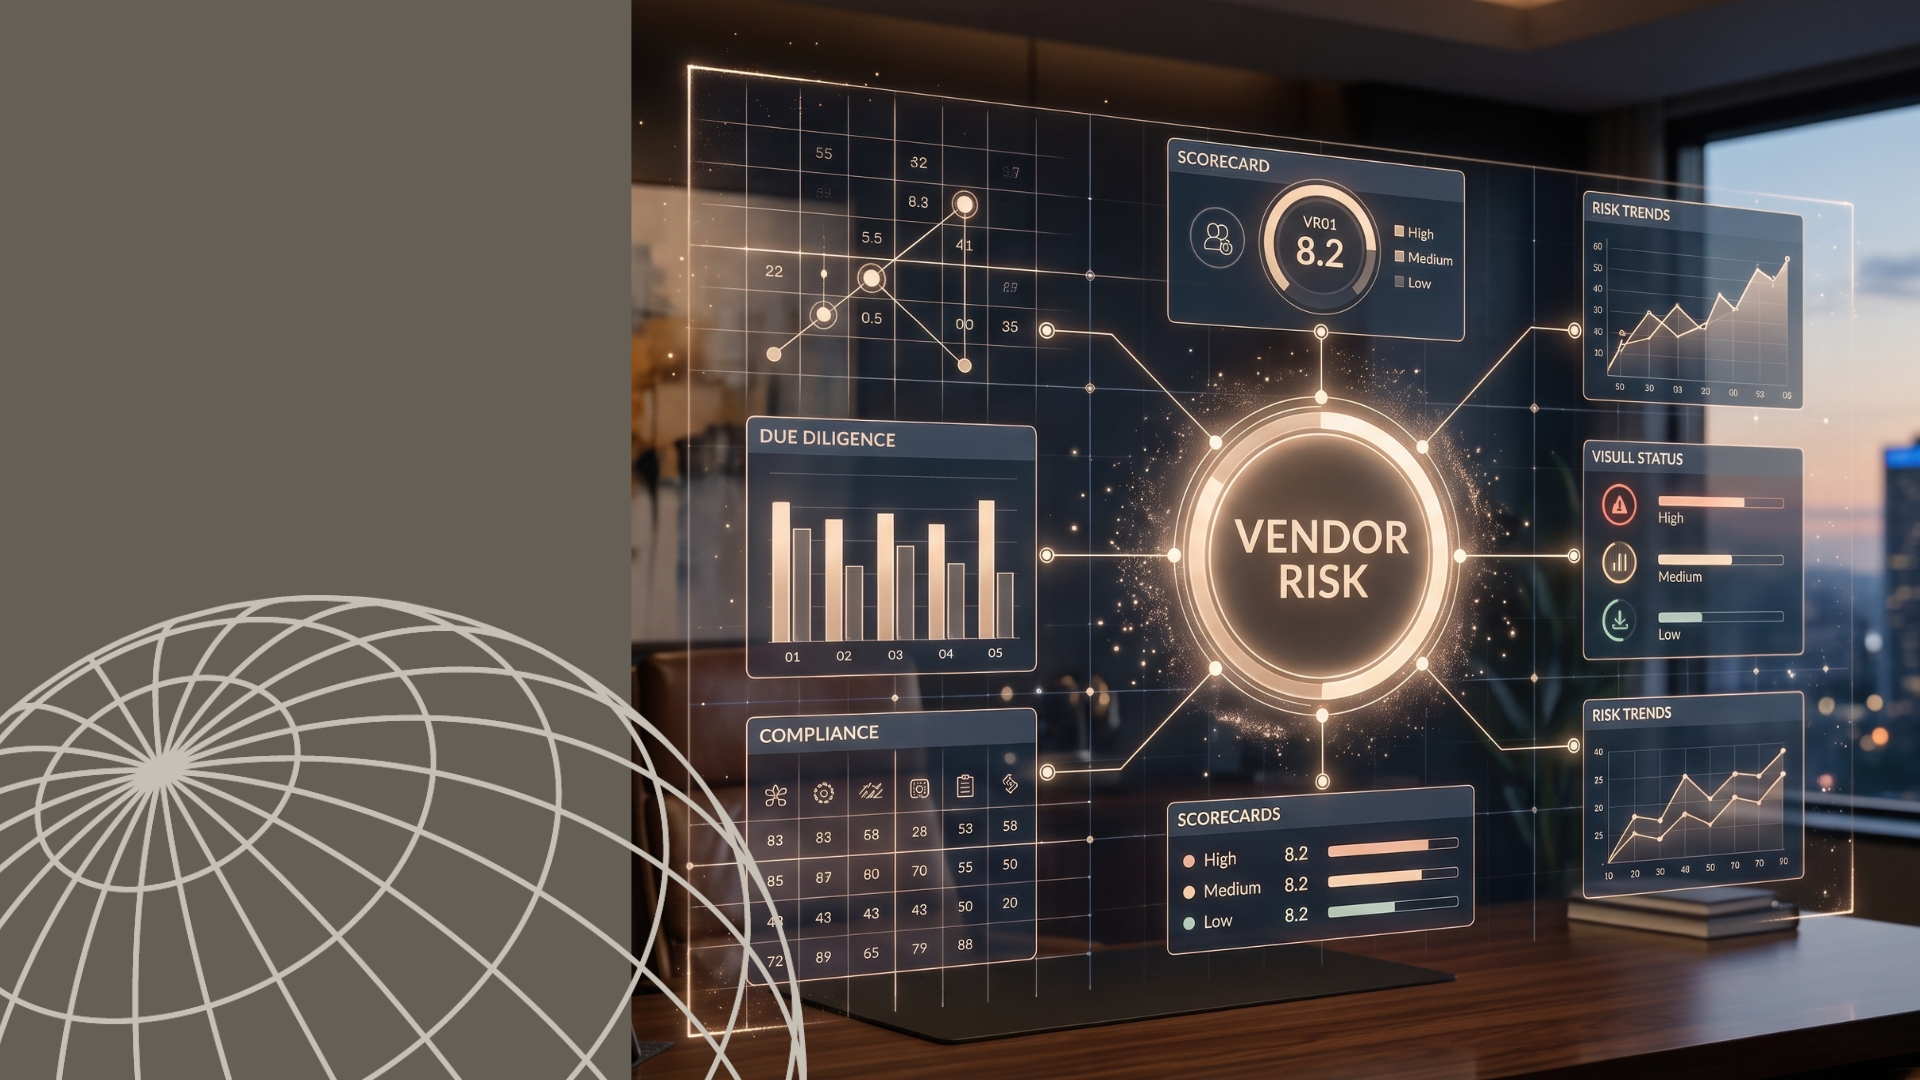
Security ratings make that possible at scale. Ratings give an outside-in view of a vendor’s IT infrastructure, turning scattered technical signals into a score that security teams and business stakeholders can both act on. Our own scanning covers more than 4.1 billion IP addresses and domains daily, backed by 99.9% data accuracy across our proprietary threat intelligence, which is what allows ongoing monitoring to run across a full vendor portfolio rather than a handful of names.
1. Turns Third-Party Risk Exposure From Reactive to Proactive
Continuous monitoring gives you timely insight into a third party’s security posture. By watching movement against risk thresholds, such as a SecurityScorecard security rating or a change in an underlying risk vector, you can trigger an assessment based on what actually changed instead of what the calendar says.
That shift matters more than it sounds. It stops unacceptable risk from sitting inside your third-party ecosystem for months simply because reassessment is not due yet. Proactive teams reassess based on evidence. Reactive teams reassess on anniversary dates. The same logic is replacing point-in-time audits on the compliance side.
2. Allows for Tailored Risk Assessment
No two vendors carry the same exposure, so assessing them identically wastes effort on both sides. Sending the same 300-question form to a payroll processor and a marketing analytics tool inflates cost and delays onboarding without improving your risk picture.
Continuous monitoring data lets you scope each risk assessment to what the evidence says, starting with the types of vendor risk worth monitoring in the first place. When monitoring flags a cluster of web application findings at a single supplier, that assessment focuses there. When another vendor shows a clean, stable profile, a shorter form does the job. Across hundreds of third parties, the time saved compounds quickly.
3. Creates Strategic Assessment Timing
How often should you assess your third parties? Criticality is usually the answer, and vendor tiering is how mature programs get there.
Continuous monitoring lets you set reassessment schedules against real signals. A critical vendor whose rating drops sharply may warrant reassessment twice in one year, regardless of a review three months earlier. A low-risk supplier with a flat risk profile and no new findings may not need reassessment for several years. Both decisions reduce work in the pipeline and reduce cyber risk carried by the organization.
4. Provides an Objective Viewpoint
Continuous monitoring of third-party cybersecurity posture gives objective context to the assessments vendors send back. Are they hitting the patch cadence they claim? Do they scan for malware regularly? Are their certificates current?
Security ratings and risk vector grades answer those questions with externally observable data, which turns questionnaire review into verification rather than trust. Our best practices for questionnaire and evidence collection covers how to build that validation step into your workflow without adding review time.
5. Surfaces Third-Party Risks in Near Real Time
Continuous risk monitoring analyzes a vendor’s externally facing assets on an ongoing basis, reporting each vulnerability into the platform as it appears. Your team walks into an assessment with current data rather than a stale export.
Alert configuration is where this becomes operational. Setting thresholds against your organization’s risk tolerance means the team hears about a newly exposed database or a confirmed security breach at a supplier immediately, not at the next quarterly review. Tuning matters here. An alert for every rating movement creates noise, and that noise gets muted, so most teams start with alerts tied to critical vendors and to the risk vectors that map to their own regulatory obligations.
How to Conduct Continuous Monitoring of Vendor Security Posture
Start with the inventory. Most organizations underestimate their vendor count by a wide margin, and you cannot monitor a supply chain you have not mapped. Automatic vendor discovery closes that gap faster than a procurement spreadsheet ever will.
Tier what you find, then set monitoring depth by tier. Critical third parties get tight alert thresholds and frequent review. Low-criticality suppliers get baseline risk monitoring and exception-only escalation. Document the thresholds so the program survives staff turnover. Our solution guide on shifting from periodic to continuous TPRM walks through the sequencing in more detail.
Then close the loop between monitoring and action. A finding that nobody routes to a vendor conversation is just a dashboard. Route alerts into the systems your team already uses, attach the specific evidence, and track remediation to a date.
Which TPRM Tools Support Continuous Monitoring Instead of Annual Reviews
Any platform worth evaluating should do three things. It should discover the vendors and fourth parties you did not know about, score them against externally observable data, and alert you when something moves.
Our TITAN AI platform handles those functions across four modules. TITAN Watch delivers baseline visibility into vendor security posture and ecosystem discovery through security ratings. TITAN Assess automates third-party risk workflows, and in TITAN AI its questionnaire answers live in the same vendor record as observed data, so gaps are easier to spot. TITAN Secure connects continuous monitoring to active threat intelligence, so teams act on the vendor risks attackers are exploiting now. TITAN MAX pairs the TITAN AI platform with expert analysts who run questionnaires, monitoring, and vendor engagement for teams without the headcount.
Customers running these workflows have reported up to 95% less manual work, and a Forrester Total Economic Impact study of the SecurityScorecard platform (May 2024) found a 75% reduction in the risk of breaches from external third-party attacks. Those outcomes come less from the scanning itself than from what the scanning removes, which is the lag between a vendor’s posture changing and your team knowing about it.
Final Thoughts
Businesses now work with more vendors than at any point in their history, and digital transformation keeps expanding that ecosystem rather than shrinking it. Relying on manual assessments that treat every relationship the same is no longer realistic at that scale.
Continuous monitoring changes the economics of a third-party risk management program. Operational efficiency goes up, dwell time for unaddressed third-party risks goes down, and the program scales with the vendor count rather than breaking under it. Pairing an effective TPRM program with ongoing monitoring is what makes that possible.