Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library

STRIKE
Your Old Threat Hunting Playbook Is Dead: Inside the 633-Server Network Hiding Criminals and Nation-States Alike
Attackers are increasingly renting the infrastructure that hides them instead of building it. SecurityScorecard’s STRIKE Threat Intelligence Team pulled back the curtain on one such operation: a 633-server proxy fleet, leased out to commodity malware crews and, at low confidence, suspected nation-state tenants.
STRIKE Alert
STRIKE News
Video
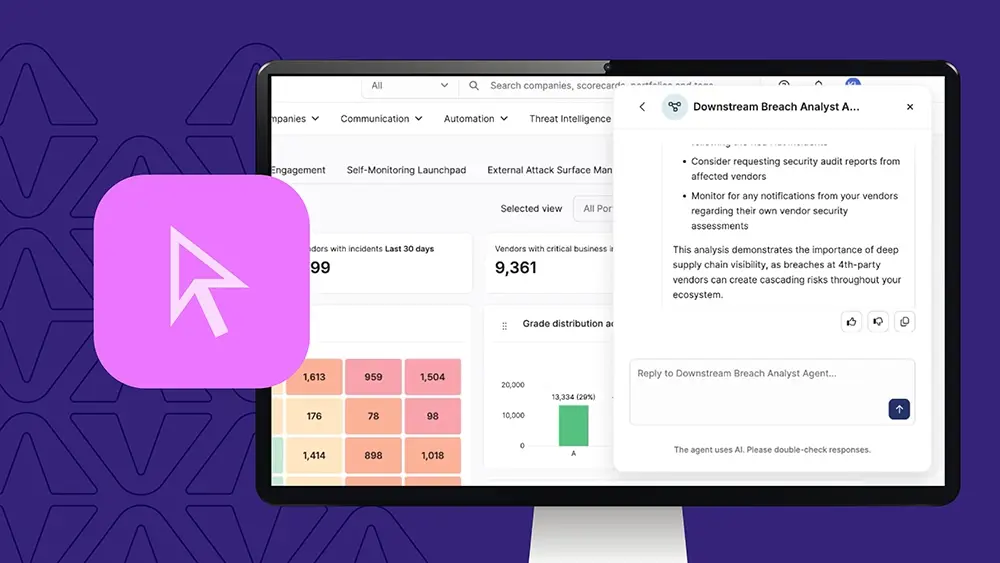
TITAN Watch – Downstream Breach Analyst Agent
This week we look at TITAN AI’s Downstream Breach Analysis Agent — found under the purple sparkle icon in the bottom-right corner — which answers a question that’s normally near-impossible to see: when a major service provider gets breached, which of your vendors are actually exposed?
Demo Tuesdays
Report
The Window to Catch a Vendor Breach Is Closing
IDC Spotlight, sponsored by SecurityScorecard
A 2026 IDC Spotlight shows why point-in-time vendor risk assessments can no longer keep pace – and what continuous, threat-informed TPRM looks like in practice.
As noted in the IDC Spotlight, the 2026 Verizon Data Breach Investigations Report (DBIR) puts third-party involvement in breaches at 48%, up 60% year over year — a sharper climb than the prior two years combined. In IDC’s Third-Party Risk Management Software Survey from August 2026 of 1,226 organizations using TPRM software, when asked to characterize their overall assurance method, only 16.2% describe continuous monitoring — security ratings, attack surface monitoring, and breach and vulnerability intelligence feeds — as the model in use.
Get the full IDC Spotlight to learn:
Why 30.9% of organizations say they are likely to switch TPRM software providers within the next 18 months (IDC’s Third-Party Risk Management Software Survey, August 2026)
Why IDC believes continuous, threat-informed TPRM — built on inside-out telemetry, API-based data collection, and risk scoring tied to business context — will keep displacing point-in-time assessment as the baseline operating model over the next several years, and that the endpoint of this shift is a TPRM life cycle that is more than 90% automated, with analysts reviewing machine-generated findings rather than producing them by hand.
Get the excerpt
メディア掲載
Logistics Today: サイバー対策に自信90%も取引先監視に盲点
Learn more in this resource.
Japanese
メディア掲載
ZDNET Japan: 第3回 エージェンティックAIに求められるセキュリティ戦略の再設計
Learn more in this resource.
Japanese
メディア掲載
TECH+: 第三回 ランサムウェア攻撃に備えよ、企業が築くべきサイバーレジリエンスの新基準:ランサムウェア対策は予測の時代へ―AIとデータ活用が防御を変える
Learn more in this resource.
Japanese
メディア掲載
DZnet Japan: 第2回 なぜ攻撃対象に?エージェンティックAIで広がる攻撃対象領域
Learn more in this resource.
Japanese
寄稿記事
東洋経済オンライン: 「そこが動かなくなると会社全体が止まる」 意外と見えない自社の急所をあぶり出すサイバー対策5つのポイント
Learn more in this resource.
Japanese
メディア掲載
@ITメディア: リスクが見えても人手が足りない米国、リスクが見えてすらいない日本 サプライチェーン防衛の現実
Learn more in this resource.
Japanese
メディア掲載
第1回:エージェンティックAIとは?権限を持つAIがもたらすリスクの拡大
Learn more in this resource.
Japanese
メディア掲載
第二回 ランサムウェア攻撃に備えよ、企業が築くべきサイバーレジリエンスの新基準:サプライチェーン攻撃はなぜ防げない?企業が取るべき「レジリエンス戦略」
Learn more in this resource.
Japanese
メディア掲載
SecurityScorecard「TITAN AI」発表 サードパーティリスク管理をAI駆動に
Learn more in this resource.
Japanese
寄稿記事
「もらい事故でした、申し訳ありません」では済まない、”他社”で発生したサイバー攻撃による被害の厳しい現実
Learn more in this resource.
Japanese
メディア掲載
「第一回:ランサムウェア攻撃に備えよ、企業が築くべき“サイバー レジリエンス”の新基準」 初動・復旧・信頼回復の全体設計 – “防げない”前提で備えよ
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(3)「侵害は社外で始まる」 クラウドや取引先に“潜伏する”脅威と、求められるセキュリティ再設計
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(2)ネットワーク境界防御では防げない、大損害をもたらす「外部侵入口」への対処法
Learn more in this resource.
Japanese
メディア掲載
金融業で考えるサプライチェーンのリスク管理(1)ランサムウェアやDDoSで連鎖被害も? 再々委託先までのリスク管理が不可欠になった訳
Learn more in this resource.
Japanese
Blog
AI Security Cannot Depend on Everyone Slowing Down
Frontier labs are calling for the industry to slow down. Our adversaries didn’t get the memo. The world’s first benchmark for AI in third-party risk management shows what we should be building instead: measurement, not just restraint.

Press
SecurityScorecard website wins Best Technology Website of 2026 from WEBAWARD
SecurityScorecard builds a bespoke, bold, accessible cybersecurity brand experience.
Press
SecurityScorecard Names Sarah Walker President as Company Expands Its Mission for the AI Era
SecurityScorecard Names Sarah Walker President as Company Expands Its Mission for the AI Era
Ebook
The Perfect Scorecard
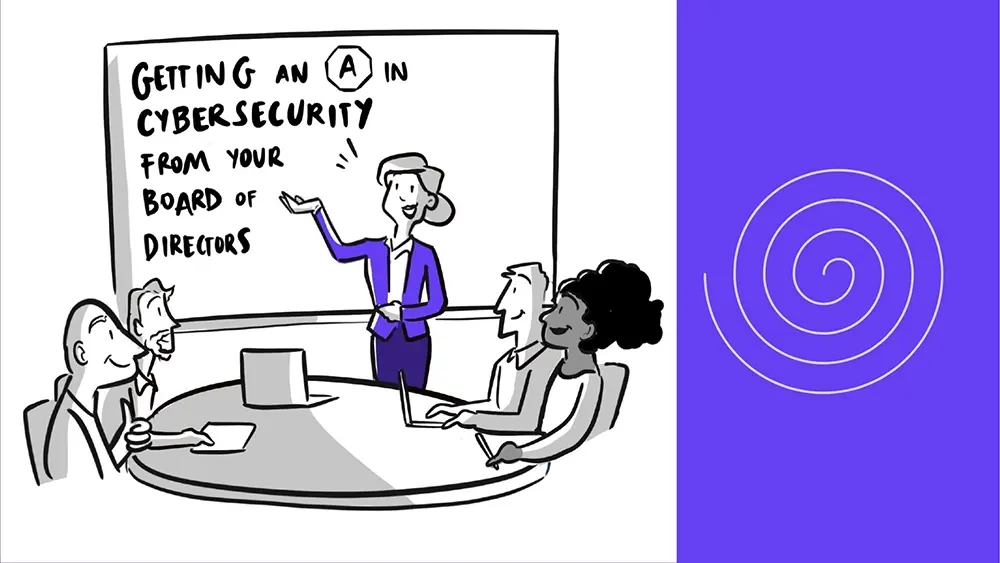
Getting an “A” in Cybersecurity From Your Board of Directors
There’s a growing communications gap between corporate boards and CISOs — and it’s putting companies at risk. This book brings together over a dozen top CISOs, CEOs, board members, and advisors to close the gap, chapter by chapter.
A Carnegie Mellon University survey found that 77% of U.S. board members rarely or never received senior leadership reports on digital privacy or security risk. Cyber risk has since become a top-tier business risk — yet most boards and CISOs still speak different languages. As the book puts it: CISOs are from Mars, and board members are from Venus.
What’s inside
How to tell if you have the right cybersecurity leader and how to test your CISO
A practical playbook for board-CISO communication, built for the boardroom, not the SOC
How to talk about ransomware, cyber insurance, and “wartime” security operations in terms the board understands
A Digital Trust Framework for managing cybersecurity as a business risk, not just an IT problem
Why trust, not just technology, is the foundation of a CISO’s success with the board
Who it’s for
CISOs and security leaders preparing for board conversations, board members and executives responsible for cyber risk oversight, and risk, compliance, and governance teams navigating the CISO-board relationship.
You’ll walk away with insights on how security executives can best communicate to the board, and what board members need to know to assess their security executives.