
Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library
Blog
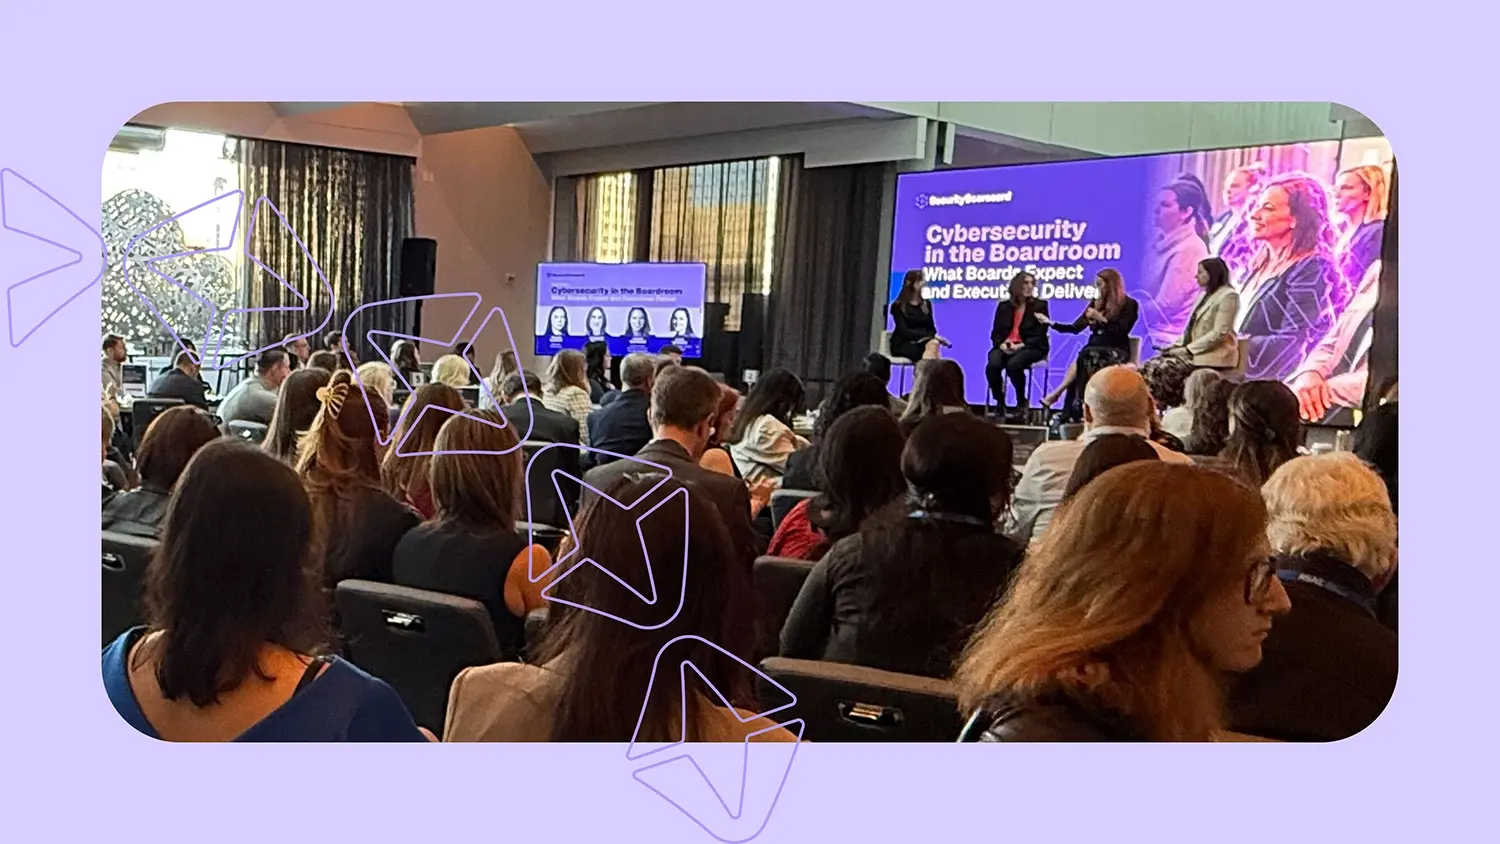
AI Is Reshaping Cyber Risk in 2026: Why Boards Must Take Ownership Now
Cybersecurity leaders must accept a hard truth: AI has already broken the traditional model of defense in 2026. Attackers now operate faster, at lower cost, and at greater scale than most organizations can handle. The only viable response is to rethink security as a continuous, business-driven risk function. This shift defined a recent panel at
Blog
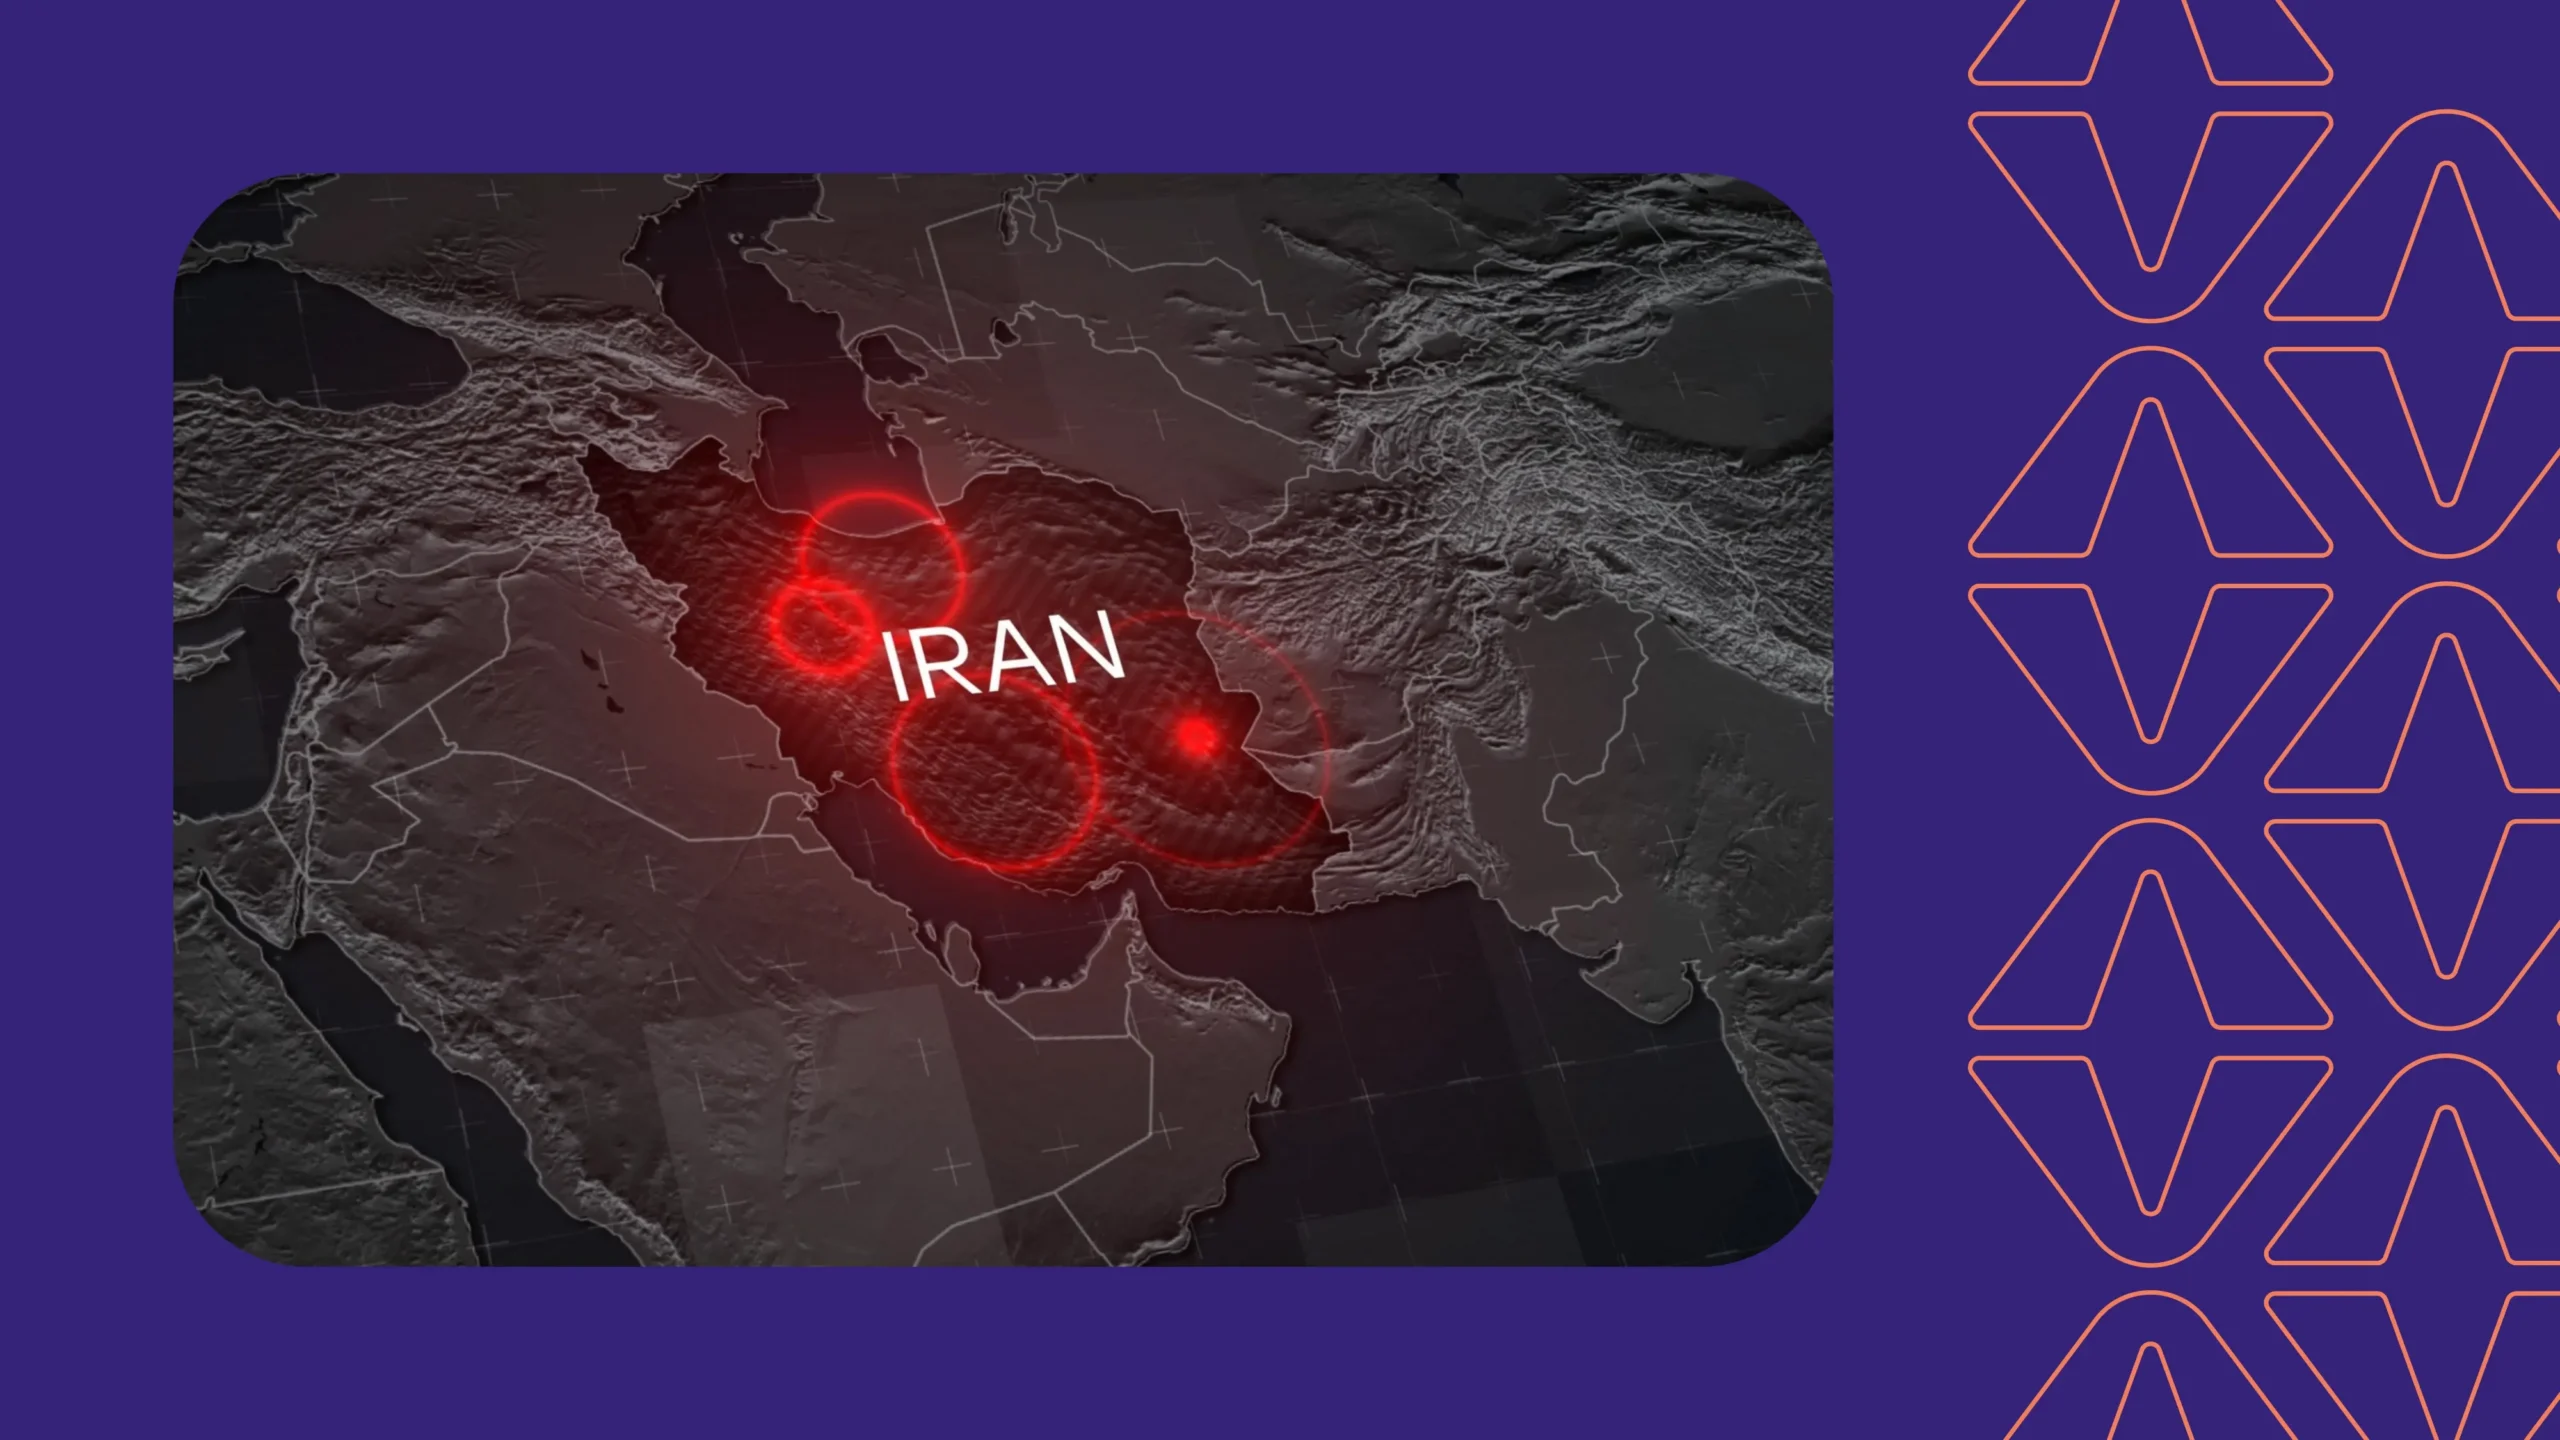
Iran Conflict and the Expanding Cyber Front: What Government Leaders Need to Know
When conflict escalates in the Middle East, the battlefield is never limited to geography. It extends into energy grids, government networks, transportation systems, and financial infrastructure. The current war involving Iran is no exception. While missiles and airstrikes dominate headlines, the parallel cyber dimension may prove equally consequential, particularly for regional governments, critical infrastructure operators,
Blog
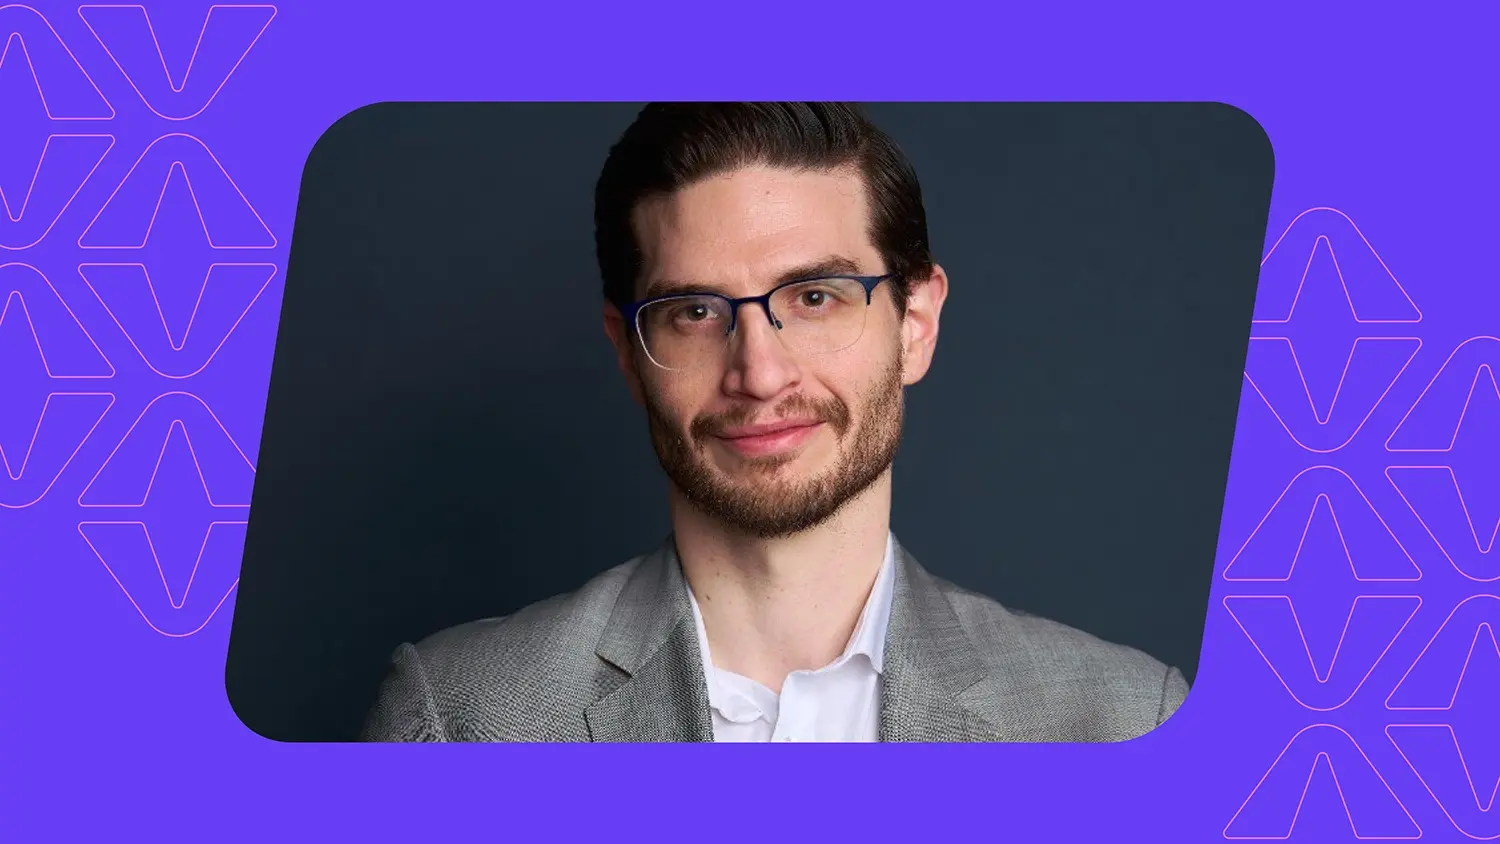
SecurityScorecard Appoints Dean Sysman to Board of Directors
SecurityScorecard today announced that Dean Sysman, Co-Founder and Executive Chairman of Axonius, has joined its Board of Directors as an independent director. Dean is one of the most respected builders in cybersecurity today. Sysman co-founded Axonius and scaled it into a leader in cyber asset management. The platform helps organizations maintain accurate asset inventories, reduce
Blog
What Is a Honeypot in Cybersecurity?
Learn what a honeypot is in cybersecurity, how it works to detect threats, and why security teams use honeypots to gather attacker intelligence.
Blog
What Is the CAIQ Questionnaire? A Clear Guide
The CAIQ questionnaire documents a cloud provider’s security controls. Learn how it works and how to finish it without the grind.
Blog
RSAC 2026 Talk: Transforming Third-Party Risk Management From Compliance Checkboxes to Security Resilience
The traditional approach to managing supply chain risk is broken. For years, organizations have relied on annual questionnaires and static attestations to “check the box” for compliance. However, as SecurityScorecard CISO Steve Cobb highlighted in his RSAC 2026 talk, “The Outside-In Advantage: Modernizing TPRM with AI and Threat Intelligence,” 90% of security practitioners lack confidence
Blog
SecurityScorecard and Dataminr Partner to Deliver Preemptive Cyber Defense for the Enterprise
Combining third party risk and external attack surface management with client-tailored threat intelligence to help organizations stop threats before they strike.
Blog
Supply Chains Are the New Front Line for Cyber Resilience
Supply chains are the top cyber resilience challenge in 2026. See how continuous monitoring and threat-informed vendor risk management protect your operations.
Press
SecurityScorecard Unveils TITAN AI: A New Era of Threat-Informed Third-Party Risk Management
TITAN AI turns AI-powered automation and advanced threat intelligence into measurable supply chain resilience
Blog
How to Reduce Security Questionnaire Fatigue
Answering the same security questionnaires is wearing your team out. Reduce security questionnaire fatigue with these fixes.
Research
INFORME DE TENDENCIAS EN CIBERSEGURIDAD DE LA CADENA DE SUMINISTRO 2026
La paradoja del riesgo de terceros: La confianza aumenta mientras la exposición crece
La brecha entre la seguridad percibida y la protección real se está ampliando. Si bien las organizaciones tienen más confianza que nunca en su capacidad para superar una brecha de seguridad, los datos subyacentes revelan una realidad diferente: los ecosistemas de cadena de suministro se están expandiendo hasta cientos de miles, mientras que la supervisión interna sigue siendo peligrosamente estancada.
Para comprender cómo los líderes globales de ciberseguridad están navegando esta paradoja del riesgo de terceros, SecurityScorecard encuestó a cientos de profesionales que gestionan el riesgo de proveedores. El informe de 2026 destaca la necesidad urgente de ir más allá de las evaluaciones manuales y puntuales hacia una defensa automatizada e informada por amenazas.
Hallazgos clave del informe 2026:
La Paradoja de la Confianza: El 90% de los líderes confía en que su empresa podría continuar operaciones durante una brecha de un proveedor, aunque el 86% expresa una profunda preocupación por los riesgos de la cadena de suministro.
Puntos Ciegos Evidentes: El 78% de las organizaciones admite que sus programas internos de ciberseguridad cubren menos del 50% de su ecosistema total de proveedores.
Amenazas Impulsadas por IA: Los líderes ahora clasifican las amenazas impulsadas por IA como su principal riesgo en la cadena de suministro, sin embargo, el 67% todavía depende de auditorías de seguridad estáticas para la evaluación
El Retraso en la Remediación: Debido a la dependencia de la comunicación manual como correos electrónicos y llamadas telefónicas, el 60% de las organizaciones tarda 8 días o más en remediar problemas de alta gravedad.
Las prácticas de seguridad de la cadena de suministro de ayer no son suficientemente sólidas para las amenazas de hoy. Descargue el informe completo para descubrir cómo sus pares están gestionando sus ecosistemas de enésimas partes y aprenda cómo avanzar en la curva de madurez de su organización con monitoreo continuo impulsado por IA.
White Papers
The TPRM Evolution: From Checkbox to Continuous Intelligence
Modernizing Third-Party Risk with Threat Intelligence and AI
For decades, TPRM has been a static, moment-in-time exercise. But today, the legacy model of massive spreadsheets and six-week wait times is a dangerous operational liability. As Nth-party dependencies grow, a single vulnerability buried deep in a software library can trigger a global outage in seconds.
While 90% of security leaders are confident in their resilience, only 22% of internal programs cover more than half of their total vendor ecosystem. To close this gap, organizations must transition from reactive box-ticking to continuous intelligence—where real-time data and predictive analytics replace the obsolete annual audit.
Access this guide to discover:
The Three Pillars of Modern TPRM: How to integrate real-time telemetry, adversary-focused signals, and AI-driven orchestration to move beyond manual oversight.
Collapsing Onboarding Timelines: How AI-driven automation and auto-fill logic can reduce vendor onboarding from 42 days to just 42 hours.
Threat Intelligence as a Force Multiplier: Leveraging outside-in and inside-out views to identify zero-day exposures and concentration risks in real-time.
The Agentic Shift: Moving toward AI Agents autonomously monitoring risks and initiating remediation requests without human intervention.
Research
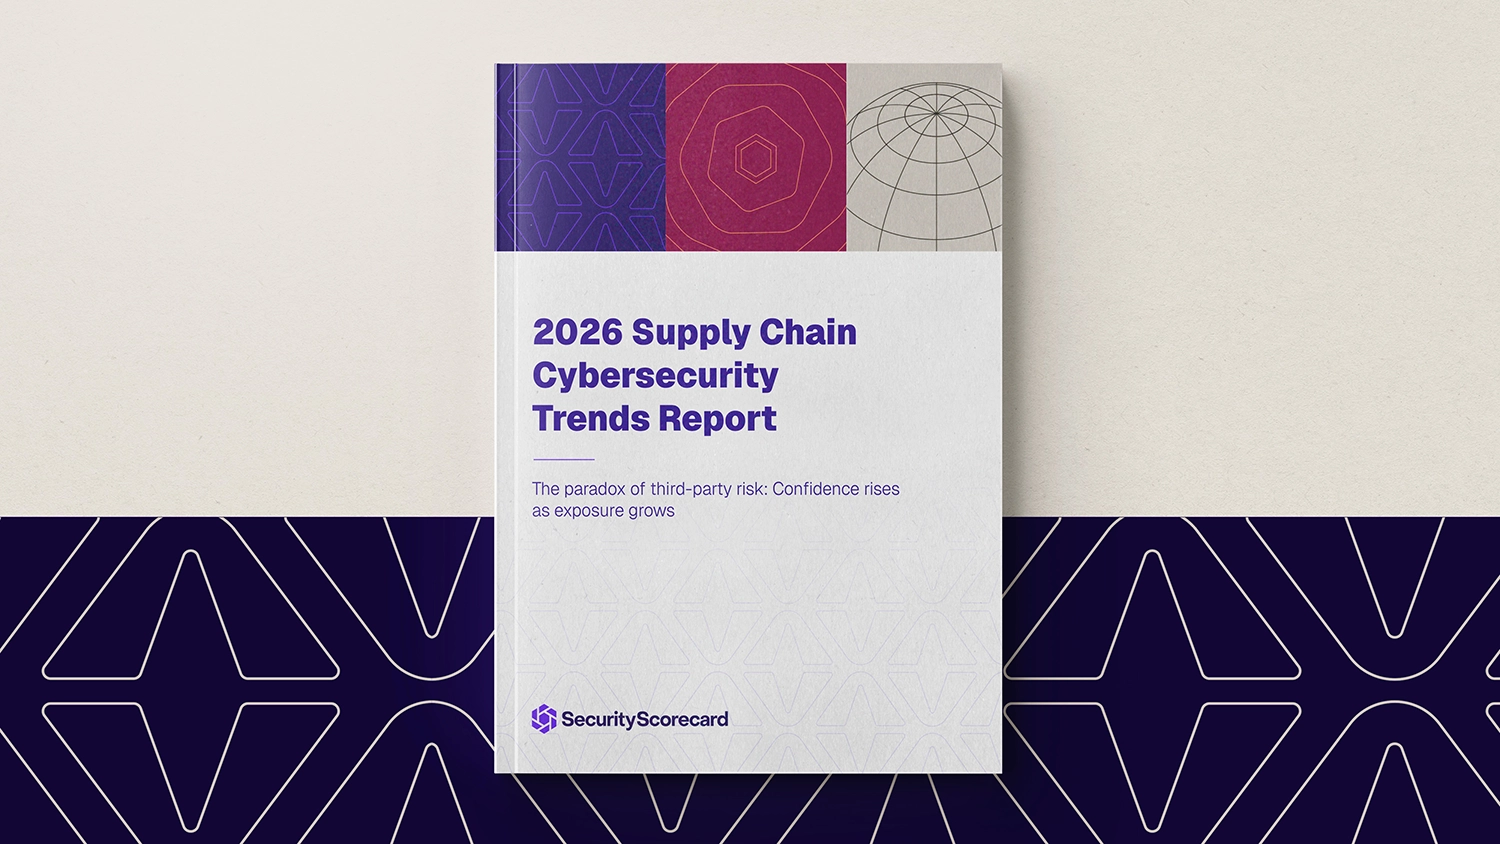
2026 Supply Chain Cybersecurity Trends Report
The paradox of third-party risk: Confidence rises as exposure grows
The gap between perceived security and actual protection is widening. While organizations are more confident than ever in their ability to weather a breach, the underlying data reveals a different reality: supply chain ecosystems are expanding into the hundreds of thousands, yet internal oversight remains dangerously flat.
To understand how global cybersecurity leaders are navigating this third-party risk paradox, SecurityScorecard surveyed hundreds of professionals managing vendor risk. The 2026 report highlights an urgent need to move beyond manual, point-in-time assessments toward automated, threat-informed defense.
Key findings from the 2026 report include:
The Confidence Paradox: 90% of leaders are confident their business could continue operations during a vendor breach, even though 86% express deep concern about supply chain risks.
Glaring Blind Spots: 78% of organizations admit their internal cybersecurity programs cover less than 50% of their total vendor ecosystem.
AI-Driven Threats: Leaders now rank AI-driven threats as their #1 supply chain risk, yet 67% still rely on static security audits for assessment.
The Remediation Lag: Due to reliance on manual communication such as emails and phone calls, 60% of organizations take 8 days or more to remediate high-severity issues.
Yesterday’s supply chain security practices aren’t strong enough for today’s threats. Download the full report to discover how your peers are managing their nth-party ecosystems and learn how to move your organization up the maturity curve with AI-driven, continuous monitoring.
Blog
What Is Application Security and Best Practices for it?
Learn what application security is and why your vendors’ AppSec gaps become your risk. Learn how continuous monitoring protects your supply chain.
Research
The State of South Korea’s Cyber Supply Chain Risk
Learn more in this resource.
Press
SecurityScorecard Expands Global Presence in South Korea
SEOUL, March 11, 2026 – SecurityScorecard, the global leader in threat-informed third-party risk management (TPRM), today announced it is expanding its operations into South Korea and outlined plans to expand its market strategy and customer support across the South Korean market. The move reflects the increasing importance of supply chain cybersecurity as global enterprises, regulators,
Blog
What Is a Supply Chain Attack?
Learn how a supply chain attack works, why it’s so dangerous, and what security measures can help protect your organization from hidden threats.
Supply Chain Cyber Risk
Threat-Informed TPRM
Blog
What the Mississippi Ransomware Attack Means for Healthcare and How to Protect Critical Infrastructure
A ransomware attack shut down clinics across Mississippi. Learn how healthcare and critical infrastructure can prevent supply chain-driven cyber disruptions.
Case Studies
Insurance Authority of Hong Kong
How the Insurance Authority of Hong Kong Strengthened Cyber Visibility and Risk Posture with SecurityScorecard
Press
SecurityScorecard Adds Former Maryland Gov. Larry Hogan to Advisory Board
SecurityScorecard, the global leader in threat-informed third-party risk management (TPRM), today announced that Former Maryland Governor Larry Hogan has joined the company’s Advisory Board.
Blog
What Are the Real Security Risks of Agentic AI and OpenClaw?
SecurityScorecard’s STRIKE Threat Intelligence team examines exposed OpenClaw deployments and the broader security risks of agentic AI, including remote code execution vulnerabilities, prompt injection, and the security controls organizations must implement now.