
Resources
Cybersecurity white papers, data sheets, webinars, videos and more
Resource Library

Press
SecurityScorecard In The News February 2026
Catch up on SecurityScorecard press coverage from February 2026
Press
SecurityScorecard In The News January 2026
Catch up on SecurityScorecard press coverage from December 2025

Press
SecurityScorecard In The News Q4 2025
Catch up on SecurityScorecard press coverage from Q4 2025
Press
SecurityScorecard In The News December 2025
Catch up on SecurityScorecard press coverage from December 2025
Data Sheet
The TITAN AI Platform Corporate Overview
SecurityScorecard introduced an industry-first customer transformation model, Supply Chain Resilience Journey, designed to help organizations understand exactly where their TPRM program stands today and how to advance it. The journey maps four progressive stages: Basic Diligence, Periodic TPRM, Continuous TPRM, and Threat-Informed TPRM.
Data Sheet
TITAN Watch: Foundational Visibility and a clear understanding risk in your vendor ecosystem
The TITAN Watch offering within SecurityScorecard’s TITAN AI platform helps organizations monitor risk in their extended supply chain and gain a clear understanding of their security posture.
Data Sheet
TITAN Secure: Threat-Informed Third-Party Risk Management
TITAN Secure provides a revolutionary threat-informed solution that transforms how organizations identify, prioritize, and act on cyber risks across their supply chain.
Data Sheet
TITAN MAX: Managed Services for Cyber TPRM Outcomes
TITAN MAX is a TPRM force multiplier that injects people, process, and technology on behalf of customers.
Data Sheet
TITAN Assess: AI-Powered Security Questionnaire Automation & Compliance
Transform your security assessment lifecycle from a manual, point-in-time hurdle into a continuous, AI-accelerated workflow. By combining proprietary RespondAI technology with expert human verification, TITAN Assess automates the manual workload associated with security questionnaires and compliance documentation. TITAN Assess eliminates the visibility gap by bringing together self-reported vendor data and objective security ratings, ensuring total reliability with human verified accuracy.
Data Sheet
Delivering a modern, threat-informed approach to TPRM
SecurityScorecard uses artificial intelligence and threat intelligence to continuously manage, detect, and respond to global supply chain risk. Our products and services deliver the
full spectrum of modern TPRM outcomes while strengthening resilience. Reduce compliance burden and administrative friction, drive measurable risk reduction, and prioritize the most critical exposures with TITAN AI.
Data Sheet
TITAN AI Data Overview
With 10+ years of third party data collection expertise, 12M organizations rated, and 99.9% proprietary data, SecurityScorecard represents the leading provider of telemetry on third, fourth and nth-party vendor risk management.
Data Sheet
Unrivaled Global Telemetry for Proactive Defense and Threat Hunting
The Security Scorecard Internet Intelligence API is a massive-scale infrastructure intelligence engine designed for the world’s most advanced security teams. By integrating the high-fidelity scanning technology with Security Scorecard’s industry-leading attribution, we provide the raw telemetry required to identify, hunt, and remediate threats across the entire global attack surface.
Solution Guide
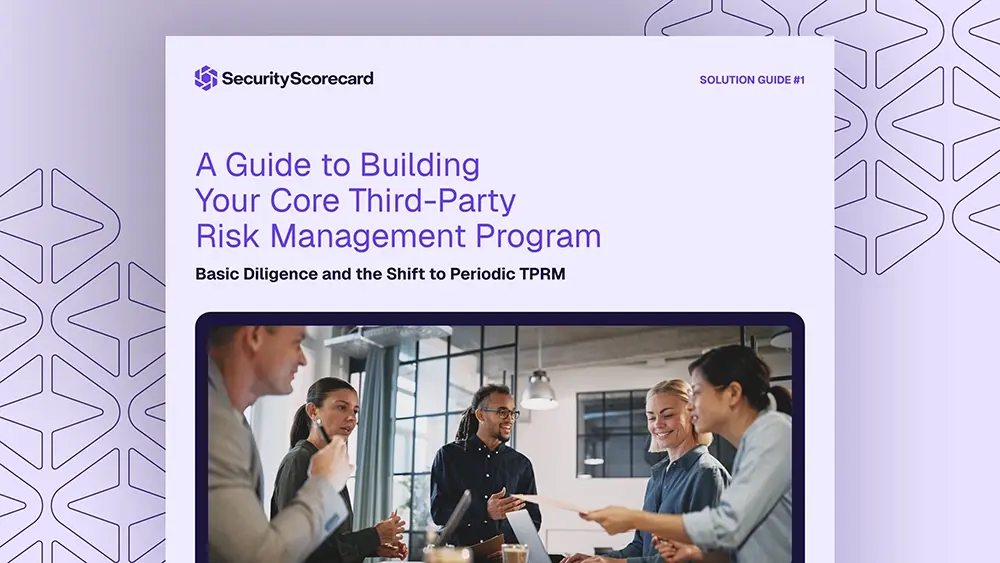
A Guide to Building Your Core Third-Party Risk Management Program
This guide is your blueprint that helps organizations move from manual spreadsheets and ad-hoc security checks to policy-driven Third-Party Risk Management (TPRM). Learn about the core practices of Basic Diligence and how to transition to a scalable Periodic TPRM program.
Inside, you will master the three essential steps to building a repeatable and scalable program:
Formalize Risk Governance: Establish a policy-driven program and an audit-ready system of record, ensuring continuous compliance and liability protection.
Implement Risk-Based Tiering: Strategically categorize vendors to focus high-value technical staff on critical partners, preventing low-risk ‘noise’ from clogging your pipeline.
Standardize the Assessment Workflow: Implement structured digital workflows to replace manual follow-ups, achieving a standard 2-week assessment cycle time and eliminating backlogs
Download the solution guide to learn about the core practices to achieve audit-readiness and operational scale without increasing headcount.
Solution Guide
Una Guía para Construir su Programa Principal de Gestión de Riesgos de Terceros
Esta guía es su modelo de referencia que ayuda a las organizaciones a pasar de hojas de cálculo manuales y controles de seguridad ad hoc a una Gestión de Riesgos de Terceros (TPRM, por sus siglas en inglés) basada en políticas. Conozca las prácticas fundamentales de la Diligencia Básica y cómo realizar la transición hacia un programa TPRM Periódico y escalable.
En su interior, dominará los tres pasos esenciales para construir un programa repetible y escalable:
Formalizar la Gobernanza del Riesgo: Establezca un programa basado en políticas y un sistema de registro listo para auditorías, garantizando el cumplimiento continuo y la protección frente a responsabilidades.
Implementar la Categorización Basada en Riesgo: Clasifique estratégicamente a los proveedores para concentrar al personal técnico de alto valor en los socios críticos, evitando que el “ruido” de bajo riesgo obstruya su proceso.
Estandarizar el Flujo de Trabajo de Evaluación: Implemente flujos de trabajo digitales estructurados para reemplazar el seguimiento manual, logrando un ciclo de evaluación estándar de 2 semanas y eliminando los retrasos acumulados.
Descargue la guía de solución para conocer las prácticas fundamentales que permiten alcanzar la preparación para auditorías y la escala operativa sin aumentar el número de empleados.
Blog
What Is Network Security?
Learn what network security is, why it matters, and how to protect your organization from cyber threats with proven strategies and tools.
Blog
What Are Indicators of Compromise (IOCs)?
An indicator of compromise (IOC) is forensic evidence of a breach. Learn the types of IOCs, how they differ from IOAs, and how teams use them.
Blog
Introducing SecurityScorecard AI Agents
Transform your vendor risk management with new SecurityScorecard AI Agents. Learn how to automate security questionnaire management, gain real-time threat insights, and accelerate remediation to stay ahead of emerging cyber threats.
TITAN AI Agents
Unlock New Levels of Productivity with AI
Learn more in this resource.
Blog
What Is a DNS Sinkhole?
Learn what a DNS sinkhole is, how it blocks malicious traffic, and why security teams use sinkholing to neutralize botnets and protect their networks.
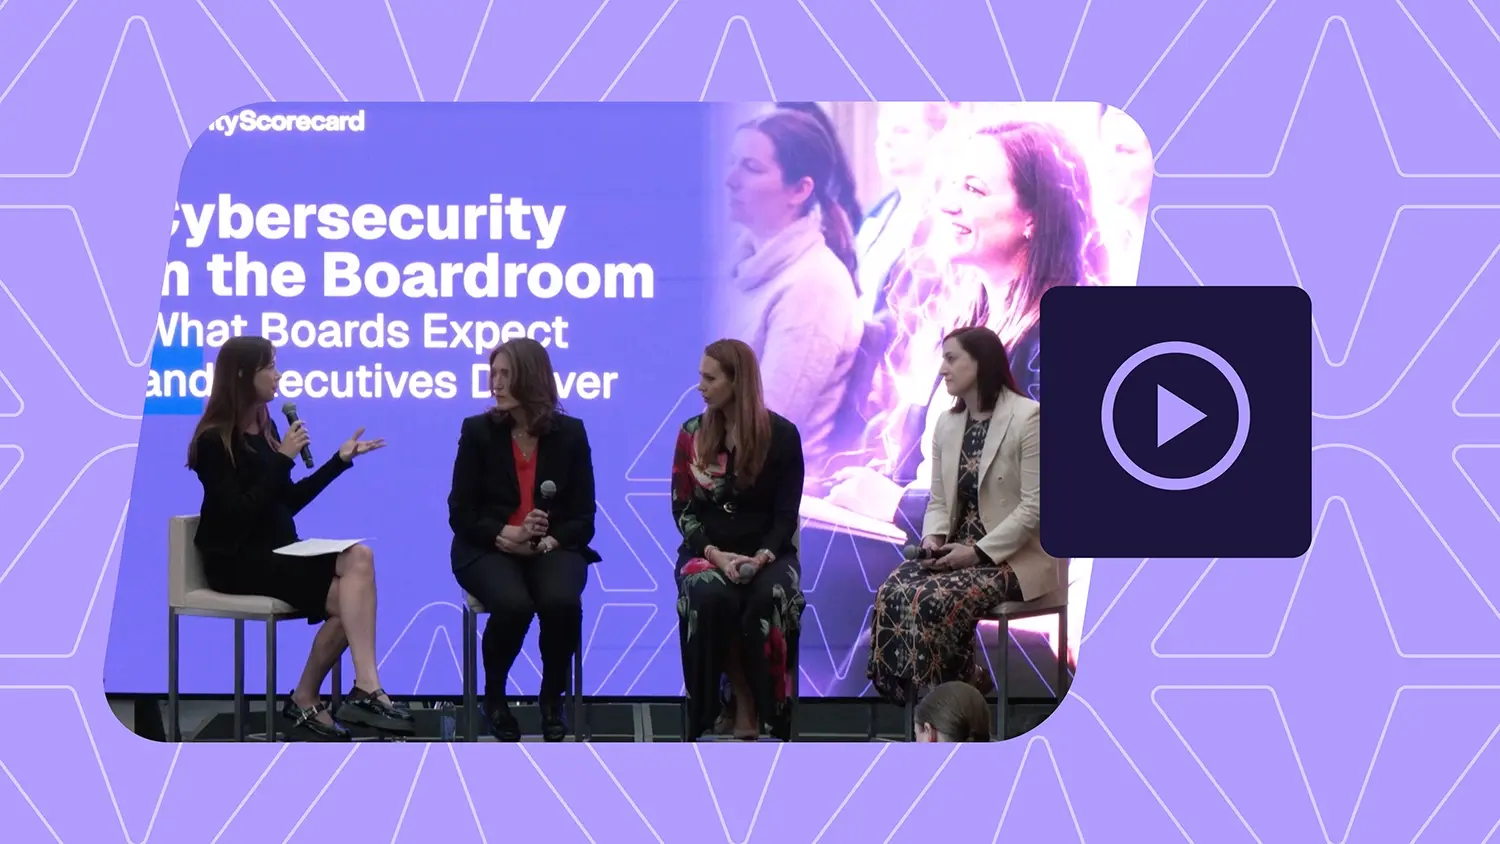
Webinars
Women in Cybersecurity Panel Event RSAC 2026
Learn more in this resource.
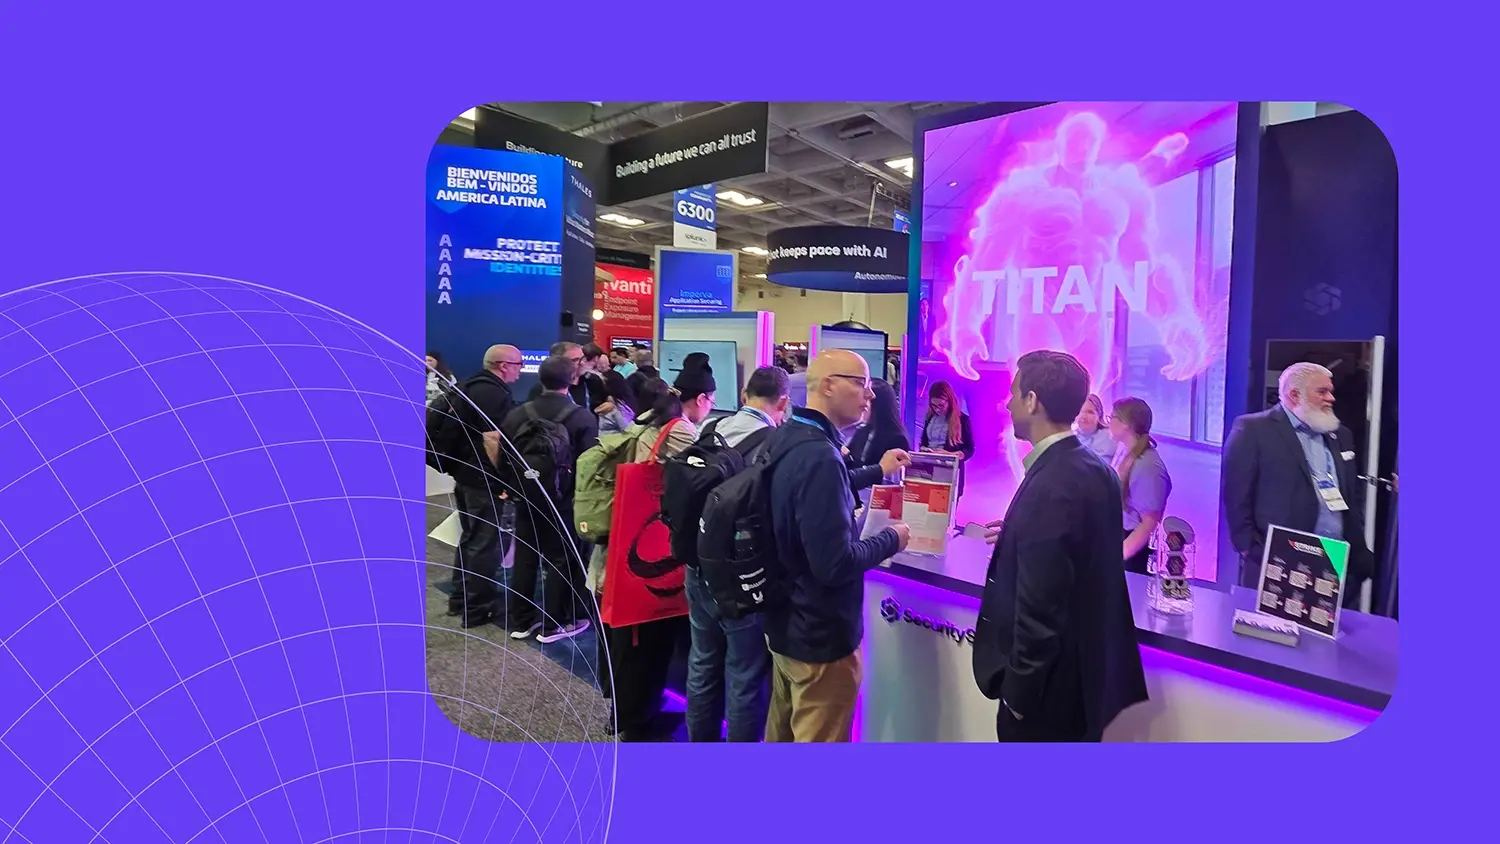
Blog
RSAC 2026 Recap: What Did RSAC 2026 Reveal About the Future of TPRM? SecurityScorecard’s TITAN AI Sets the Pace
CEO and Co-Founder Dr. Aleksandr Yampolskiy, CISO Steve Cobb, and SecurityScorecard leaders joined chief information security officers (CISOs), partners, and industry experts at RSAC 2026 to discuss how AI, threat intelligence, and continuous monitoring are reshaping third-party risk management (TPRM). RSAC 2026 reinforced a growing gap between how organizations manage third-party risk and how that